


teo_rz
Потребител
-
Регистрация
-
Последно онлайн
-
teo_rz обнови профилната си снимка
-
Оххххххх сега пък ми казват, че сам разпращал такива глупости в чата на Фейсбук .... @[smiley: Oh%20No%20She%20Didn%27t: [F/1/446]] *:-]* Your friend just sent you a Smiley. Go to http://digtrivia.com?partner=ZNzfb001_ZNzfb015&5M1L3
-
трябва ли ти ? само един архивирах, че нямат събиранка всички (махам линка да не се набута някой) предположих изтрих 653 файла да видим сега ще се появят ли пак ...
-
ами нищо ново не се е създало но старите си седят My Documents.exe Pictures.exe Games.exe Music.exe. Мисля да пусна в търсачката *.* и да ги сортирам по размер тъй като всичките са с един размер да им видя датите и да ги изтрия...
-
ето log1.txt
-
ComboFix 11-01-13.01 - teo 01.2011 г. 18:42:43.1.2 - x64 Microsoft Windows 7 Ultimate 6.1.7600.0.1251.359.1033.18.2046.1157 [GMT 2:00] Running from: c:\users\teo\Desktop\ComboFix.exe SP: Windows Defender *Enabled/Outdated* {D68DDC3A-831F-4fae-9E44-DA132C1ACF46} . ((((((((((((((((((((((((((((((((((((((( Other Deletions ))))))))))))))))))))))))))))))))))))))))))))))))) . c:\users\Default\AppData\Local\Application Data.exe c:\users\Default\AppData\Local\Local.exe c:\users\Default\AppData\Local\Settings.exe c:\users\Default\AppData\Roaming\Application Data.exe c:\users\Default\AppData\Roaming\Microsoft\Microsoft.exe c:\users\Default\AppData\Roaming\Roaming.exe c:\users\Default\Default User.exe c:\users\Default\Default.exe c:\users\Public\Public.exe c:\users\teo\AppData\Local\Application Data.exe c:\users\teo\AppData\Local\Local.exe c:\users\teo\AppData\Roaming\Microsoft\Windows\Recent\Recent.pif c:\users\teo\AppData\Roaming\Roaming.exe c:\users\teo\teo.exe c:\windows\SysWow64\klipxm32.dll c:\windows\XSxS . ((((((((((((((((((((((((( Files Created from 2010-12-14 to 2011-01-14 ))))))))))))))))))))))))))))))) . 2011-01-14 16:49 . 2011-01-14 16:49 -------- d-----w- c:\users\Default\AppData\Local\temp 2011-01-14 13:38 . 2011-01-14 13:38 -------- d-----w- C:\antivir 2011-01-14 13:34 . 2011-01-14 13:34 -------- d-----w- c:\program files\trend micro 2011-01-13 22:46 . 2011-01-13 22:46 -------- d-----w- c:\users\teo\AppData\Roaming\Malwarebytes 2011-01-13 22:46 . 2011-01-13 22:46 -------- d-----w- c:\programdata\Malwarebytes 2011-01-13 22:46 . 2010-12-20 16:09 38224 ----a-w- c:\windows\SysWow64\drivers\mbamswissarmy.sys 2011-01-13 22:46 . 2011-01-13 22:46 -------- d-----w- c:\program files (x86)\Malwarebytes' Anti-Malware 2011-01-13 22:46 . 2010-12-20 16:08 24152 ----a-w- c:\windows\system32\drivers\mbam.sys 2011-01-13 09:18 . 2011-01-13 10:08 -------- d-----w- c:\program files (x86)\Games 2011-01-06 08:56 . 2011-01-09 11:04 -------- d-----w- c:\users\teo\AppData\Roaming\Hardcore 2011-01-05 16:13 . 2011-01-05 16:13 -------- d-----w- c:\program files (x86)\ASIO4ALL v2 2011-01-05 16:13 . 2006-06-20 08:56 225280 ----a-w- c:\windows\SysWow64\rewire.dll 2011-01-05 16:12 . 2009-09-15 09:14 1554944 ----a-w- c:\windows\SysWow64\vorbis.acm 2011-01-05 16:12 . 2011-01-05 16:13 -------- d-----w- c:\program files (x86)\VstPlugins 2011-01-05 16:12 . 2011-01-05 16:12 -------- d-----w- c:\program files (x86)\Outsim 2011-01-05 16:10 . 2011-01-05 16:12 -------- d-----w- c:\program files (x86)\Image-Line 2011-01-04 13:24 . 2011-01-05 19:23 561152 ----a-w- c:\users\Default\AppData\Roaming\Microsoft\Windows\Printer Shortcuts\PrintHood.exe 2011-01-04 13:24 . 2011-01-05 19:22 561152 ----a-w- c:\users\Default\AppData\Roaming\Microsoft\Windows\Network Shortcuts\NetHood.exe 2011-01-04 13:21 . 2011-01-05 19:26 561152 ----a-w- c:\users\Default\AppData\Roaming\Microsoft\Windows\Templates\Templates.bat 2011-01-04 13:21 . 2011-01-05 19:12 561152 ----a-w- c:\users\Default\AppData\Roaming\Microsoft\Windows\Start Menu\Programs\Maintenance\Maintenance.exe 2011-01-04 13:21 . 2011-01-05 19:11 561152 ----a-w- c:\users\Default\AppData\Roaming\Microsoft\Windows\Start Menu\Programs\Accessories\System Tools\Tools.exe 2011-01-04 13:20 . 2011-01-05 19:10 561152 ----a-w- c:\users\Default\AppData\Roaming\Microsoft\Windows\Start Menu\Programs\Accessories\Accessibility\Accessibility.exe 2011-01-04 13:20 . 2011-01-05 19:10 561152 ----a-w- c:\users\Default\AppData\Roaming\Microsoft\Windows\Start Menu\Programs\Accessories\Accessories.pif 2011-01-04 13:20 . 2011-01-05 19:09 561152 ----a-w- c:\users\Default\AppData\Roaming\Microsoft\Windows\Start Menu\Programs\Programs.pif 2011-01-04 13:20 . 2011-01-05 19:26 561152 ----a-w- c:\users\Default\AppData\Roaming\Microsoft\Windows\Start Menu\Start Menu.exe 2011-01-04 13:20 . 2011-01-05 19:25 561152 ----a-w- c:\users\Default\AppData\Roaming\Microsoft\Windows\SendTo\SendTo.scr 2011-01-04 13:19 . 2011-01-05 19:24 561152 ----a-w- c:\users\Default\AppData\Roaming\Microsoft\Windows\Recent\Recent.pif 2011-01-04 13:19 . 2011-01-05 19:07 561152 ----a-w- c:\users\Default\AppData\Roaming\Microsoft\Windows\Printer Shortcuts\Shortcuts.exe 2011-01-04 13:19 . 2011-01-05 19:07 561152 ----a-w- c:\users\Default\AppData\Roaming\Microsoft\Windows\Network Shortcuts\Shortcuts.exe 2011-01-04 13:19 . 2011-01-05 19:14 561152 ----a-w- c:\users\Default\AppData\Roaming\Microsoft\Windows\Cookies\Cookies.pif 2011-01-04 13:19 . 2011-01-05 19:05 561152 ----a-w- c:\users\Default\AppData\Roaming\Microsoft\Windows\Windows.pif 2011-01-04 13:18 . 2011-01-05 19:05 561152 ----a-w- c:\users\Default\AppData\Roaming\Microsoft\Internet Explorer\Quick Launch\Launch.scr 2011-01-04 13:18 . 2011-01-05 19:04 561152 ----a-w- c:\users\Default\AppData\Roaming\Microsoft\Internet Explorer\Explorer.exe 2011-01-03 15:43 . 2011-01-03 15:43 561152 ----a-w- c:\users\teo\AppData\Roaming\Microsoft\Windows\Recent\CustomDestinations\CustomDestinations.exe 2011-01-03 15:43 . 2011-01-03 15:43 561152 ----a-w- c:\users\teo\AppData\Roaming\Microsoft\Windows\Recent\AutomaticDestinations\AutomaticDestinations.exe 2010-12-29 17:03 . 2010-12-29 17:03 -------- d-----w- c:\programdata\Electronic Arts 2010-12-29 16:27 . 2010-12-29 16:27 -------- d-----w- c:\program files (x86)\Electronic Arts 2010-12-27 13:59 . 2010-12-27 14:05 88 --sh--r- c:\programdata\840BB621E5.sys 2010-12-27 13:59 . 2010-12-30 10:53 2828 --sha-w- c:\programdata\KGyGaAvL.sys 2010-12-27 13:58 . 2010-12-27 13:58 143360 ----a-w- c:\program files (x86)\Internet Explorer\Plugins\npqtplugin7.dll 2010-12-27 13:58 . 2010-12-27 13:58 143360 ----a-w- c:\program files (x86)\Internet Explorer\Plugins\npqtplugin6.dll 2010-12-27 13:58 . 2010-12-27 13:58 143360 ----a-w- c:\program files (x86)\Internet Explorer\Plugins\npqtplugin5.dll 2010-12-27 13:58 . 2010-12-27 13:58 143360 ----a-w- c:\program files (x86)\Internet Explorer\Plugins\npqtplugin4.dll 2010-12-27 13:58 . 2010-12-27 13:58 143360 ----a-w- c:\program files (x86)\Internet Explorer\Plugins\npqtplugin3.dll 2010-12-27 13:58 . 2010-12-27 13:58 143360 ----a-w- c:\program files (x86)\Internet Explorer\Plugins\npqtplugin2.dll 2010-12-27 13:58 . 2010-12-27 13:58 143360 ----a-w- c:\program files (x86)\Internet Explorer\Plugins\npqtplugin.dll 2010-12-27 13:58 . 2010-12-27 13:58 -------- d-----w- c:\program files (x86)\Common Files\Apple 2010-12-27 13:58 . 2010-12-27 13:58 -------- d-----w- c:\program files (x86)\QuickTime 2010-12-27 13:58 . 2010-12-27 13:58 -------- d-----w- c:\programdata\Apple Computer 2010-12-27 13:57 . 2010-12-27 13:57 -------- d-----w- c:\program files (x86)\Common Files\Protexis 2010-12-27 13:57 . 2010-12-27 13:57 -------- d-----w- c:\programdata\Corel 2010-12-27 13:54 . 2011-01-07 15:25 -------- d-----w- c:\users\teo\AppData\Local\Corel 2010-12-27 13:54 . 2011-01-07 15:25 -------- d-----w- c:\users\teo\AppData\Roaming\Corel 2010-12-27 13:51 . 2010-12-29 15:42 -------- d-----w- c:\programdata\Ulead Systems 2010-12-27 13:51 . 2010-12-27 13:53 -------- d-----w- c:\program files (x86)\Common Files\Corel 2010-12-27 13:51 . 2010-12-27 13:51 -------- d-----w- c:\program files (x86)\Corel 2010-12-26 09:24 . 2007-05-16 14:45 4496232 ----a-w- c:\windows\system32\d3dx9_34.dll 2010-12-22 19:02 . 2010-12-22 19:02 -------- d-----r- c:\program files (x86)\Skype 2010-12-22 16:37 . 2009-11-25 10:47 99176 ----a-w- c:\windows\SysWow64\PresentationHostProxy.dll 2010-12-22 16:37 . 2009-11-25 10:47 49472 ----a-w- c:\windows\SysWow64\netfxperf.dll 2010-12-22 16:37 . 2009-11-25 10:47 48960 ----a-w- c:\windows\system32\netfxperf.dll 2010-12-22 16:37 . 2009-11-25 10:47 297808 ----a-w- c:\windows\SysWow64\mscoree.dll 2010-12-22 16:37 . 2009-11-25 10:47 295264 ----a-w- c:\windows\SysWow64\PresentationHost.exe 2010-12-22 16:37 . 2009-11-25 10:47 1130824 ----a-w- c:\windows\SysWow64\dfshim.dll 2010-12-22 16:37 . 2009-11-25 10:47 109912 ----a-w- c:\windows\system32\PresentationHostProxy.dll 2010-12-22 16:37 . 2009-11-25 10:47 444752 ----a-w- c:\windows\system32\mscoree.dll 2010-12-22 16:37 . 2009-11-25 10:47 320352 ----a-w- c:\windows\system32\PresentationHost.exe 2010-12-22 16:37 . 2009-11-25 10:47 1942856 ----a-w- c:\windows\system32\dfshim.dll 2010-12-22 16:30 . 2010-11-16 10:01 8199504 ----a-w- c:\programdata\Microsoft\Windows Defender\Definition Updates\{DFF6C16D-3128-4DCE-A8E8-92D449D6DCFA}\mpengine.dll 2010-12-22 16:24 . 2010-03-24 07:34 1737120 ----a-w- c:\windows\system32\ntdll.dll 2010-12-22 16:23 . 2010-10-16 05:23 112000 ----a-w- c:\windows\system32\consent.exe 2010-12-22 16:20 . 2010-08-21 06:38 1024512 ----a-w- c:\windows\system32\wmpmde.dll 2010-12-22 16:20 . 2010-08-21 05:36 738816 ----a-w- c:\windows\SysWow64\wmpmde.dll 2010-12-22 16:19 . 2010-05-05 07:37 483840 ----a-w- c:\windows\system32\StructuredQuery.dll 2010-12-22 16:19 . 2010-05-05 06:46 363520 ----a-w- c:\windows\SysWow64\StructuredQuery.dll 2010-12-22 16:18 . 2010-08-20 05:38 559104 ----a-w- c:\windows\system32\spoolsv.exe 2010-12-22 16:18 . 2010-08-31 04:32 954752 ----a-w- c:\windows\SysWow64\mfc40.dll 2010-12-22 16:18 . 2010-08-31 04:32 954288 ----a-w- c:\windows\SysWow64\mfc40u.dll 2010-12-22 16:18 . 2010-08-27 06:14 236032 ----a-w- c:\windows\system32\srvsvc.dll 2010-12-22 16:18 . 2010-08-27 05:46 9728 ----a-w- c:\windows\SysWow64\sscore.dll 2010-12-22 16:18 . 2010-08-27 03:38 463360 ----a-w- c:\windows\system32\drivers\srv.sys 2010-12-22 16:18 . 2010-08-27 03:37 402944 ----a-w- c:\windows\system32\drivers\srv2.sys 2010-12-22 16:18 . 2010-08-27 03:37 161792 ----a-w- c:\windows\system32\drivers\srvnet.sys 2010-12-22 16:05 . 2010-02-23 08:16 294912 ----a-w- c:\windows\system32\browserchoice.exe 2010-12-22 16:05 . 2010-03-04 04:40 184832 ----a-w- c:\windows\system32\drivers\usbvideo.sys 2010-12-22 16:05 . 2010-03-04 04:32 243712 ----a-w- c:\windows\system32\drivers\ks.sys 2010-12-22 15:27 . 2010-01-09 07:19 139264 ----a-w- c:\windows\system32\cabview.dll 2010-12-22 15:27 . 2010-01-09 06:52 132608 ----a-w- c:\windows\SysWow64\cabview.dll 2010-12-22 15:27 . 2009-12-29 08:03 220672 ----a-w- c:\windows\system32\wintrust.dll 2010-12-22 15:27 . 2009-12-29 06:55 172032 ----a-w- c:\windows\SysWow64\wintrust.dll 2010-12-21 08:27 . 2011-01-04 08:09 -------- d-----w- c:\users\teo\AppData\Roaming\Zeon 2010-12-18 15:47 . 2010-12-18 15:47 -------- d-----w- c:\program files (x86)\Imikimi . (((((((((((((((((((((((((((((((((((((((( Find3M Report )))))))))))))))))))))))))))))))))))))))))))))))))))) . 2010-12-02 03:35 . 2010-12-02 03:35 4280320 ----a-w- c:\windows\SysWow64\GPhotos.scr 2010-11-04 21:52 . 2010-11-04 21:52 614400 ----a-w- c:\windows\AutoKMS.exe 2010-10-19 08:41 . 2010-09-08 07:41 270720 ------w- c:\windows\system32\MpSigStub.exe 2010-10-18 18:11 . 2010-10-18 18:11 31744 ----a-w- c:\windows\SysWow64\maplec.dll 2010-10-18 18:11 . 2010-10-18 18:11 212992 ----a-w- c:\windows\SysWow64\WMIMPLEX.dll 2010-10-18 18:11 . 2010-10-18 18:11 20480 ----a-w- c:\windows\SysWow64\maplecompat.dll . ((((((((((((((((((((((((((((((((((((( Reg Loading Points )))))))))))))))))))))))))))))))))))))))))))))))))) . . *Note* empty entries & legit default entries are not shown REGEDIT4 [HKEY_CURRENT_USER\Software\Microsoft\Internet Explorer\URLSearchHooks] "{bf7380fa-e3b4-4db2-af3e-9d8783a45bfc}"= "c:\program files (x86)\uTorrentBar\tbuTo1.dll" [2010-12-26 3911776] [HKEY_CLASSES_ROOT\clsid\{bf7380fa-e3b4-4db2-af3e-9d8783a45bfc}] [HKEY_LOCAL_MACHINE\Wow6432Node\~\Browser Helper Objects\{30F9B915-B755-4826-820B-08FBA6BD249D}] 2010-12-26 15:10 3911776 ----a-w- c:\program files (x86)\ConduitEngine\ConduitEngin0.dll [HKEY_LOCAL_MACHINE\Wow6432Node\~\Browser Helper Objects\{bf7380fa-e3b4-4db2-af3e-9d8783a45bfc}] 2010-12-26 15:10 3911776 ----a-w- c:\program files (x86)\uTorrentBar\tbuTo1.dll [HKEY_LOCAL_MACHINE\SOFTWARE\Wow6432Node\Microsoft\Internet Explorer\Toolbar] "{bf7380fa-e3b4-4db2-af3e-9d8783a45bfc}"= "c:\program files (x86)\uTorrentBar\tbuTo1.dll" [2010-12-26 3911776] "{30F9B915-B755-4826-820B-08FBA6BD249D}"= "c:\program files (x86)\ConduitEngine\ConduitEngin0.dll" [2010-12-26 3911776] [HKEY_CLASSES_ROOT\clsid\{bf7380fa-e3b4-4db2-af3e-9d8783a45bfc}] [HKEY_CLASSES_ROOT\clsid\{30f9b915-b755-4826-820b-08fba6bd249d}] [HKEY_CURRENT_USER\SOFTWARE\Microsoft\Windows\CurrentVersion\Run] "Skype"="c:\program files (x86)\Skype\Phone\Skype.exe" [2010-09-02 13351304] "NokiaPCInternetAccess"="c:\program files (x86)\Nokia\PC Internet Access\NPCIA.exe" [2009-05-26 651264] "uTorrent"="c:\program files (x86)\uTorrent\uTorrent.exe" [2010-12-11 395640] "PC Suite Tray"="c:\program files (x86)\Nokia\Nokia PC Suite 7\PCSuite.exe" [2010-05-14 1479680] "Corel Photo Downloader"="c:\program files (x86)\Common Files\Corel\Corel PhotoDownloader\Corel Photo Downloader.exe" [2010-07-28 526992] c:\programdata\Microsoft\Windows\Start Menu\Programs\Startup\ Bluetooth Monitor.lnk - c:\program files (x86)\TOSHIBA\Bluetooth Monitor\BtMon2.exe [2010-9-8 92280] [HKEY_LOCAL_MACHINE\software\microsoft\windows\currentversion\policies\system] "ConsentPromptBehaviorAdmin"= 0 (0x0) "ConsentPromptBehaviorUser"= 3 (0x3) "EnableLUA"= 0 (0x0) "EnableUIADesktopToggle"= 0 (0x0) "PromptOnSecureDesktop"= 0 (0x0) [HKEY_LOCAL_MACHINE\software\wow6432node\microsoft\windows nt\currentversion\drivers32] "aux1"=wdmaud.drv [HKEY_LOCAL_MACHINE\system\currentcontrolset\control\session manager] BootExecute REG_MULTI_SZ \0 R3 netw5v64;Intel® Wireless WiFi Link 5000 Series Adapter Driver for Windows Vista 64 Bit;c:\windows\system32\DRIVERS\netw5v64.sys [2009-06-10 5434368] R3 nmwcdcx64;Nokia USB Generic;c:\windows\system32\drivers\ccdcmbox64.sys [2010-02-26 25088] R3 nmwcdnsucx64;Nokia USB Flashing Generic;c:\windows\system32\drivers\nmwcdnsucx64.sys [2010-02-26 12288] R3 nmwcdnsux64;Nokia USB Flashing Phone Parent;c:\windows\system32\drivers\nmwcdnsux64.sys [2010-02-26 173056] R3 nmwcdx64;Nokia USB Phone Parent;c:\windows\system32\drivers\ccdcmbx64.sys [2010-02-26 19456] R3 SwitchBoard;SwitchBoard;c:\program files (x86)\Common Files\Adobe\SwitchBoard\SwitchBoard.exe [2010-02-19 517096] S0 sptd;sptd;c:\windows\System32\Drivers\sptd.sys [2010-09-08 834544] S2 AMD External Events Utility;AMD External Events Utility;c:\windows\system32\atiesrxx.exe [2009-08-18 203264] S2 TeamViewer4;TeamViewer 4;c:\program files (x86)\TeamViewer\Version4\TeamViewer_Service.exe [2009-10-07 185640] S3 SrvHsfHDA;SrvHsfHDA;c:\windows\system32\DRIVERS\VSTAZL6.SYS [2009-06-10 292864] S3 SrvHsfV92;SrvHsfV92;c:\windows\system32\DRIVERS\VSTDPV6.SYS [2009-06-10 1485312] S3 SrvHsfWinac;SrvHsfWinac;c:\windows\system32\DRIVERS\VSTCNXT6.SYS [2009-06-10 740864] S3 yukonw7;NDIS6.2 Miniport Driver for Marvell Yukon Ethernet Controller;c:\windows\system32\DRIVERS\yk62x64.sys [2009-06-10 389120] . Contents of the 'Scheduled Tasks' folder 2011-01-14 c:\windows\Tasks\GoogleUpdateTaskUserS-1-5-21-3447158227-3012016689-1084579962-1000Core.job - c:\users\teo\AppData\Local\Google\Update\GoogleUpdate.exe [2010-09-08 07:39] 2011-01-14 c:\windows\Tasks\GoogleUpdateTaskUserS-1-5-21-3447158227-3012016689-1084579962-1000UA.job - c:\users\teo\AppData\Local\Google\Update\GoogleUpdate.exe [2010-09-08 07:39] . --------- x86-64 ----------- [HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\Run] "EvtMgr6"="c:\program files\Logitech\SetPointP\SetPoint.exe" [2010-06-26 1609296] [HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows NT\CurrentVersion\Windows] "LoadAppInit_DLLs"=0x0 . ------- Supplementary Scan ------- . uLocal Page = c:\windows\system32\blank.htm uStart Page = about:blank mLocal Page = c:\windows\SysWOW64\blank.htm IE: Add to Google Photos Screensa&ver - c:\windows\system32\GPhotos.scr/200 IE: Download &Flash Movies - c:\program files (x86)\Flash2X\Flash Hunter\save.htm IE: E&xport to Microsoft Excel - c:\progra~2\MICROS~1\Office12\EXCEL.EXE/3000 TCP: {6B34DE5E-E3F1-4A75-A206-2E5E3B6E4440} = 10.10.10.3 DPF: {210D0CBC-8B17-48D1-B294-1A338DD2EB3A} - hxxp://webcam.varna.bg:8080/VatDec.cab . - - - - ORPHANS REMOVED - - - - WebBrowser-{D4027C7F-154A-4066-A1AD-4243D8127440} - (no file) WebBrowser-{BF7380FA-E3B4-4DB2-AF3E-9D8783A45BFC} - (no file) AddRemove-Adobe Shockwave Player - c:\windows\system32\Adobe\Shockwave 11\uninstaller.exe AddRemove-WinSetupFromUSB - c:\winsetupfromusb\Uninstall.exe . --------------------- LOCKED REGISTRY KEYS --------------------- [HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\CLSID\{A483C63A-CDBC-426E-BF93-872502E8144E}] @Denied: (A 2) (Everyone) @="FlashBroker" "LocalizedString"="@c:\\Windows\\SysWOW64\\Macromed\\Flash\\FlashUtil10k_ActiveX.exe,-101" [HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\CLSID\{A483C63A-CDBC-426E-BF93-872502E8144E}\Elevation] "Enabled"=dword:00000001 [HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\CLSID\{A483C63A-CDBC-426E-BF93-872502E8144E}\LocalServer32] @="c:\\Windows\\SysWOW64\\Macromed\\Flash\\FlashUtil10k_ActiveX.exe" [HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\CLSID\{A483C63A-CDBC-426E-BF93-872502E8144E}\TypeLib] @="{FAB3E735-69C7-453B-A446-B6823C6DF1C9}" [HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\CLSID\{D27CDB6E-AE6D-11cf-96B8-444553540000}] @Denied: (A 2) (Everyone) @="Shockwave Flash Object" [HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\CLSID\{D27CDB6E-AE6D-11cf-96B8-444553540000}\InprocServer32] @="c:\\Windows\\SysWOW64\\Macromed\\Flash\\Flash10k.ocx" "ThreadingModel"="Apartment" [HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\CLSID\{D27CDB6E-AE6D-11cf-96B8-444553540000}\MiscStatus] @="0" [HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\CLSID\{D27CDB6E-AE6D-11cf-96B8-444553540000}\ProgID] @="ShockwaveFlash.ShockwaveFlash.10" [HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\CLSID\{D27CDB6E-AE6D-11cf-96B8-444553540000}\ToolboxBitmap32] @="c:\\Windows\\SysWOW64\\Macromed\\Flash\\Flash10k.ocx, 1" [HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\CLSID\{D27CDB6E-AE6D-11cf-96B8-444553540000}\TypeLib] @="{D27CDB6B-AE6D-11cf-96B8-444553540000}" [HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\CLSID\{D27CDB6E-AE6D-11cf-96B8-444553540000}\Version] @="1.0" [HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\CLSID\{D27CDB6E-AE6D-11cf-96B8-444553540000}\VersionIndependentProgID] @="ShockwaveFlash.ShockwaveFlash" [HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\CLSID\{D27CDB70-AE6D-11cf-96B8-444553540000}] @Denied: (A 2) (Everyone) @="Macromedia Flash Factory Object" [HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\CLSID\{D27CDB70-AE6D-11cf-96B8-444553540000}\InprocServer32] @="c:\\Windows\\SysWOW64\\Macromed\\Flash\\Flash10k.ocx" "ThreadingModel"="Apartment" [HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\CLSID\{D27CDB70-AE6D-11cf-96B8-444553540000}\ProgID] @="FlashFactory.FlashFactory.1" [HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\CLSID\{D27CDB70-AE6D-11cf-96B8-444553540000}\ToolboxBitmap32] @="c:\\Windows\\SysWOW64\\Macromed\\Flash\\Flash10k.ocx, 1" [HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\CLSID\{D27CDB70-AE6D-11cf-96B8-444553540000}\TypeLib] @="{D27CDB6B-AE6D-11cf-96B8-444553540000}" [HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\CLSID\{D27CDB70-AE6D-11cf-96B8-444553540000}\Version] @="1.0" [HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\CLSID\{D27CDB70-AE6D-11cf-96B8-444553540000}\VersionIndependentProgID] @="FlashFactory.FlashFactory" [HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\Interface\{1D4C8A81-B7AC-460A-8C23-98713C41D6B3}] @Denied: (A 2) (Everyone) @="IFlashBroker3" [HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\Interface\{1D4C8A81-B7AC-460A-8C23-98713C41D6B3}\ProxyStubClsid32] @="{00020424-0000-0000-C000-000000000046}" [HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\Interface\{1D4C8A81-B7AC-460A-8C23-98713C41D6B3}\TypeLib] @="{6EF568F4-D437-4466-AA63-A3645136D93E}" "Version"="1.0" [HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\Interface\{2E4BB6BE-A75F-4DC0-9500-68203655A2C4}] @Denied: (A 2) (Everyone) @="IFlashBroker" [HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\Interface\{2E4BB6BE-A75F-4DC0-9500-68203655A2C4}\ProxyStubClsid32] @="{00020424-0000-0000-C000-000000000046}" [HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\Interface\{2E4BB6BE-A75F-4DC0-9500-68203655A2C4}\TypeLib] @="{6EF568F4-D437-4466-AA63-A3645136D93E}" "Version"="1.0" [HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\Interface\{DDF4CE26-4BDA-42BC-B0F0-0E75243AD285}] @Denied: (A 2) (Everyone) @="IFlashBroker2" [HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\Interface\{DDF4CE26-4BDA-42BC-B0F0-0E75243AD285}\ProxyStubClsid32] @="{00020424-0000-0000-C000-000000000046}" [HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\Interface\{DDF4CE26-4BDA-42BC-B0F0-0E75243AD285}\TypeLib] @="{6EF568F4-D437-4466-AA63-A3645136D93E}" "Version"="1.0" [HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\Interface\{E3F2C3CB-5EB8-4A04-B22C-7E3B4B6AF30F}] @Denied: (A 2) (Everyone) @="IFlashBroker4" [HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\Interface\{E3F2C3CB-5EB8-4A04-B22C-7E3B4B6AF30F}\ProxyStubClsid32] @="{00020424-0000-0000-C000-000000000046}" [HKEY_LOCAL_MACHINE\SOFTWARE\Classes\Wow6432Node\Interface\{E3F2C3CB-5EB8-4A04-B22C-7E3B4B6AF30F}\TypeLib] @="{FAB3E735-69C7-453B-A446-B6823C6DF1C9}" "Version"="1.0" [HKEY_LOCAL_MACHINE\SYSTEM\ControlSet001\Control\Class\{4D36E96D-E325-11CE-BFC1-08002BE10318}\0000\AllUserSettings] @Denied: (A) (Users) @Denied: (A) (Everyone) @Allowed: (B 1 2 3 4 5) (S-1-5-20) "BlindDial"=dword:00000000 [HKEY_LOCAL_MACHINE\SYSTEM\ControlSet001\Control\Class\{4D36E96D-E325-11CE-BFC1-08002BE10318}\0001\AllUserSettings] @Denied: (A) (Users) @Denied: (A) (Everyone) @Allowed: (B 1 2 3 4 5) (S-1-5-20) "BlindDial"=dword:00000000 [HKEY_LOCAL_MACHINE\SYSTEM\ControlSet001\Control\Class\{4D36E96D-E325-11CE-BFC1-08002BE10318}\0002\AllUserSettings] @Denied: (A) (Users) @Denied: (A) (Everyone) @Allowed: (B 1 2 3 4 5) (S-1-5-20) "BlindDial"=dword:00000000 [HKEY_LOCAL_MACHINE\SYSTEM\ControlSet001\Control\Class\{4D36E96D-E325-11CE-BFC1-08002BE10318}\0003\AllUserSettings] @Denied: (A) (Users) @Denied: (A) (Everyone) @Allowed: (B 1 2 3 4 5) (S-1-5-20) "BlindDial"=dword:00000000 [HKEY_LOCAL_MACHINE\SYSTEM\ControlSet001\Control\Class\{4D36E96D-E325-11CE-BFC1-08002BE10318}\0004\AllUserSettings] @Denied: (A) (Users) @Denied: (A) (Everyone) @Allowed: (B 1 2 3 4 5) (S-1-5-20) "BlindDial"=dword:00000000 [HKEY_LOCAL_MACHINE\SYSTEM\ControlSet001\Control\PCW\Security] @Denied: (Full) (Everyone) . Completion time: 2011-01-14 18:53:05 ComboFix-quarantined-files.txt 2011-01-14 16:53 Pre-Run: 13 583 769 600 bytes free Post-Run: 13 165 256 704 bytes free - - End Of File - - E1CE13282C9229FA51844AC83802E282
-
Ами за сега не са се появявали нови, и не знам ако ги изтрия пак дали няма да се появят .... Пратих този файл за анализ и ми изписа това Avast 4.8.1351.0 2011.01.14 Win32:Chydo F-Prot 4.6.2.117 2011.01.13 W32/Chydo.A и така нататък, има ли начин да ги изчистя... незнам какво да ги правя вече
-
Ами като начало го махнах от Scheduler Tasks, а и деинсталирах тоолбара Тези файлове продължават да си стоят
-
4 VT Community user(s) with a total of 4 reputation credit(s) say(s) this sample is goodware. 1 VT Community user(s) with a total of 1 reputation credit(s) say(s) this sample is malware. File name: AutoKMS.exe Submission date: 2011-01-13 22:20:46 (UTC) Current status: finished Result: 22 /43 (51.2%)
-
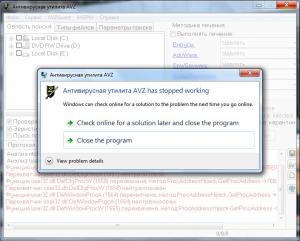
Да правя всичко точно и след няколко секунди работа и се появява NOT RESPONDING ето това става
-
AVZ
-
При изпълняване на 1-я скрипт от около 10 опита, всичките пъти програмата забива и се появява съобщение за затваряне на програмата....
-
ето и тези virusinfo_syscheck.zip virusinfo_syscure.zip
-
ето тези log.txt info.txt
-
All processes killed ========== OTL ========== Registry value HKEY_USERS\S-1-5-21-3447158227-3012016689-1084579962-1000\Software\Microsoft\Windows\CurrentVersion\Run\\AdobeBridge deleted successfully. Registry value HKEY_USERS\S-1-5-19\Software\Microsoft\Windows\CurrentVersion\RunOnce\\mctadmin deleted successfully. Registry value HKEY_USERS\S-1-5-20\Software\Microsoft\Windows\CurrentVersion\RunOnce\\mctadmin deleted successfully. HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\URL\Prefixes\\gopher|:gopher:// /E : value set successfully! HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\URL\Prefixes\\gopher|:gopher:// /E : value set successfully! Registry value HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows NT\CurrentVersion\Winlogon\\VMApplet:/pagefile deleted successfully. Registry value HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\ShellServiceObjectDelayLoad\\WebCheck deleted successfully. Registry key HKEY_LOCAL_MACHINE\SOFTWARE\Classes\CLSID\{E6FB5E20-DE35-11CF-9C87-00AA005127ED}\ not found. Registry key HKEY_CURRENT_USER\SOFTWARE\Microsoft\Windows\CurrentVersion\Explorer\MountPoints2\{2c087a07-bb21-11df-835a-00037aabad3a}\ deleted successfully. Registry key HKEY_LOCAL_MACHINE\SOFTWARE\Classes\CLSID\{2c087a07-bb21-11df-835a-00037aabad3a}\ not found. Registry key HKEY_CURRENT_USER\SOFTWARE\Microsoft\Windows\CurrentVersion\Explorer\MountPoints2\{2c087a07-bb21-11df-835a-00037aabad3a}\ not found. Registry key HKEY_LOCAL_MACHINE\SOFTWARE\Classes\CLSID\{2c087a07-bb21-11df-835a-00037aabad3a}\ not found. File F:\Autorun.exe not found. Registry key HKEY_CURRENT_USER\SOFTWARE\Microsoft\Windows\CurrentVersion\Explorer\MountPoints2\{4325a475-d368-11df-aacc-001e685d64c2}\ deleted successfully. Registry key HKEY_LOCAL_MACHINE\SOFTWARE\Classes\CLSID\{4325a475-d368-11df-aacc-001e685d64c2}\ not found. Registry key HKEY_CURRENT_USER\SOFTWARE\Microsoft\Windows\CurrentVersion\Explorer\MountPoints2\{4325a475-d368-11df-aacc-001e685d64c2}\ not found. Registry key HKEY_LOCAL_MACHINE\SOFTWARE\Classes\CLSID\{4325a475-d368-11df-aacc-001e685d64c2}\ not found. File H:\NokiaPCIA_Autorun.exe not found. Registry value HKEY_LOCAL_MACHINE\SYSTEM\CurrentControlSet\Control\Session manager\\BootExecute:autocheck autochk * deleted successfully. Registry value HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows NT\CurrentVersion\Drivers32\\vidc.xvid deleted successfully. ========== FILES ========== recycler not found in C:\ recycler not found in E:\ < ipconfig /flushdns /c > Windows IP Configuration Successfully flushed the DNS Resolver Cache. C:\Users\teo\Desktop\cmd.bat deleted successfully. C:\Users\teo\Desktop\cmd.txt deleted successfully. ========== COMMANDS ========== C:\Windows\System32\drivers\etc\Hosts moved successfully. HOSTS file reset successfully [EMPTYTEMP] User: All Users User: Default ->Temp folder emptied: 561152 bytes ->Temporary Internet Files folder emptied: 561152 bytes ->Flash cache emptied: 1686326 bytes User: Default User ->Temp folder emptied: 0 bytes ->Temporary Internet Files folder emptied: 0 bytes ->Flash cache emptied: 0 bytes User: Public User: teo ->Temp folder emptied: 76828676 bytes ->Temporary Internet Files folder emptied: 33579817 bytes ->Java cache emptied: 38794304 bytes ->Google Chrome cache emptied: 240294550 bytes ->Flash cache emptied: 235924569 bytes %systemdrive% .tmp files removed: 0 bytes %systemroot% .tmp files removed: 0 bytes %systemroot%\System32 .tmp files removed: 1619120 bytes %systemroot%\System32 (64bit) .tmp files removed: 0 bytes %systemroot%\System32\drivers .tmp files removed: 0 bytes Windows Temp folder emptied: 3760642 bytes %systemroot%\sysnative\config\systemprofile\AppData\Local\Microsoft\Windows\Temporary Internet Files folder emptied: 67630 bytes RecycleBin emptied: 0 bytes Total Files Cleaned = 604,00 mb [EMPTYFLASH] User: All Users User: Default ->Flash cache emptied: 0 bytes User: Default User ->Flash cache emptied: 0 bytes User: Public User: teo ->Flash cache emptied: 0 bytes Total Flash Files Cleaned = 0,00 mb OTL by OldTimer - Version 3.2.20.2 log created on 01142011_151929 Files\Folders moved on Reboot... C:\Users\teo\AppData\Local\Temp\FXSAPIDebugLogFile.txt moved successfully. Registry entries deleted on Reboot...
-
това са логовете от OTL от TDS Extras.Txt OTL.Txt TDSSKiller.2.4.13.0_14.01.2011_14.42.19_log.txt


Разглеждащи това в момента 0
- Няма регистрирани потребители разглеждащи тази страница.