


petionikolov
Потребител
-
Регистрация
-
Последно онлайн
-
За първи път виждам такова желание за помощ. ... Нямам думи! Благодаря за всичко!
-
Според мен всичко е наред с този файл Ето линка http://4storing.com/kz1ddq/0ca7e9a7ba0d150da419bd06264c0bcd.html Остава раздела за хардуера...

-
DDS (Ver_09-07-30.01) - NTFSx86 Run by User at 23:42:55,59 on 30.07.2009 г. Internet Explorer: 6.0.2900.2180 Microsoft Windows XP Professional 5.1.2600.2.1251.359.1033.18.2038.1271 [GMT 3:00] AV: ESET Smart Security 3.0 *On-access scanning enabled* (Updated) {E5E70D32-0101-4F12-8FB0-D96ACA4F34C0} FW: ESET Personal firewall *enabled* {E5E70D32-0101-4340-86A3-A7B0F1C8FFE0} ============== Running Processes =============== C:\WINDOWS\system32\svchost -k DcomLaunch svchost.exe C:\WINDOWS\System32\svchost.exe -k netsvcs svchost.exe svchost.exe C:\WINDOWS\system32\spoolsv.exe C:\WINDOWS\System32\acs.exe svchost.exe C:\Program Files\ESET\ESET Smart Security\ekrn.exe C:\BonArtMC\database\bin\mysqld-nt.exe C:\WINDOWS\System32\svchost.exe -k imgsvc C:\WINDOWS\System32\TUProgSt.exe C:\WINDOWS\Explorer.EXE C:\Program Files\Synaptics\SynTP\SynTPEnh.exe C:\Program Files\Atheros\ACU.exe C:\BonArtMC\BonArt.exe C:\Program Files\ESET\ESET Smart Security\egui.exe C:\WINDOWS\System32\igfxpers.exe C:\WINDOWS\System32\igfxsrvc.exe C:\WINDOWS\System32\igfxtray.exe C:\WINDOWS\RTHDCPL.EXE C:\Program Files\Google\GoogleToolbarNotifier\GoogleToolbarNotifier.exe C:\WINDOWS\system32\CTFMON.EXE C:\WINDOWS\Datecs\FType2K.exe C:\BonArtMC\abyssws_webserver.exe C:\BonArtMC\abyssws_webserver.exe C:\Program Files\Internet Explorer\iexplore.exe C:\Documents and Settings\User\Desktop\dds.pif ============== Pseudo HJT Report =============== uStart Page = about:blank uSearch Page = hxxp://www.google.com uSearch Bar = hxxp://www.google.com/ie mStart Page = about:blank uInternet Connection Wizard,ShellNext = iexplore uSearchURL,(Default) = hxxp://www.google.com/search?q=%s BHO: Adobe PDF Link Helper: {18df081c-e8ad-4283-a596-fa578c2ebdc3} - c:\program files\common files\adobe\acrobat\activex\AcroIEHelperShim.dll BHO: Google Toolbar Helper: {aa58ed58-01dd-4d91-8333-cf10577473f7} - c:\program files\google\google toolbar\GoogleToolbar.dll BHO: Google Toolbar Notifier BHO: {af69de43-7d58-4638-b6fa-ce66b5ad205d} - c:\program files\google\googletoolbarnotifier\5.1.1309.15642\swg.dll BHO: Google Dictionary Compression sdch: {c84d72fe-e17d-4195-bb24-76c02e2e7c4e} - c:\program files\google\google toolbar\component\fastsearch_A8904FB862BD9564.dll BHO: FlashGet GetFlash Class: {f156768e-81ef-470c-9057-481ba8380dba} - c:\program files\flashget\getflash.dll TB: Google Toolbar: {2318c2b1-4965-11d4-9b18-009027a5cd4f} - c:\program files\google\google toolbar\GoogleToolbar.dll TB: {2C688203-7EB3-4327-9995-1CB417BA23F9} - No File EB: {32683183-48a0-441b-a342-7c2a440a9478} - No File uRun: [swg] c:\program files\google\googletoolbarnotifier\GoogleToolbarNotifier.exe uRun: [ctfmon.exe] c:\windows\system32\ctfmon.exe mRun: [synTPEnh] c:\program files\synaptics\syntp\SynTPEnh.exe mRun: [ACU] "c:\program files\atheros\ACU.exe" -nogui mRun: [bAE3FA] c:\bonartmc\BonArt.exe mRun: [egui] "c:\program files\eset\eset smart security\egui.exe" /hide /waitservice mRun: [Persistence] c:\windows\system32\igfxpers.exe mRun: [igfxTray] c:\windows\system32\igfxtray.exe mRun: [HotKeysCmds] c:\windows\system32\hkcmd.exe mRun: [RTHDCPL] RTHDCPL.EXE StartupFolder: c:\docume~1\user\startm~1\programs\startup\abyssws.lnk - c:\bonartmc\abyssws.exe StartupFolder: c:\docume~1\alluse~1\startm~1\programs\startup\flexty~1.lnk - c:\windows\datecs\FType2K.exe IE: &Download All with FlashGet - c:\program files\flashget\jc_all.htm IE: &Download with FlashGet - c:\program files\flashget\jc_link.htm IE: {85d1f590-48f4-11d9-9669-0800200c9a66} - %windir%\bdoscandel.exe DPF: DirectAnimation Java Classes - file://c:\windows\java\classes\dajava.cab DPF: Microsoft XML Parser for Java - file://c:\windows\java\classes\xmldso.cab DPF: {166B1BCA-3F9C-11CF-8075-444553540000} - hxxp://download.macromedia.com/pub/shockwave/cabs/director/sw.cab DPF: {5D86DDB5-BDF9-441B-9E9E-D4730F4EE499} - hxxp://download.bitdefender.com/resources/scanner/sources/en/scan8/oscan8.cab DPF: {8FFBE65D-2C9C-4669-84BD-5829DC0B603C} - hxxp://fpdownload.macromedia.com/get/flashplayer/current/polarbear/ultrashim.cab Filter: x-sdch - {B1759355-3EEC-4C1E-B0F1-B719FE26E377} - c:\program files\google\google toolbar\component\fastsearch_A8904FB862BD9564.dll Handler: skype4com - {FFC8B962-9B40-4DFF-9458-1830C7DD7F5D} - c:\progra~1\common~1\skype\SKYPE4~1.DLL Notify: !SASWinLogon - c:\program files\superantispyware\SASWINLO.dll Notify: igfxcui - igfxdev.dll SEH: SABShellExecuteHook Class: {5ae067d3-9afb-48e0-853a-ebb7f4a000da} - c:\program files\superantispyware\SASSEH.DLL ================= FIREFOX =================== FF - ProfilePath - c:\docume~1\user\applic~1\mozilla\firefox\profiles\p1i9jalj.default\ FF - prefs.js: browser.search.selectedEngine - Google FF - prefs.js: browser.startup.homepage - 127.0.0.1 FF - component: c:\program files\mozilla firefox\components\qfaservices.dll ---- FIREFOX POLICIES ---- c:\program files\mozilla firefox\greprefs\all.js - pref("backups.number_of_prefs_copies", 1); c:\program files\mozilla firefox\greprefs\all.js - pref("capability.policy.default.Window.closed", "allAccess"); c:\program files\mozilla firefox\greprefs\all.js - pref("capability.policy.default.Window.document", "allAccess"); c:\program files\mozilla firefox\greprefs\all.js - pref("capability.policy.default.Window.frames", "allAccess"); c:\program files\mozilla firefox\greprefs\all.js - pref("capability.policy.default.Window.history", "allAccess"); c:\program files\mozilla firefox\greprefs\all.js - pref("capability.policy.default.Window.length", "allAccess"); c:\program files\mozilla firefox\greprefs\all.js - pref("capability.policy.default.Window.opener", "allAccess"); c:\program files\mozilla firefox\greprefs\all.js - pref("capability.policy.default.Window.parent", "allAccess"); c:\program files\mozilla firefox\greprefs\all.js - pref("capability.policy.default.Window.self", "allAccess"); c:\program files\mozilla firefox\greprefs\all.js - pref("capability.policy.default.Window.top", "allAccess"); c:\program files\mozilla firefox\greprefs\all.js - pref("capability.policy.default.Window.window", "allAccess"); c:\program files\mozilla firefox\greprefs\all.js - pref("capability.policy.mailnews.DOMParser,parseFromString", "noAccess"); c:\program files\mozilla firefox\greprefs\all.js - pref("capability.policy.mailnews.DOMParser,parseFromStream", "noAccess"); c:\program files\mozilla firefox\greprefs\all.js - pref("browser.block.target_new_window", false); c:\program files\mozilla firefox\greprefs\all.js - pref("dom.disable_window_open_feature.status", false); c:\program files\mozilla firefox\greprefs\all.js - pref("advanced.always_load_images", true); c:\program files\mozilla firefox\greprefs\all.js - pref("network.protocol-handler.external.help", false); c:\program files\mozilla firefox\greprefs\all.js - pref("network.protocol-handler.external-default", 2); c:\program files\mozilla firefox\greprefs\all.js - pref("network.http.connect.timeout", 30); // in seconds c:\program files\mozilla firefox\greprefs\all.js - pref("network.http.request.timeout", 120); // in seconds c:\program files\mozilla firefox\greprefs\all.js - pref("network.image.imageBehavior", 0); // 0-Accept, 1-dontAcceptForeign, 2-dontUse c:\program files\mozilla firefox\greprefs\all.js - pref("network.cookie.cookieBehavior", 3); // 0-Accept, 1-dontAcceptForeign, 2-dontUse, 3-p3p c:\program files\mozilla firefox\greprefs\all.js - pref("network.cookie.p3plevel", 1); // 0=low, 1=medium, 2=high, 3=custom c:\program files\mozilla firefox\greprefs\all.js - pref("network.enablePad", false); // Allow client to do proxy autodiscovery c:\program files\mozilla firefox\greprefs\security-prefs.js - pref("security.warn_entering_weak", false); c:\program files\mozilla firefox\greprefs\security-prefs.js - pref("security.warn_viewing_mixed", false); c:\program files\mozilla firefox\defaults\pref\firefox.js - pref("app.id", "{ec8030f7-c20a-464f-9b0e-13a3a9e97384}"); c:\program files\mozilla firefox\defaults\pref\firefox.js - pref("app.version", c:\program files\mozilla firefox\defaults\pref\firefox.js - pref("app.extensions.version", "0.10"); c:\program files\mozilla firefox\defaults\pref\firefox.js - pref("app.build_id", c:\program files\mozilla firefox\defaults\pref\firefox.js - pref("app.update.autoUpdateEnabled", false); // Whether or not background app updates c:\program files\mozilla firefox\defaults\pref\firefox.js - pref("app.update.url", "chrome://mozapps/locale/update/update.properties"); c:\program files\mozilla firefox\defaults\pref\firefox.js - pref("app.update.updatesAvailable", false); c:\program files\mozilla firefox\defaults\pref\firefox.js - pref("app.update.lastUpdateDate", 0); // UTC offset when last App update was c:\program files\mozilla firefox\defaults\pref\firefox.js - pref("app.update.performed", false); // Whether or not an update has been c:\program files\mozilla firefox\defaults\pref\firefox.js - pref("extensions.update.autoUpdateEnabled", false); c:\program files\mozilla firefox\defaults\pref\firefox.js - pref("extensions.update.autoUpdate", false); // Automatically download and install c:\program files\mozilla firefox\defaults\pref\firefox.js - pref("extensions.update.interval", 604800000); // Check for updates to Extensions and c:\program files\mozilla firefox\defaults\pref\firefox.js - pref("extensions.update.lastUpdateDate", 0); // UTC offset when last Extension/Theme c:\program files\mozilla firefox\defaults\pref\firefox.js - pref("extensions.update.severity.threshold", 5);// The number of pending Extension/Theme c:\program files\mozilla firefox\defaults\pref\firefox.js - pref("extensions.update.count", 0); // The number of extension/theme/etc c:\program files\mozilla firefox\defaults\pref\firefox.js - pref("update.interval", 3600000); // Check each of the above intervals c:\program files\mozilla firefox\defaults\pref\firefox.js - pref("update.showSlidingNotification", true); // Windows-only slide-up taskbar c:\program files\mozilla firefox\defaults\pref\firefox.js - pref("update.severity", 0); c:\program files\mozilla firefox\defaults\pref\firefox.js - pref("general.useragent.vendor", "Firefox"); c:\program files\mozilla firefox\defaults\pref\firefox.js - pref("general.useragent.vendorSub", "0.10"); c:\program files\mozilla firefox\defaults\pref\firefox.js - pref("browser.startup.homepage", "http://127.0.0.1/"); c:\program files\mozilla firefox\defaults\pref\firefox.js - pref("browser.startup.homepage_override.1", false); c:\program files\mozilla firefox\defaults\pref\firefox.js - pref("browser.turbo.enabled", false); c:\program files\mozilla firefox\defaults\pref\firefox.js - pref("browser.search.param.Google.1.name", "chrome://browser/content/searchconfig.properties"); c:\program files\mozilla firefox\defaults\pref\firefox.js - pref("browser.search.param.Google.1.custom", "chrome://browser/content/searchconfig.properties"); c:\program files\mozilla firefox\defaults\pref\firefox.js - pref("browser.search.param.Google.1.default", "chrome://browser/content/searchconfig.properties"); c:\program files\mozilla firefox\defaults\pref\firefox.js - pref("dom.disable_open_during_load", false); c:\program files\mozilla firefox\defaults\pref\firefox.js - pref("network.protocols.useSystemDefaults", false); // set to true if user links should use system default handlers c:\program files\mozilla firefox\defaults\pref\firefox.js - pref("update_notifications.enabled", true); c:\program files\mozilla firefox\defaults\pref\firefox.js - pref("update_notifications.provider.0.frequency", 7); // number of days c:\program files\mozilla firefox\defaults\pref\firefox.js - pref("browser.xul.error_pages.enabled", false); c:\program files\mozilla firefox\defaults\pref\firefox.js - pref("network.protocol-handler.external.news" , true); // for news c:\program files\mozilla firefox\defaults\pref\firefox.js - pref("security.warn_entering_weak.show_once", false); c:\program files\mozilla firefox\defaults\pref\firefox.js - pref("security.warn_viewing_mixed.show_once", false); c:\program files\mozilla firefox\defaults\pref\firefox.js - pref("pfs.datasource.url", "chrome://mozapps/locale/plugins/plugins.properties"); ============= SERVICES / DRIVERS =============== R1 SASDIFSV;SASDIFSV;c:\program files\superantispyware\sasdifsv.sys [2009-7-28 9968] R1 SASKUTIL;SASKUTIL;c:\program files\superantispyware\SASKUTIL.SYS [2009-7-28 72944] R2 ekrn;Eset Service;c:\program files\eset\eset smart security\ekrn.exe [2007-12-21 468224] R2 TuneUp.ProgramStatisticsSvc;TuneUp Program Statistics Service;c:\windows\system32\TUProgSt.exe [2009-7-28 604488] R3 RTL8187B;Realtek RTL8187B Wireless 802.11b/g 54Mbps USB 2.0 Network Adapter;c:\windows\system32\drivers\RTL8187B.sys [2008-10-17 288000] R3 WSIMD;wsimd Service;c:\windows\system32\drivers\wsimd.sys [2008-10-17 57408] S3 Ambfilt;Ambfilt;c:\windows\system32\drivers\Ambfilt.sys [2009-7-30 1684736] S3 SASENUM;SASENUM;c:\program files\superantispyware\SASENUM.SYS [2009-7-28 7408] =============== Created Last 30 ================ 2009-07-30 22:52 29,000 a------- c:\windows\system32\uxtuneup.dll 2009-07-30 22:52 361,288 a------- c:\windows\system32\TuneUpDefragService.exe 2009-07-30 22:43 <DIR> --d----- c:\windows\system32\SoftwareDistribution 2009-07-30 17:15 290,816 a------- c:\windows\vncutil.exe 2009-07-30 17:15 104,992 a------- c:\windows\RtkAudioService.exe 2009-07-30 17:15 35,840 a------- c:\windows\system32\RtkCoInstXP.dll 2009-07-30 17:15 1,389,056 a------- c:\windows\system32\drivers\Monfilt.sys 2009-07-30 17:15 1,684,736 a------- c:\windows\system32\drivers\Ambfilt.sys 2009-07-30 17:11 224,016 a------- c:\windows\system32\Tabctl32.ocx 2009-07-30 17:11 110,602 a------- c:\windows\system32\xcdsfx32.bin 2009-07-30 17:11 <DIR> --d----- c:\program files\Driver Magician 2009-07-30 16:59 219,648 a------- c:\windows\PEV.exe 2009-07-30 16:59 161,792 a------- c:\windows\SWREG.exe 2009-07-30 16:59 98,816 a------- c:\windows\sed.exe 2009-07-30 11:01 <DIR> -cd----- c:\windows\system32\dllcache\cache 2009-07-30 10:40 <DIR> --d----- c:\docume~1\alluse~1\applic~1\SUPERAntiSpyware.com 2009-07-30 10:39 <DIR> --d----- c:\program files\SUPERAntiSpyware 2009-07-30 10:39 <DIR> --d----- c:\docume~1\user\applic~1\SUPERAntiSpyware.com 2009-07-30 10:39 <DIR> --d----- c:\program files\common files\Wise Installation Wizard 2009-07-30 10:32 <DIR> --d----- c:\documents and settings\user\DoctorWeb 2009-07-28 10:30 604,488 a------- c:\windows\system32\TUProgSt.exe 2009-07-28 10:24 <DIR> --d----- c:\docume~1\user\applic~1\TuneUp Software 2009-07-28 10:24 <DIR> --d----- c:\docume~1\alluse~1\applic~1\TuneUp Software 2009-07-28 10:24 <DIR> --d----- c:\program files\TuneUp Utilities 2009 2009-07-28 10:22 <DIR> --d----- c:\program files\Enigma Software Group 2009-07-28 10:19 <DIR> --d----- c:\docume~1\user\applic~1\ESET 2009-07-28 10:18 <DIR> --d----- c:\program files\ESET 2009-07-28 10:05 <DIR> --d----- c:\docume~1\user\applic~1\Malwarebytes 2009-07-28 10:05 38,160 a------- c:\windows\system32\drivers\mbamswissarmy.sys 2009-07-28 10:05 19,096 a------- c:\windows\system32\drivers\mbam.sys 2009-07-28 10:05 <DIR> --d----- c:\docume~1\alluse~1\applic~1\Malwarebytes 2009-07-28 10:05 <DIR> --d----- c:\program files\Malwarebytes' Anti-Malware ==================== Find3M ==================== ============= FINISH: 23:43:31,48 =============== UNLESS SPECIFICALLY INSTRUCTED, DO NOT POST THIS LOG. IF REQUESTED, ZIP IT UP & ATTACH IT DDS (Ver_09-07-30.01) Microsoft Windows XP Professional Boot Device: \Device\HarddiskVolume1 Install Date: 17.10.2008 г. 13:11:42 System Uptime: 30.7.2009 г. 23:02:22 (0 hours ago) Motherboard: Intel Corp. | | Base Board Product Name Processor: Intel® Pentium® Dual CPU T2370 @ 1.73GHz | CPU | 795/533mhz Processor: Intel® Pentium® Dual CPU T2370 @ 1.73GHz | CPU | 795/533mhz ==== Disk Partitions ========================= C: is FIXED (NTFS) - 98 GiB total, 83,955 GiB free. D: is FIXED (NTFS) - 135 GiB total, 25,206 GiB free. E: is CDROM () F: is CDROM () ==== Disabled Device Manager Items ============= Class GUID: {4D36E97E-E325-11CE-BFC1-08002BE10318} Description: Device ID: ACPI\TOS1901\2&DABA3FF&0 Manufacturer: Name: PNP Device ID: ACPI\TOS1901\2&DABA3FF&0 Service: Class GUID: {4D36E97E-E325-11CE-BFC1-08002BE10318} Description: SM Bus Controller Device ID: PCI\VEN_8086&DEV_283E&SUBSYS_FF641179&REV_03\3&B1BFB68&0&FB Manufacturer: Name: SM Bus Controller PNP Device ID: PCI\VEN_8086&DEV_283E&SUBSYS_FF641179&REV_03\3&B1BFB68&0&FB Service: ==== System Restore Points =================== RP1: 30.7.2009 г. 16:08:17 - System Checkpoint RP2: 30.7.2009 г. 17:08:10 - Installed Bulgarian (Phonetic) - Huku RP3: 30.7.2009 г. 17:15:47 - Installed Realtek High Definition Audio Driver RP4: 30.7.2009 г. 18:03:18 - Removed Sentinel Protection Installer 7.0.0 RP5: 30.7.2009 г. 22:49:03 - Software Distribution Service 3.0 ==== Installed Programs ====================== ABBYY FineReader 7.0 Professional Edition Acrobat.com Adobe AIR Adobe Bridge 1.0 Adobe Common File Installer Adobe Flash Player 10 ActiveX Adobe Help Center 1.0 Adobe Photoshop CS2 Adobe Reader 9 Adobe Shockwave Player Adobe Stock Photos 1.0 Atheros Client Utility BS.Player FREE Bulgarian (Phonetic) - Huku Camera Assistant Software for Toshiba Driver Magician 3.41 ESET Smart Security FlashGet 1.9.6.1073 FlexType 2K Google Earth Google Toolbar for Internet Explorer Google Updater High Definition Audio Driver Package - KB888111 HijackThis 2.0.2 Intel® Graphics Media Accelerator Driver Lexmark Software Uninstall Malwarebytes' Anti-Malware Microsoft Office Professional Edition 2003 Microsoft Visual C++ 2005 Redistributable MV2Player (remove only) Nero 6 Ultra Edition REALTEK GbE & FE Ethernet PCI-E NIC Driver Realtek High Definition Audio Driver REALTEK RTL8187B Wireless LAN Driver Realtek USB 2.0 Card Reader Skype™ 3.8 Soft Modem with SmartCP Spybot - Search & Destroy SpyHunter SUPERAntiSpyware Free Edition Synaptics Pointing Device Driver TuneUp Utilities 2009 Update for Windows XP (KB898461) WebFldrs XP WebTrance3.0 (aaeinoaee?aia) Winamp Windows Installer 3.1 (KB893803) Windows Media Format Runtime Windows XP Service Pack 2 WinRAR archiver ==== Event Viewer Messages From Past Week ======== 30.7.2009 і. 22:23:43, error: Service Control Manager [7009] - Timeout (30000 milliseconds) waiting for the PEVSystemStart service to connect. 30.7.2009 і. 22:23:42, error: Service Control Manager [7009] - Timeout (30000 milliseconds) waiting for the PEVSystemStart service to connect. 30.7.2009 і. 22:20:56, error: Service Control Manager [7009] - Timeout (30000 milliseconds) waiting for the PEVSystemStart service to connect. 30.7.2009 і. 17:03:04, error: Service Control Manager [7009] - Timeout (30000 milliseconds) waiting for the PEVSystemStart service to connect. 30.7.2009 і. 17:03:03, error: Service Control Manager [7009] - Timeout (30000 milliseconds) waiting for the PEVSystemStart service to connect. 30.7.2009 і. 16:59:56, error: Service Control Manager [7009] - Timeout (30000 milliseconds) waiting for the PEVSystemStart service to connect. 30.7.2009 і. 15:16:54, error: Dhcp [1002] - The IP address lease 192.168.0.102 for the Network Card with network address 001B9EE39A16 has been denied by the DHCP server 0.0.0.0 (The DHCP Server sent a DHCPNACK message). 30.7.2009 і. 10:59:48, error: Service Control Manager [7009] - Timeout (30000 milliseconds) waiting for the PEVSystemStart service to connect. 30.7.2009 і. 10:58:07, error: Service Control Manager [7009] - Timeout (30000 milliseconds) waiting for the PEVSystemStart service to connect. 30.7.2009 і. 10:45:39, error: Service Control Manager [7009] - Timeout (30000 milliseconds) waiting for the PEVSystemStart service to connect. 28.7.2009 і. 11:44:07, error: DCOM [10005] - DCOM got error "%1084" attempting to start the service EventSystem with arguments "" in order to run the server: {1BE1F766-5536-11D1-B726-00C04FB926AF} 28.7.2009 і. 11:39:46, error: DCOM [10005] - DCOM got error "%1084" attempting to start the service StiSvc with arguments "" in order to run the server: {A1F4E726-8CF1-11D1-BF92-0060081ED811} 28.7.2009 і. 11:39:28, error: DCOM [10005] - DCOM got error "%1084" attempting to start the service StiSvc with arguments "" in order to run the server: {A1F4E726-8CF1-11D1-BF92-0060081ED811} 28.7.2009 і. 11:39:28, error: DCOM [10005] - DCOM got error "%1084" attempting to start the service StiSvc with arguments "" in order to run the server: {A1F4E726-8CF1-11D1-BF92-0060081ED811} 28.7.2009 і. 11:35:46, error: Service Control Manager [7026] - The following boot-start or system-start driver(s) failed to load: AFD easdrv epfwtdi Fips intelppm IPSec MRxSmb NetBIOS NetBT RasAcd Rdbss Tcpip 28.7.2009 і. 11:35:46, error: Service Control Manager [7001] - The TCP/IP NetBIOS Helper service depends on the AFD Networking Support Environment service which failed to start because of the following error: A device attached to the system is not functioning. 28.7.2009 і. 11:35:46, error: Service Control Manager [7001] - The IPSEC Services service depends on the IPSEC driver service which failed to start because of the following error: A device attached to the system is not functioning. 28.7.2009 і. 11:35:46, error: Service Control Manager [7001] - The DNS Client service depends on the TCP/IP Protocol Driver service which failed to start because of the following error: A device attached to the system is not functioning. 28.7.2009 і. 11:35:46, error: Service Control Manager [7001] - The DHCP Client service depends on the NetBios over Tcpip service which failed to start because of the following error: A device attached to the system is not functioning. 28.7.2009 і. 11:35:02, error: DCOM [10005] - DCOM got error "%1084" attempting to start the service EventSystem with arguments "" in order to run the server: {1BE1F766-5536-11D1-B726-00C04FB926AF} 28.7.2009 і. 11:34:52, error: DCOM [10005] - DCOM got error "%1084" attempting to start the service netman with arguments "" in order to run the server: {BA126AE5-2166-11D1-B1D0-00805FC1270E} 28.7.2009 і. 10:30:30, error: Service Control Manager [7000] - The TuneUp Theme Extension service failed to start due to the following error: The executable program that this service is configured to run in does not implement the service. 28.7.2009 і. 10:24:50, error: Service Control Manager [7000] - The TuneUp Theme Extension service failed to start due to the following error: The executable program that this service is configured to run in does not implement the service. 24.7.2009 і. 12:41:45, error: Dhcp [1002] - The IP address lease 192.168.1.2 for the Network Card with network address 001E3338620C has been denied by the DHCP server 192.168.1.1 (The DHCP Server sent a DHCPNACK message). 24.7.2009 і. 08:18:58, error: Dhcp [1002] - The IP address lease 192.168.1.2 for the Network Card with network address 001E3338620C has been denied by the DHCP server 192.168.1.1 (The DHCP Server sent a DHCPNACK message). ==== End Of File =========================== Мирише ми на формат ц: колкото и да не ми се иска. Благодаря ти за всичко. Задължен съм ти!
-
За трети път го почистих, но този път е абсолютно чист, а проблемът си остава. Ето лога Malwarebytes' Anti-Malware 1.39 Версия на базата от данни: 2531 Windows 5.1.2600 Service Pack 2 30.7.2009 г. 23:31:53 mbam-log-2009-07-30 (23-31-53).txt Тип сканиране: Пълно сканиране (C:\|D:\|) Сканирани обекти: 148438 Изминало време: 26 minute(s), 46 second(s) Заразени процеси в паметта: 0 Заразени модули в паметта: 0 Заразени ключове в регистратурата: 0 Заразени стойности в регистратурата: 0 Заразени информационни обекти в регистратурата: 0 Заразени папки: 0 Заразени файлове: 0 Заразени процеси в паметта: (Не бяха открити заплахи) Заразени модули в паметта: (Не бяха открити заплахи) Заразени ключове в регистратурата: (Не бяха открити заплахи) Заразени стойности в регистратурата: (Не бяха открити заплахи) Заразени информационни обекти в регистратурата: (Не бяха открити заплахи) Заразени папки: (Не бяха открити заплахи) Заразени файлове: (Не бяха открити заплахи)
-
Заповядай ROOTREPEAL © AD, 2007-2009 ================================================== Scan Start Time: 2009/07/30 22:41 Program Version: Version 1.3.3.0 Windows Version: Windows XP SP2 ================================================== Drivers ------------------- Name: 00000053 Image Path: \Driver\00000053 Address: 0x00000000 Size: 0 File Visible: No Signed: - Status: - Name: catchme.sys Image Path: C:\DOCUME~1\User\LOCALS~1\Temp\catchme.sys Address: 0xBA420000 Size: 31744 File Visible: No Signed: - Status: - Name: dump_atapi.sys Image Path: C:\WINDOWS\System32\Drivers\dump_atapi.sys Address: 0xA7CD3000 Size: 98304 File Visible: No Signed: - Status: - Name: dump_WMILIB.SYS Image Path: C:\WINDOWS\System32\Drivers\dump_WMILIB.SYS Address: 0xBA606000 Size: 8192 File Visible: No Signed: - Status: - Name: PROCEXP90.SYS Image Path: C:\WINDOWS\system32\Drivers\PROCEXP90.SYS Address: 0xBA65A000 Size: 6464 File Visible: No Signed: - Status: - Name: rootrepeal.sys Image Path: C:\WINDOWS\system32\drivers\rootrepeal.sys Address: 0xA70E5000 Size: 49152 File Visible: No Signed: - Status: - SSDT ------------------- #: 041 Function Name: NtCreateKey Status: Hooked by "sptd.sys" at address 0xb9ed9ac8 #: 071 Function Name: NtEnumerateKey Status: Hooked by "sptd.sys" at address 0xb9ed9c22 #: 073 Function Name: NtEnumerateValueKey Status: Hooked by "sptd.sys" at address 0xb9ed9f9a #: 119 Function Name: NtOpenKey Status: Hooked by "sptd.sys" at address 0xb9ed998e #: 160 Function Name: NtQueryKey Status: Hooked by "sptd.sys" at address 0xb9eda064 #: 177 Function Name: NtQueryValueKey Status: Hooked by "sptd.sys" at address 0xb9ed9efc #: 247 Function Name: NtSetValueKey Status: Hooked by "sptd.sys" at address 0xb9eda0ec ==EOF==
-
готово ComboFix 09-07-29.04 - User 07.2009 г. 22:21.3.2 - NTFSx86 Microsoft Windows XP Professional 5.1.2600.2.1251.359.1033.18.2038.1464 [GMT 3:00] Running from: c:\documents and settings\User\Desktop\ComboFix.exe Command switches used :: c:\documents and settings\User\Desktop\CFScript.txt AV: ESET Smart Security 3.0 *On-access scanning disabled* (Updated) {E5E70D32-0101-4F12-8FB0-D96ACA4F34C0} FW: ESET Personal firewall *enabled* {E5E70D32-0101-4340-86A3-A7B0F1C8FFE0} WARNING -THIS MACHINE DOES NOT HAVE THE RECOVERY CONSOLE INSTALLED !! . ((((((((((((((((((((((((( Files Created from 2009-06-28 to 2009-07-30 ))))))))))))))))))))))))))))))) . 2009-07-30 15:02 . 2008-06-12 10:09 33088 ----a-w- c:\documents and settings\User\Application Data\Macromedia\Flash Player\www.macromedia.com\bin\airappinstaller\airappinstaller.exe 2009-07-30 14:15 . 2008-10-23 14:42 290816 ----a-w- c:\windows\vncutil.exe 2009-07-30 14:15 . 2009-02-09 11:34 35840 ----a-w- c:\windows\system32\RtkCoInstXP.dll 2009-07-30 14:15 . 2008-06-24 11:46 104992 ----a-w- c:\windows\RtkAudioService.exe 2009-07-30 14:15 . 2006-01-04 12:41 1389056 ----a-w- c:\windows\system32\drivers\Monfilt.sys 2009-07-30 14:15 . 2008-08-05 17:10 1684736 ----a-w- c:\windows\system32\drivers\Ambfilt.sys 2009-07-30 14:11 . 2004-08-11 12:55 110602 ----a-w- c:\windows\system32\xcdsfx32.bin 2009-07-30 14:11 . 2009-07-30 14:15 -------- d-----w- c:\program files\Driver Magician 2009-07-30 08:12 . 2009-07-30 08:30 -------- d-----w- c:\windows\BDOSCAN8 2009-07-30 07:43 . 2009-07-30 13:52 117760 ----a-w- c:\documents and settings\User\Application Data\SUPERAntiSpyware.com\SUPERAntiSpyware\SDDLLS\UIREPAIR.DLL 2009-07-30 07:40 . 2009-07-30 07:40 -------- d-----w- c:\documents and settings\All Users\Application Data\SUPERAntiSpyware.com 2009-07-30 07:39 . 2009-07-30 07:39 -------- d-----w- c:\program files\SUPERAntiSpyware 2009-07-30 07:39 . 2009-07-30 07:39 -------- d-----w- c:\documents and settings\User\Application Data\SUPERAntiSpyware.com 2009-07-30 07:39 . 2009-07-30 07:39 -------- d-----w- c:\program files\Common Files\Wise Installation Wizard 2009-07-30 07:32 . 2009-07-30 07:32 -------- d-----w- c:\documents and settings\User\DoctorWeb 2009-07-28 07:57 . 2009-07-28 07:57 -------- d-----w- c:\program files\Common Files\Adobe AIR 2009-07-28 07:43 . 2009-07-28 07:43 -------- d-----w- c:\documents and settings\User\Local Settings\Application Data\ESET 2009-07-28 07:30 . 2009-07-28 07:30 604416 ----a-w- c:\windows\system32\TUProgSt.exe 2009-07-28 07:30 . 2009-04-27 12:21 28928 ----a-w- c:\windows\system32\uxtuneup.dll 2009-07-28 07:30 . 2009-07-28 07:30 361216 ----a-w- c:\windows\system32\TuneUpDefragService.exe 2009-07-28 07:24 . 2009-07-28 07:24 -------- d-----w- c:\documents and settings\User\Application Data\TuneUp Software 2009-07-28 07:24 . 2009-07-28 07:24 -------- d-----w- c:\documents and settings\All Users\Application Data\TuneUp Software 2009-07-28 07:24 . 2009-07-28 07:30 -------- d-----w- c:\program files\TuneUp Utilities 2009 2009-07-28 07:22 . 2009-07-28 07:22 -------- d-----w- c:\program files\Enigma Software Group 2009-07-28 07:19 . 2009-07-28 07:19 -------- d-----w- c:\documents and settings\User\Application Data\ESET 2009-07-28 07:18 . 2009-07-28 07:18 -------- d-----w- c:\program files\ESET 2009-07-28 07:18 . 2009-07-28 07:18 -------- d-----w- c:\documents and settings\All Users\Application Data\ESET 2009-07-28 07:05 . 2009-07-28 07:05 -------- d-----w- c:\documents and settings\User\Application Data\Malwarebytes 2009-07-28 07:05 . 2009-07-13 10:36 38160 ----a-w- c:\windows\system32\drivers\mbamswissarmy.sys 2009-07-28 07:05 . 2009-07-28 07:05 -------- d-----w- c:\documents and settings\All Users\Application Data\Malwarebytes 2009-07-28 07:05 . 2009-07-13 10:36 19096 ----a-w- c:\windows\system32\drivers\mbam.sys 2009-07-28 07:05 . 2009-07-28 07:05 -------- d-----w- c:\program files\Malwarebytes' Anti-Malware . (((((((((((((((((((((((((((((((((((((((( Find3M Report )))))))))))))))))))))))))))))))))))))))))))))))))))) . 2009-07-30 15:51 . 2008-11-29 11:25 -------- d-----w- c:\program files\Spybot - Search & Destroy 2009-07-30 15:04 . 2008-11-29 11:25 -------- d-----w- c:\documents and settings\All Users\Application Data\Spybot - Search & Destroy 2009-07-30 07:40 . 2008-10-17 15:54 -------- d-----w- c:\program files\FlashGet 2009-07-28 07:55 . 2008-10-17 18:36 -------- d-----w- c:\program files\Common Files\Adobe 2009-07-26 19:24 . 2008-10-17 15:49 -------- d-----w- c:\documents and settings\User\Application Data\Skype 2009-07-26 13:04 . 2008-10-17 19:54 -------- d-----w- c:\documents and settings\User\Application Data\skypePM 2004-09-13 20:57 . 2004-09-13 20:57 94208 ----a-w- c:\program files\mozilla firefox\components\BrandRes.dll 2004-09-13 20:57 . 2004-09-13 20:57 150912 ----a-w- c:\program files\mozilla firefox\components\fullsoft.dll 2004-09-13 20:57 . 2004-09-13 20:57 53346 ----a-w- c:\program files\mozilla firefox\components\jar50.dll 2004-09-13 20:57 . 2004-09-13 20:57 61532 ----a-w- c:\program files\mozilla firefox\components\jsd3250.dll 2004-09-13 20:57 . 2004-09-13 20:57 24682 ----a-w- c:\program files\mozilla firefox\components\qfaservices.dll 2004-09-13 20:57 . 2004-09-13 20:57 172132 ----a-w- c:\program files\mozilla firefox\components\xpinstal.dll . ((((((((((((((((((((((((((((( SnapShot@2009-07-30_14.03.10 ))))))))))))))))))))))))))))))))))))))))) . + 2009-07-30 14:15 . 2006-07-21 14:14 86016 c:\windows\system32\ReinstallBackups\0005\DriverFiles\SOUNDMAN.EXE + 2009-07-30 14:15 . 2004-08-03 21:56 23552 c:\windows\system32\ReinstallBackups\0005\DriverFiles\i386\wdmaud.drv + 2009-07-30 14:15 . 2004-08-03 21:08 48640 c:\windows\system32\ReinstallBackups\0005\DriverFiles\i386\stream.sys + 2009-07-30 14:15 . 2004-08-03 21:08 60288 c:\windows\system32\ReinstallBackups\0005\DriverFiles\i386\drmk.sys + 2009-07-30 14:15 . 2005-05-03 16:43 69632 c:\windows\system32\ReinstallBackups\0005\DriverFiles\ALCMTR.EXE + 2008-10-17 17:44 . 2002-04-22 21:17 45056 c:\windows\system32\newdll.dll - 2008-10-17 15:21 . 2004-08-03 21:08 48640 c:\windows\system32\drivers\stream.sys + 2008-10-17 15:21 . 2004-08-03 20:08 48640 c:\windows\system32\drivers\stream.sys + 2008-10-17 15:21 . 2004-08-03 20:08 60288 c:\windows\system32\drivers\drmk.sys - 2008-10-17 15:21 . 2004-08-03 21:08 60288 c:\windows\system32\drivers\drmk.sys + 2008-10-17 15:21 . 2004-08-03 20:08 48640 c:\windows\system32\dllcache\stream.sys - 2008-10-17 15:21 . 2004-08-03 21:08 48640 c:\windows\system32\dllcache\stream.sys + 2008-10-17 15:21 . 2004-08-03 20:08 60288 c:\windows\system32\dllcache\drmk.sys - 2008-10-17 15:21 . 2004-08-03 21:08 60288 c:\windows\system32\dllcache\drmk.sys + 2008-10-17 15:20 . 2008-08-19 10:26 77824 c:\windows\SOUNDMAN.EXE + 2009-07-30 14:41 . 2002-05-13 10:06 53248 c:\windows\Datecs\Remove.exe - 2008-10-17 17:44 . 2000-12-17 03:46 36864 c:\windows\Datecs\Protype\PROTYPE.DLL + 2008-10-17 17:44 . 2000-12-17 04:46 36864 c:\windows\Datecs\Protype\PROTYPE.DLL + 2008-10-17 17:44 . 2002-04-24 01:47 56320 c:\windows\Datecs\live\Live.exe + 2009-07-30 14:41 . 2002-05-19 06:24 95232 c:\windows\Datecs\FType2K.exe + 2009-07-30 14:41 . 2002-04-21 10:16 20480 c:\windows\Datecs\Flex_utl\Flex2Kutil.exe + 2008-10-17 15:20 . 2009-03-02 08:14 57344 c:\windows\ALCMTR.EXE + 2009-07-30 14:15 . 2004-08-03 21:56 4096 c:\windows\system32\ReinstallBackups\0005\DriverFiles\i386\ksuser.dll + 2008-10-17 17:44 . 1999-11-11 10:47 6416 c:\windows\system32\kbdinori.Dll - 2008-10-17 17:44 . 1999-11-11 15:47 6416 c:\windows\system32\kbdinori.Dll - 2008-10-17 17:44 . 1999-11-11 15:47 6416 c:\windows\system32\kbdinasa.Dll + 2008-10-17 17:44 . 1999-11-11 10:47 6416 c:\windows\system32\kbdinasa.Dll - 2008-10-17 17:44 . 1999-11-11 15:47 6928 c:\windows\system32\kbdhebx.Dll + 2008-10-17 17:44 . 1999-11-11 10:47 6928 c:\windows\system32\kbdhebx.Dll + 2008-10-17 17:44 . 1999-11-18 02:04 7440 c:\windows\system32\KBDDLL.DLL - 2008-10-17 17:44 . 1999-11-18 07:04 7440 c:\windows\system32\KBDDLL.DLL - 2008-10-17 17:44 . 2000-11-17 10:47 8992 c:\windows\system32\kbdbphz.dLL + 2008-10-17 17:44 . 2000-11-17 05:47 8992 c:\windows\system32\kbdbphz.dLL - 2008-10-17 17:44 . 1997-04-03 23:00 8992 c:\windows\system32\KBDBPH.dLL + 2008-10-17 17:44 . 1997-04-03 18:00 8992 c:\windows\system32\KBDBPH.dLL - 2008-10-17 17:44 . 1999-12-07 11:00 6416 c:\windows\system32\kbdbp.Dll + 2008-10-17 17:44 . 1999-12-07 06:00 6416 c:\windows\system32\kbdbp.Dll + 2008-10-17 17:44 . 2000-11-14 22:52 6416 c:\windows\system32\kbdbds.Dll - 2008-10-17 17:44 . 2000-11-15 03:52 6416 c:\windows\system32\kbdbds.Dll + 2007-10-11 15:59 . 2007-10-11 15:59 6144 c:\windows\system32\Huku.dll + 2008-10-17 15:21 . 2004-08-03 21:56 4096 c:\windows\system32\dllcache\ksuser.dll - 2008-10-17 17:44 . 2000-10-16 15:50 7202 c:\windows\Datecs\FDOS.COM + 2008-10-17 17:44 . 2000-10-16 11:50 7202 c:\windows\Datecs\Fdos.com + 2008-10-17 15:20 . 2009-02-06 16:11 131072 c:\windows\system32\RTCOM\RTLCPAPI.dll + 2008-10-17 15:20 . 2009-02-18 10:58 266240 c:\windows\system32\RTCOM\RTCOMDLL.dll + 2009-07-30 14:15 . 2007-12-21 16:01 139264 c:\windows\system32\ReinstallBackups\0005\DriverFiles\RTLCPAPI.dll + 2009-07-30 14:15 . 2007-11-19 15:12 262144 c:\windows\system32\ReinstallBackups\0005\DriverFiles\RTCOMDLL.dll + 2009-07-30 14:15 . 2004-08-03 21:15 145792 c:\windows\system32\ReinstallBackups\0005\DriverFiles\i386\portcls.sys + 2009-07-30 14:15 . 2004-08-03 21:15 140928 c:\windows\system32\ReinstallBackups\0005\DriverFiles\i386\ks.sys - 2008-10-17 13:02 . 2008-12-01 14:48 120544 c:\windows\system32\FNTCACHE.DAT + 2008-10-17 13:02 . 2009-07-30 14:54 120544 c:\windows\system32\FNTCACHE.DAT + 2004-03-16 07:58 . 2004-08-03 20:15 145792 c:\windows\system32\drivers\portcls.sys - 2004-03-16 07:58 . 2004-08-03 21:15 145792 c:\windows\system32\drivers\portcls.sys - 2008-10-17 15:21 . 2004-08-03 21:15 140928 c:\windows\system32\drivers\ks.sys + 2008-10-17 15:21 . 2004-08-03 20:15 140928 c:\windows\system32\drivers\ks.sys + 2004-03-16 07:58 . 2004-08-03 20:15 145792 c:\windows\system32\dllcache\portcls.sys - 2004-03-16 07:58 . 2004-08-03 21:15 145792 c:\windows\system32\dllcache\portcls.sys - 2008-10-17 15:21 . 2004-08-03 21:15 140928 c:\windows\system32\dllcache\ks.sys + 2008-10-17 15:21 . 2004-08-03 20:15 140928 c:\windows\system32\dllcache\ks.sys + 2008-10-17 15:20 . 2008-08-25 13:17 528384 c:\windows\RtlExUpd.dll + 2009-07-30 14:08 . 2009-07-30 14:08 114688 c:\windows\Installer\fce37.msi + 2009-07-30 14:41 . 2001-09-28 14:00 164864 c:\windows\Datecs\UNWISE.EXE + 2009-07-30 14:15 . 2007-11-20 16:15 1826816 c:\windows\system32\ReinstallBackups\0005\DriverFiles\SkyTel.exe + 2009-07-30 14:15 . 2007-11-07 15:31 1191936 c:\windows\system32\ReinstallBackups\0005\DriverFiles\RtlUpd.exe + 2009-07-30 14:15 . 2007-03-23 17:19 9715200 c:\windows\system32\ReinstallBackups\0005\DriverFiles\RTLCPL.EXE + 2009-07-30 14:15 . 2008-01-30 09:28 4725760 c:\windows\system32\ReinstallBackups\0005\DriverFiles\RtkHDAud.sys + 2009-07-30 14:15 . 2007-06-28 14:44 2165760 c:\windows\system32\ReinstallBackups\0005\DriverFiles\MicCal.exe + 2009-07-30 14:15 . 2006-05-04 14:26 2808832 c:\windows\system32\ReinstallBackups\0005\DriverFiles\ALCWZRD.EXE + 2008-10-17 15:20 . 2009-03-04 14:58 5045760 c:\windows\system32\drivers\RtkHDAud.sys - 2008-10-17 15:20 . 2007-11-20 16:15 1826816 c:\windows\SkyTel.exe + 2008-10-17 15:20 . 2007-11-20 15:15 1826816 c:\windows\SkyTel.exe + 2008-10-17 15:20 . 2009-01-21 12:54 1206816 c:\windows\RtlUpd.exe - 2008-10-17 15:20 . 2007-03-23 17:19 9715200 c:\windows\RTLCPL.exe + 2008-10-17 15:20 . 2008-06-19 13:27 9715200 c:\windows\RTLCPL.EXE + 2008-10-17 15:20 . 2008-09-30 13:38 2168320 c:\windows\MicCal.exe + 2008-10-17 15:20 . 2008-06-19 13:42 2808832 c:\windows\ALCWZRD.EXE - 2008-10-17 15:20 . 2006-05-04 14:26 2808832 c:\windows\alcwzrd.exe + 2009-07-30 14:15 . 2008-01-29 13:47 16859648 c:\windows\system32\ReinstallBackups\0005\DriverFiles\RTHDCPL.EXE + 2008-10-17 15:20 . 2009-03-02 13:01 17530368 c:\windows\RTHDCPL.EXE . -- Snapshot reset to current date -- . ((((((((((((((((((((((((((((((((((((( Reg Loading Points )))))))))))))))))))))))))))))))))))))))))))))))))) . . *Note* empty entries & legit default entries are not shown REGEDIT4 [HKEY_CURRENT_USER\SOFTWARE\Microsoft\Windows\CurrentVersion\Run] "swg"="c:\program files\Google\GoogleToolbarNotifier\GoogleToolbarNotifier.exe" [2008-10-17 39408] [HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\Run] "SynTPEnh"="c:\program files\Synaptics\SynTP\SynTPEnh.exe" [2007-12-06 1024000] "ACU"="c:\program files\Atheros\ACU.exe" [2008-01-26 450648] "BAE3FA"="c:\bonartmc\BonArt.exe" [2007-05-23 61440] "egui"="c:\program files\ESET\ESET Smart Security\egui.exe" [2008-07-01 1447168] c:\documents and settings\User\Start Menu\Programs\Startup\ abyssws.lnk - c:\bonartmc\abyssws.exe [2008-2-5 49636] c:\documents and settings\All Users\Start Menu\Programs\Startup\ FlexType 2K.lnk - c:\windows\Datecs\FType2K.exe [2009-7-30 95232] [hkey_local_machine\software\microsoft\windows\currentversion\explorer\ShellExecuteHooks] "{5AE067D3-9AFB-48E0-853A-EBB7F4A000DA}"= "c:\program files\SUPERAntiSpyware\SASSEH.DLL" [2008-05-13 77824] [HKEY_LOCAL_MACHINE\software\microsoft\windows nt\currentversion\winlogon\notify\!SASWinLogon] 2008-12-22 09:05 356352 ----a-w- c:\program files\SUPERAntiSpyware\SASWINLO.dll [HKEY_CURRENT_USER\software\microsoft\windows\currentversion\run-] "SUPERAntiSpyware"=c:\program files\SUPERAntiSpyware\SUPERAntiSpyware.exe "swg"=c:\program files\Google\GoogleToolbarNotifier\GoogleToolbarNotifier.exe "ctfmon.exe"=c:\windows\system32\CTFMON.EXE [HKEY_LOCAL_MACHINE\software\microsoft\windows\currentversion\run-] "Persistence"=c:\windows\System32\igfxpers.exe "IgfxTray"=c:\windows\System32\igfxtray.exe "HotKeysCmds"=c:\windows\System32\hkcmd.exe "SoundMan"=SOUNDMAN.EXE "RTHDCPL"=RTHDCPL.EXE "Alcmtr"=ALCMTR.EXE "SkyTel"=SkyTel.EXE "AlcWzrd"=ALCWZRD.EXE "Adobe Reader Speed Launcher"="c:\program files\Adobe\Reader 9.0\Reader\Reader_sl.exe" [HKLM\~\services\sharedaccess\parameters\firewallpolicy\standardprofile] "EnableFirewall"= 0 (0x0) [HKLM\~\services\sharedaccess\parameters\firewallpolicy\standardprofile\AuthorizedApplications\List] "%windir%\\system32\\sessmgr.exe"= "c:\\Program Files\\FlashGet\\flashget.exe"= "c:\\WINDOWS\\system32\\LMabcoms.exe"= "c:\\Program Files\\Skype\\Phone\\Skype.exe"= R1 SASDIFSV;SASDIFSV;c:\program files\SUPERAntiSpyware\sasdifsv.sys [28.7.2009 і. 10:53 9968] R1 SASKUTIL;SASKUTIL;c:\program files\SUPERAntiSpyware\SASKUTIL.SYS [28.7.2009 і. 10:53 72944] R2 ekrn;Eset Service;c:\program files\ESET\ESET Smart Security\ekrn.exe [21.12.2007 і. 08:21 468224] R2 TuneUp.ProgramStatisticsSvc;TuneUp Program Statistics Service;c:\windows\system32\TUProgSt.exe [28.7.2009 і. 10:30 604416] R3 RTL8187B;Realtek RTL8187B Wireless 802.11b/g 54Mbps USB 2.0 Network Adapter;c:\windows\system32\drivers\RTL8187B.sys [17.10.2008 і. 18:44 288000] R3 WSIMD;wsimd Service;c:\windows\system32\drivers\wsimd.sys [17.10.2008 і. 18:32 57408] S3 Ambfilt;Ambfilt;c:\windows\system32\drivers\Ambfilt.sys [30.7.2009 і. 17:15 1684736] S3 SASENUM;SASENUM;c:\program files\SUPERAntiSpyware\SASENUM.SYS [28.7.2009 і. 10:53 7408] HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows NT\CurrentVersion\Svchost - NetSvcs UxTuneUp . Contents of the 'Scheduled Tasks' folder 2009-07-30 c:\windows\Tasks\1-Click Maintenance.job - c:\program files\TuneUp Utilities 2009\OneClickStarter.exe [2009-04-27 13:37] . - - - - ORPHANS REMOVED - - - - HKLM-Run-UTNH Agent - c:\windows\system32\28463\UTNH.exe . ------- Supplementary Scan ------- . uStart Page = about:blank uSearch Page = hxxp://www.google.com uSearch Bar = hxxp://www.google.com/ie mStart Page = about:blank uSearchURL,(Default) = hxxp://www.google.com/search?q=%s IE: &Download All with FlashGet - c:\program files\FlashGet\jc_all.htm IE: &Download with FlashGet - c:\program files\FlashGet\jc_link.htm DPF: DirectAnimation Java Classes - file://c:\windows\Java\classes\dajava.cab DPF: Microsoft XML Parser for Java - file://c:\windows\Java\classes\xmldso.cab FF - ProfilePath - c:\documents and settings\User\Application Data\Mozilla\Firefox\Profiles\p1i9jalj.default\ FF - prefs.js: browser.search.selectedEngine - Google FF - prefs.js: browser.startup.homepage - 127.0.0.1 FF - component: c:\program files\Mozilla Firefox\components\qfaservices.dll ---- FIREFOX POLICIES ---- c:\program files\Mozilla Firefox\greprefs\all.js - pref("backups.number_of_prefs_copies", 1); c:\program files\Mozilla Firefox\greprefs\all.js - pref("capability.policy.default.Window.closed", "allAccess"); c:\program files\Mozilla Firefox\greprefs\all.js - pref("capability.policy.default.Window.document", "allAccess"); c:\program files\Mozilla Firefox\greprefs\all.js - pref("capability.policy.default.Window.frames", "allAccess"); c:\program files\Mozilla Firefox\greprefs\all.js - pref("capability.policy.default.Window.history", "allAccess"); c:\program files\Mozilla Firefox\greprefs\all.js - pref("capability.policy.default.Window.length", "allAccess"); c:\program files\Mozilla Firefox\greprefs\all.js - pref("capability.policy.default.Window.opener", "allAccess"); c:\program files\Mozilla Firefox\greprefs\all.js - pref("capability.policy.default.Window.parent", "allAccess"); c:\program files\Mozilla Firefox\greprefs\all.js - pref("capability.policy.default.Window.self", "allAccess"); c:\program files\Mozilla Firefox\greprefs\all.js - pref("capability.policy.default.Window.top", "allAccess"); c:\program files\Mozilla Firefox\greprefs\all.js - pref("capability.policy.default.Window.window", "allAccess"); c:\program files\Mozilla Firefox\greprefs\all.js - pref("capability.policy.mailnews.DOMParser,parseFromString", "noAccess"); c:\program files\Mozilla Firefox\greprefs\all.js - pref("capability.policy.mailnews.DOMParser,parseFromStream", "noAccess"); c:\program files\Mozilla Firefox\greprefs\all.js - pref("browser.block.target_new_window", false); c:\program files\Mozilla Firefox\greprefs\all.js - pref("dom.disable_window_open_feature.status", false); c:\program files\Mozilla Firefox\greprefs\all.js - pref("advanced.always_load_images", true); c:\program files\Mozilla Firefox\greprefs\all.js - pref("network.protocol-handler.external.help", false); c:\program files\Mozilla Firefox\greprefs\all.js - pref("network.protocol-handler.external-default", 2); c:\program files\Mozilla Firefox\greprefs\all.js - pref("network.http.connect.timeout", 30); // in seconds c:\program files\Mozilla Firefox\greprefs\all.js - pref("network.http.request.timeout", 120); // in seconds c:\program files\Mozilla Firefox\greprefs\all.js - pref("network.image.imageBehavior", 0); // 0-Accept, 1-dontAcceptForeign, 2-dontUse c:\program files\Mozilla Firefox\greprefs\all.js - pref("network.cookie.cookieBehavior", 3); // 0-Accept, 1-dontAcceptForeign, 2-dontUse, 3-p3p c:\program files\Mozilla Firefox\greprefs\all.js - pref("network.cookie.p3plevel", 1); // 0=low, 1=medium, 2=high, 3=custom c:\program files\Mozilla Firefox\greprefs\all.js - pref("network.enablePad", false); // Allow client to do proxy autodiscovery c:\program files\Mozilla Firefox\greprefs\security-prefs.js - pref("security.warn_entering_weak", false); c:\program files\Mozilla Firefox\greprefs\security-prefs.js - pref("security.warn_viewing_mixed", false); c:\program files\Mozilla Firefox\defaults\pref\firefox.js - pref("app.id", "{ec8030f7-c20a-464f-9b0e-13a3a9e97384}"); c:\program files\Mozilla Firefox\defaults\pref\firefox.js - pref("app.version", c:\program files\Mozilla Firefox\defaults\pref\firefox.js - pref("app.extensions.version", "0.10"); c:\program files\Mozilla Firefox\defaults\pref\firefox.js - pref("app.build_id", c:\program files\Mozilla Firefox\defaults\pref\firefox.js - pref("app.update.autoUpdateEnabled", false); // Whether or not background app updates c:\program files\Mozilla Firefox\defaults\pref\firefox.js - pref("app.update.url", "chrome://mozapps/locale/update/update.properties"); c:\program files\Mozilla Firefox\defaults\pref\firefox.js - pref("app.update.updatesAvailable", false); c:\program files\Mozilla Firefox\defaults\pref\firefox.js - pref("app.update.lastUpdateDate", 0); // UTC offset when last App update was c:\program files\Mozilla Firefox\defaults\pref\firefox.js - pref("app.update.performed", false); // Whether or not an update has been c:\program files\Mozilla Firefox\defaults\pref\firefox.js - pref("extensions.update.autoUpdateEnabled", false); c:\program files\Mozilla Firefox\defaults\pref\firefox.js - pref("extensions.update.autoUpdate", false); // Automatically download and install c:\program files\Mozilla Firefox\defaults\pref\firefox.js - pref("extensions.update.interval", 604800000); // Check for updates to Extensions and c:\program files\Mozilla Firefox\defaults\pref\firefox.js - pref("extensions.update.lastUpdateDate", 0); // UTC offset when last Extension/Theme c:\program files\Mozilla Firefox\defaults\pref\firefox.js - pref("extensions.update.severity.threshold", 5);// The number of pending Extension/Theme c:\program files\Mozilla Firefox\defaults\pref\firefox.js - pref("extensions.update.count", 0); // The number of extension/theme/etc c:\program files\Mozilla Firefox\defaults\pref\firefox.js - pref("update.interval", 3600000); // Check each of the above intervals c:\program files\Mozilla Firefox\defaults\pref\firefox.js - pref("update.showSlidingNotification", true); // Windows-only slide-up taskbar c:\program files\Mozilla Firefox\defaults\pref\firefox.js - pref("update.severity", 0); c:\program files\Mozilla Firefox\defaults\pref\firefox.js - pref("general.useragent.vendor", "Firefox"); c:\program files\Mozilla Firefox\defaults\pref\firefox.js - pref("general.useragent.vendorSub", "0.10"); c:\program files\Mozilla Firefox\defaults\pref\firefox.js - pref("browser.startup.homepage", "http://127.0.0.1/"); c:\program files\Mozilla Firefox\defaults\pref\firefox.js - pref("browser.startup.homepage_override.1", false); c:\program files\Mozilla Firefox\defaults\pref\firefox.js - pref("browser.turbo.enabled", false); c:\program files\Mozilla Firefox\defaults\pref\firefox.js - pref("browser.search.param.Google.1.name", "chrome://browser/content/searchconfig.properties"); c:\program files\Mozilla Firefox\defaults\pref\firefox.js - pref("browser.search.param.Google.1.custom", "chrome://browser/content/searchconfig.properties"); c:\program files\Mozilla Firefox\defaults\pref\firefox.js - pref("browser.search.param.Google.1.default", "chrome://browser/content/searchconfig.properties"); c:\program files\Mozilla Firefox\defaults\pref\firefox.js - pref("dom.disable_open_during_load", false); c:\program files\Mozilla Firefox\defaults\pref\firefox.js - pref("network.protocols.useSystemDefaults", false); // set to true if user links should use system default handlers c:\program files\Mozilla Firefox\defaults\pref\firefox.js - pref("update_notifications.enabled", true); c:\program files\Mozilla Firefox\defaults\pref\firefox.js - pref("update_notifications.provider.0.frequency", 7); // number of days c:\program files\Mozilla Firefox\defaults\pref\firefox.js - pref("browser.xul.error_pages.enabled", false); c:\program files\Mozilla Firefox\defaults\pref\firefox.js - pref("network.protocol-handler.external.news" , true); // for news c:\program files\Mozilla Firefox\defaults\pref\firefox.js - pref("security.warn_entering_weak.show_once", false); c:\program files\Mozilla Firefox\defaults\pref\firefox.js - pref("security.warn_viewing_mixed.show_once", false); c:\program files\Mozilla Firefox\defaults\pref\firefox.js - pref("pfs.datasource.url", "chrome://mozapps/locale/plugins/plugins.properties"); . ************************************************************************** catchme 0.3.1398 W2K/XP/Vista - rootkit/stealth malware detector by Gmer, http://www.gmer.net Rootkit scan 2009-07-30 22:23 Windows 5.1.2600 Service Pack 2 NTFS scanning hidden processes ... scanning hidden autostart entries ... scanning hidden files ... scan completed successfully hidden files: 0 ************************************************************************** [HKEY_LOCAL_MACHINE\System\ControlSet001\Services\MySql] "ImagePath"="C:/BonArtMC/database/bin/mysqld-nt.exe" [HKEY_LOCAL_MACHINE\System\ControlSet001\Services\MySql] "ImagePath"="C:/BonArtMC/database/bin/mysqld-nt.exe" . --------------------- DLLs Loaded Under Running Processes --------------------- - - - - - - - > 'winlogon.exe'(1460) c:\program files\SUPERAntiSpyware\SASWINLO.dll - - - - - - - > 'explorer.exe'(2000) c:\windows\system32\newdll.dll . Completion time: 2009-07-30 22:25 ComboFix-quarantined-files.txt 2009-07-30 19:25 ComboFix2.txt 2009-07-30 14:04 ComboFix3.txt 2009-07-30 08:02 Pre-Run: 90 560 495 616 bytes free Post-Run: 90 531 016 704 bytes free 306
-
Здравейте, ето логовете ComboFix 09-07-29.04 - User 07.2009 г. 17:00.2.2 - NTFSx86 Microsoft Windows XP Professional 5.1.2600.2.1251.359.1033.18.2038.1630 [GMT 3:00] Running from: c:\documents and settings\User\Desktop\ComboFix.exe AV: ESET Smart Security 3.0 *On-access scanning disabled* (Updated) {E5E70D32-0101-4F12-8FB0-D96ACA4F34C0} FW: ESET Personal firewall *enabled* {E5E70D32-0101-4340-86A3-A7B0F1C8FFE0} WARNING -THIS MACHINE DOES NOT HAVE THE RECOVERY CONSOLE INSTALLED !! . ((((((((((((((((((((((((( Files Created from 2009-06-28 to 2009-07-30 ))))))))))))))))))))))))))))))) . 2009-07-30 08:12 . 2009-07-30 08:30 -------- d-----w- c:\windows\BDOSCAN8 2009-07-30 07:43 . 2009-07-30 13:52 117760 ----a-w- c:\documents and settings\User\Application Data\SUPERAntiSpyware.com\SUPERAntiSpyware\SDDLLS\UIREPAIR.DLL 2009-07-30 07:40 . 2009-07-30 07:40 -------- d-----w- c:\documents and settings\All Users\Application Data\SUPERAntiSpyware.com 2009-07-30 07:39 . 2009-07-30 07:39 -------- d-----w- c:\program files\SUPERAntiSpyware 2009-07-30 07:39 . 2009-07-30 07:39 -------- d-----w- c:\documents and settings\User\Application Data\SUPERAntiSpyware.com 2009-07-30 07:39 . 2009-07-30 07:39 -------- d-----w- c:\program files\Common Files\Wise Installation Wizard 2009-07-30 07:32 . 2009-07-30 07:32 -------- d-----w- c:\documents and settings\User\DoctorWeb 2009-07-28 07:57 . 2009-07-28 07:57 -------- d-----w- c:\program files\Common Files\Adobe AIR 2009-07-28 07:43 . 2009-07-28 07:43 -------- d-----w- c:\documents and settings\User\Local Settings\Application Data\ESET 2009-07-28 07:30 . 2009-07-28 07:30 604416 ----a-w- c:\windows\system32\TUProgSt.exe 2009-07-28 07:30 . 2009-04-27 12:21 28928 ----a-w- c:\windows\system32\uxtuneup.dll 2009-07-28 07:30 . 2009-07-28 07:30 361216 ----a-w- c:\windows\system32\TuneUpDefragService.exe 2009-07-28 07:24 . 2009-07-28 07:24 -------- d-----w- c:\documents and settings\User\Application Data\TuneUp Software 2009-07-28 07:24 . 2009-07-28 07:24 -------- d-----w- c:\documents and settings\All Users\Application Data\TuneUp Software 2009-07-28 07:24 . 2009-07-28 07:30 -------- d-----w- c:\program files\TuneUp Utilities 2009 2009-07-28 07:22 . 2009-07-28 07:22 -------- d-----w- c:\program files\Enigma Software Group 2009-07-28 07:19 . 2009-07-28 07:19 -------- d-----w- c:\documents and settings\User\Application Data\ESET 2009-07-28 07:18 . 2009-07-28 07:18 -------- d-----w- c:\program files\ESET 2009-07-28 07:18 . 2009-07-28 07:18 -------- d-----w- c:\documents and settings\All Users\Application Data\ESET 2009-07-28 07:05 . 2009-07-28 07:05 -------- d-----w- c:\documents and settings\User\Application Data\Malwarebytes 2009-07-28 07:05 . 2009-07-13 10:36 38160 ----a-w- c:\windows\system32\drivers\mbamswissarmy.sys 2009-07-28 07:05 . 2009-07-28 07:05 -------- d-----w- c:\documents and settings\All Users\Application Data\Malwarebytes 2009-07-28 07:05 . 2009-07-13 10:36 19096 ----a-w- c:\windows\system32\drivers\mbam.sys 2009-07-28 07:05 . 2009-07-28 07:05 -------- d-----w- c:\program files\Malwarebytes' Anti-Malware . (((((((((((((((((((((((((((((((((((((((( Find3M Report )))))))))))))))))))))))))))))))))))))))))))))))))))) . 2009-07-30 08:48 . 2008-11-29 11:25 -------- d-----w- c:\documents and settings\All Users\Application Data\Spybot - Search & Destroy 2009-07-30 07:40 . 2008-10-17 15:54 -------- d-----w- c:\program files\FlashGet 2009-07-28 07:55 . 2008-10-17 18:36 -------- d-----w- c:\program files\Common Files\Adobe 2009-07-26 19:24 . 2008-10-17 15:49 -------- d-----w- c:\documents and settings\User\Application Data\Skype 2009-07-26 13:04 . 2008-10-17 19:54 -------- d-----w- c:\documents and settings\User\Application Data\skypePM 2004-09-13 20:57 . 2004-09-13 20:57 94208 ----a-w- c:\program files\mozilla firefox\components\BrandRes.dll 2004-09-13 20:57 . 2004-09-13 20:57 150912 ----a-w- c:\program files\mozilla firefox\components\fullsoft.dll 2004-09-13 20:57 . 2004-09-13 20:57 53346 ----a-w- c:\program files\mozilla firefox\components\jar50.dll 2004-09-13 20:57 . 2004-09-13 20:57 61532 ----a-w- c:\program files\mozilla firefox\components\jsd3250.dll 2004-09-13 20:57 . 2004-09-13 20:57 24682 ----a-w- c:\program files\mozilla firefox\components\qfaservices.dll 2004-09-13 20:57 . 2004-09-13 20:57 172132 ----a-w- c:\program files\mozilla firefox\components\xpinstal.dll . ((((((((((((((((((((((((((((((((((((( Reg Loading Points )))))))))))))))))))))))))))))))))))))))))))))))))) . . *Note* empty entries & legit default entries are not shown REGEDIT4 [HKEY_CURRENT_USER\SOFTWARE\Microsoft\Windows\CurrentVersion\Run] "swg"="c:\program files\Google\GoogleToolbarNotifier\GoogleToolbarNotifier.exe" [2008-10-17 39408] "ctfmon.exe"="c:\windows\system32\ctfmon.exe" [2004-08-03 15360] "SUPERAntiSpyware"="c:\program files\SUPERAntiSpyware\SUPERAntiSpyware.exe" [2009-07-28 1830128] [HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\Run] "IgfxTray"="c:\windows\System32\igfxtray.exe" [2008-02-05 141848] "HotKeysCmds"="c:\windows\System32\hkcmd.exe" [2008-02-05 162328] "Persistence"="c:\windows\System32\igfxpers.exe" [2008-02-05 137752] "SynTPEnh"="c:\program files\Synaptics\SynTP\SynTPEnh.exe" [2007-12-06 1024000] "ACU"="c:\program files\Atheros\ACU.exe" [2008-01-26 450648] "BAE3FA"="c:\bonartmc\BonArt.exe" [2007-05-23 61440] "egui"="c:\program files\ESET\ESET Smart Security\egui.exe" [2008-07-01 1447168] "Adobe Reader Speed Launcher"="c:\program files\Adobe\Reader 9.0\Reader\Reader_sl.exe" [2008-06-11 34672] "RTHDCPL"="RTHDCPL.EXE" - c:\windows\RTHDCPL.exe [2008-01-29 16859648] c:\documents and settings\User\Start Menu\Programs\Startup\ abyssws.lnk - c:\bonartmc\abyssws.exe [2008-2-5 49636] c:\documents and settings\All Users\Start Menu\Programs\Startup\ FlexType 2K.lnk - c:\windows\Datecs\Flex2K.exe [2008-10-17 151552] [hkey_local_machine\software\microsoft\windows\currentversion\explorer\ShellExecuteHooks] "{5AE067D3-9AFB-48E0-853A-EBB7F4A000DA}"= "c:\program files\SUPERAntiSpyware\SASSEH.DLL" [2008-05-13 77824] [HKEY_LOCAL_MACHINE\software\microsoft\windows nt\currentversion\winlogon\notify\!SASWinLogon] 2008-12-22 09:05 356352 ----a-w- c:\program files\SUPERAntiSpyware\SASWINLO.dll [HKLM\~\services\sharedaccess\parameters\firewallpolicy\standardprofile] "EnableFirewall"= 0 (0x0) [HKLM\~\services\sharedaccess\parameters\firewallpolicy\standardprofile\AuthorizedApplications\List] "%windir%\\system32\\sessmgr.exe"= "c:\\Program Files\\FlashGet\\flashget.exe"= "c:\\WINDOWS\\system32\\LMabcoms.exe"= "c:\\Program Files\\Skype\\Phone\\Skype.exe"= R1 SASDIFSV;SASDIFSV;c:\program files\SUPERAntiSpyware\sasdifsv.sys [28.7.2009 і. 10:53 9968] R1 SASKUTIL;SASKUTIL;c:\program files\SUPERAntiSpyware\SASKUTIL.SYS [28.7.2009 і. 10:53 72944] R2 ekrn;Eset Service;c:\program files\ESET\ESET Smart Security\ekrn.exe [21.12.2007 і. 08:21 468224] R2 TuneUp.ProgramStatisticsSvc;TuneUp Program Statistics Service;c:\windows\system32\TUProgSt.exe [28.7.2009 і. 10:30 604416] R3 RTL8187B;Realtek RTL8187B Wireless 802.11b/g 54Mbps USB 2.0 Network Adapter;c:\windows\system32\drivers\RTL8187B.sys [17.10.2008 і. 18:44 288000] R3 SASENUM;SASENUM;c:\program files\SUPERAntiSpyware\SASENUM.SYS [28.7.2009 і. 10:53 7408] R3 WSIMD;wsimd Service;c:\windows\system32\drivers\wsimd.sys [17.10.2008 і. 18:32 57408] HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows NT\CurrentVersion\Svchost - NetSvcs UxTuneUp . Contents of the 'Scheduled Tasks' folder 2009-07-30 c:\windows\Tasks\1-Click Maintenance.job - c:\program files\TuneUp Utilities 2009\OneClickStarter.exe [2009-04-27 13:37] . . ------- Supplementary Scan ------- . uStart Page = about:blank uSearch Page = hxxp://www.google.com uSearch Bar = hxxp://www.google.com/ie mStart Page = about:blank uSearchURL,(Default) = hxxp://www.google.com/search?q=%s IE: &Download All with FlashGet - c:\program files\FlashGet\jc_all.htm IE: &Download with FlashGet - c:\program files\FlashGet\jc_link.htm DPF: DirectAnimation Java Classes - file://c:\windows\Java\classes\dajava.cab DPF: Microsoft XML Parser for Java - file://c:\windows\Java\classes\xmldso.cab FF - ProfilePath - c:\documents and settings\User\Application Data\Mozilla\Firefox\Profiles\p1i9jalj.default\ FF - prefs.js: browser.search.selectedEngine - Google FF - prefs.js: browser.startup.homepage - 127.0.0.1 FF - component: c:\program files\Mozilla Firefox\components\qfaservices.dll ---- FIREFOX POLICIES ---- c:\program files\Mozilla Firefox\greprefs\all.js - pref("backups.number_of_prefs_copies", 1); c:\program files\Mozilla Firefox\greprefs\all.js - pref("capability.policy.default.Window.closed", "allAccess"); c:\program files\Mozilla Firefox\greprefs\all.js - pref("capability.policy.default.Window.document", "allAccess"); c:\program files\Mozilla Firefox\greprefs\all.js - pref("capability.policy.default.Window.frames", "allAccess"); c:\program files\Mozilla Firefox\greprefs\all.js - pref("capability.policy.default.Window.history", "allAccess"); c:\program files\Mozilla Firefox\greprefs\all.js - pref("capability.policy.default.Window.length", "allAccess"); c:\program files\Mozilla Firefox\greprefs\all.js - pref("capability.policy.default.Window.opener", "allAccess"); c:\program files\Mozilla Firefox\greprefs\all.js - pref("capability.policy.default.Window.parent", "allAccess"); c:\program files\Mozilla Firefox\greprefs\all.js - pref("capability.policy.default.Window.self", "allAccess"); c:\program files\Mozilla Firefox\greprefs\all.js - pref("capability.policy.default.Window.top", "allAccess"); c:\program files\Mozilla Firefox\greprefs\all.js - pref("capability.policy.default.Window.window", "allAccess"); c:\program files\Mozilla Firefox\greprefs\all.js - pref("capability.policy.mailnews.DOMParser,parseFromString", "noAccess"); c:\program files\Mozilla Firefox\greprefs\all.js - pref("capability.policy.mailnews.DOMParser,parseFromStream", "noAccess"); c:\program files\Mozilla Firefox\greprefs\all.js - pref("browser.block.target_new_window", false); c:\program files\Mozilla Firefox\greprefs\all.js - pref("dom.disable_window_open_feature.status", false); c:\program files\Mozilla Firefox\greprefs\all.js - pref("advanced.always_load_images", true); c:\program files\Mozilla Firefox\greprefs\all.js - pref("network.protocol-handler.external.help", false); c:\program files\Mozilla Firefox\greprefs\all.js - pref("network.protocol-handler.external-default", 2); c:\program files\Mozilla Firefox\greprefs\all.js - pref("network.http.connect.timeout", 30); // in seconds c:\program files\Mozilla Firefox\greprefs\all.js - pref("network.http.request.timeout", 120); // in seconds c:\program files\Mozilla Firefox\greprefs\all.js - pref("network.image.imageBehavior", 0); // 0-Accept, 1-dontAcceptForeign, 2-dontUse c:\program files\Mozilla Firefox\greprefs\all.js - pref("network.cookie.cookieBehavior", 3); // 0-Accept, 1-dontAcceptForeign, 2-dontUse, 3-p3p c:\program files\Mozilla Firefox\greprefs\all.js - pref("network.cookie.p3plevel", 1); // 0=low, 1=medium, 2=high, 3=custom c:\program files\Mozilla Firefox\greprefs\all.js - pref("network.enablePad", false); // Allow client to do proxy autodiscovery c:\program files\Mozilla Firefox\greprefs\security-prefs.js - pref("security.warn_entering_weak", false); c:\program files\Mozilla Firefox\greprefs\security-prefs.js - pref("security.warn_viewing_mixed", false); c:\program files\Mozilla Firefox\defaults\pref\firefox.js - pref("app.id", "{ec8030f7-c20a-464f-9b0e-13a3a9e97384}"); c:\program files\Mozilla Firefox\defaults\pref\firefox.js - pref("app.version", c:\program files\Mozilla Firefox\defaults\pref\firefox.js - pref("app.extensions.version", "0.10"); c:\program files\Mozilla Firefox\defaults\pref\firefox.js - pref("app.build_id", c:\program files\Mozilla Firefox\defaults\pref\firefox.js - pref("app.update.autoUpdateEnabled", false); // Whether or not background app updates c:\program files\Mozilla Firefox\defaults\pref\firefox.js - pref("app.update.url", "chrome://mozapps/locale/update/update.properties"); c:\program files\Mozilla Firefox\defaults\pref\firefox.js - pref("app.update.updatesAvailable", false); c:\program files\Mozilla Firefox\defaults\pref\firefox.js - pref("app.update.lastUpdateDate", 0); // UTC offset when last App update was c:\program files\Mozilla Firefox\defaults\pref\firefox.js - pref("app.update.performed", false); // Whether or not an update has been c:\program files\Mozilla Firefox\defaults\pref\firefox.js - pref("extensions.update.autoUpdateEnabled", false); c:\program files\Mozilla Firefox\defaults\pref\firefox.js - pref("extensions.update.autoUpdate", false); // Automatically download and install c:\program files\Mozilla Firefox\defaults\pref\firefox.js - pref("extensions.update.interval", 604800000); // Check for updates to Extensions and c:\program files\Mozilla Firefox\defaults\pref\firefox.js - pref("extensions.update.lastUpdateDate", 0); // UTC offset when last Extension/Theme c:\program files\Mozilla Firefox\defaults\pref\firefox.js - pref("extensions.update.severity.threshold", 5);// The number of pending Extension/Theme c:\program files\Mozilla Firefox\defaults\pref\firefox.js - pref("extensions.update.count", 0); // The number of extension/theme/etc c:\program files\Mozilla Firefox\defaults\pref\firefox.js - pref("update.interval", 3600000); // Check each of the above intervals c:\program files\Mozilla Firefox\defaults\pref\firefox.js - pref("update.showSlidingNotification", true); // Windows-only slide-up taskbar c:\program files\Mozilla Firefox\defaults\pref\firefox.js - pref("update.severity", 0); c:\program files\Mozilla Firefox\defaults\pref\firefox.js - pref("general.useragent.vendor", "Firefox"); c:\program files\Mozilla Firefox\defaults\pref\firefox.js - pref("general.useragent.vendorSub", "0.10"); c:\program files\Mozilla Firefox\defaults\pref\firefox.js - pref("browser.startup.homepage", "http://127.0.0.1/"); c:\program files\Mozilla Firefox\defaults\pref\firefox.js - pref("browser.startup.homepage_override.1", false); c:\program files\Mozilla Firefox\defaults\pref\firefox.js - pref("browser.turbo.enabled", false); c:\program files\Mozilla Firefox\defaults\pref\firefox.js - pref("browser.search.param.Google.1.name", "chrome://browser/content/searchconfig.properties"); c:\program files\Mozilla Firefox\defaults\pref\firefox.js - pref("browser.search.param.Google.1.custom", "chrome://browser/content/searchconfig.properties"); c:\program files\Mozilla Firefox\defaults\pref\firefox.js - pref("browser.search.param.Google.1.default", "chrome://browser/content/searchconfig.properties"); c:\program files\Mozilla Firefox\defaults\pref\firefox.js - pref("dom.disable_open_during_load", false); c:\program files\Mozilla Firefox\defaults\pref\firefox.js - pref("network.protocols.useSystemDefaults", false); // set to true if user links should use system default handlers c:\program files\Mozilla Firefox\defaults\pref\firefox.js - pref("update_notifications.enabled", true); c:\program files\Mozilla Firefox\defaults\pref\firefox.js - pref("update_notifications.provider.0.frequency", 7); // number of days c:\program files\Mozilla Firefox\defaults\pref\firefox.js - pref("browser.xul.error_pages.enabled", false); c:\program files\Mozilla Firefox\defaults\pref\firefox.js - pref("network.protocol-handler.external.news" , true); // for news c:\program files\Mozilla Firefox\defaults\pref\firefox.js - pref("security.warn_entering_weak.show_once", false); c:\program files\Mozilla Firefox\defaults\pref\firefox.js - pref("security.warn_viewing_mixed.show_once", false); c:\program files\Mozilla Firefox\defaults\pref\firefox.js - pref("pfs.datasource.url", "chrome://mozapps/locale/plugins/plugins.properties"); . ************************************************************************** catchme 0.3.1398 W2K/XP/Vista - rootkit/stealth malware detector by Gmer, http://www.gmer.net Rootkit scan 2009-07-30 17:03 Windows 5.1.2600 Service Pack 2 NTFS scanning hidden processes ... scanning hidden autostart entries ... scanning hidden files ... scan completed successfully hidden files: 0 ************************************************************************** [HKEY_LOCAL_MACHINE\System\ControlSet001\Services\MySql] "ImagePath"="C:/BonArtMC/database/bin/mysqld-nt.exe" [HKEY_LOCAL_MACHINE\System\ControlSet001\Services\MySql] "ImagePath"="C:/BonArtMC/database/bin/mysqld-nt.exe" . --------------------- DLLs Loaded Under Running Processes --------------------- - - - - - - - > 'winlogon.exe'(1464) c:\program files\SUPERAntiSpyware\SASWINLO.dll - - - - - - - > 'explorer.exe'(1148) c:\windows\system32\newdll.dll . Completion time: 2009-07-30 17:04 ComboFix-quarantined-files.txt 2009-07-30 14:04 ComboFix2.txt 2009-07-30 08:02 Pre-Run: 90 838 675 456 bytes free Post-Run: 90 799 591 424 bytes free 201 ROOTREPEAL © AD, 2007-2009 ================================================== Scan Start Time: 2009/07/30 16:55 Program Version: Version 1.3.3.0 Windows Version: Windows XP SP2 ================================================== Drivers ------------------- Name: 00000055 Image Path: \Driver\00000055 Address: 0x00000000 Size: 0 File Visible: No Signed: - Status: - Name: dump_atapi.sys Image Path: C:\WINDOWS\System32\Drivers\dump_atapi.sys Address: 0xA81F9000 Size: 98304 File Visible: No Signed: - Status: - Name: dump_WMILIB.SYS Image Path: C:\WINDOWS\System32\Drivers\dump_WMILIB.SYS Address: 0xBA5D6000 Size: 8192 File Visible: No Signed: - Status: - Name: rootrepeal.sys Image Path: C:\WINDOWS\system32\drivers\rootrepeal.sys Address: 0xA7274000 Size: 49152 File Visible: No Signed: - Status: - Name: wggIguo.sys Image Path: wggIguo.sys Address: 0xBA0A8000 Size: 61440 File Visible: No Signed: - Status: - SSDT ------------------- #: 041 Function Name: NtCreateKey Status: Hooked by "sptd.sys" at address 0xb9ed9ac8 #: 071 Function Name: NtEnumerateKey Status: Hooked by "sptd.sys" at address 0xb9ed9c22 #: 073 Function Name: NtEnumerateValueKey Status: Hooked by "sptd.sys" at address 0xb9ed9f9a #: 119 Function Name: NtOpenKey Status: Hooked by "sptd.sys" at address 0xb9ed998e #: 160 Function Name: NtQueryKey Status: Hooked by "sptd.sys" at address 0xb9eda064 #: 177 Function Name: NtQueryValueKey Status: Hooked by "sptd.sys" at address 0xb9ed9efc #: 247 Function Name: NtSetValueKey Status: Hooked by "sptd.sys" at address 0xb9eda0ec #: 257 Function Name: NtTerminateProcess Status: Hooked by "C:\Program Files\SUPERAntiSpyware\SASKUTIL.sys" at address 0xa8337df0 ==EOF==
-
Деинсталирах ComboBox и изпълних останалите стъпки. Резултатът е: GMER 1.0.15.15011 [gmer.exe] - http://www.gmer.net Rootkit scan 2009-07-30 15:55:28 Windows 5.1.2600 Service Pack 2 ---- System - GMER 1.0.15 ---- SSDT sptd.sys ZwCreateKey [0xB9ED9AC8] SSDT sptd.sys ZwEnumerateKey [0xB9ED9C22] SSDT sptd.sys ZwEnumerateValueKey [0xB9ED9F9A] SSDT sptd.sys ZwOpenKey [0xB9ED998E] SSDT sptd.sys ZwQueryKey [0xB9EDA064] SSDT sptd.sys ZwQueryValueKey [0xB9ED9EFC] SSDT sptd.sys ZwSetValueKey [0xB9EDA0EC] SSDT \??\C:\Program Files\SUPERAntiSpyware\SASKUTIL.sys (SASKUTIL.SYS/SUPERAdBlocker.com and SUPERAntiSpyware.com) ZwTerminateProcess [0xA7F01DF0] INT 0x06 \??\C:\WINDOWS\system32\drivers\Haspnt.sys (HASP Kernel Device Driver for Windows NT/Aladdin Knowledge Systems) A87B916D INT 0x0E \??\C:\WINDOWS\system32\drivers\Haspnt.sys (HASP Kernel Device Driver for Windows NT/Aladdin Knowledge Systems) A87B8FC2 ---- Kernel code sections - GMER 1.0.15 ---- ? C:\WINDOWS\system32\drivers\sptd.sys The process cannot access the file because it is being used by another process. ? C:\WINDOWS\System32\Drivers\SPTD2525.SYS The process cannot access the file because it is being used by another process. .text dtscsi.sys!A0DB34FC6FE35D429A28ADDE5467D4D7 B95C34F0 16 Bytes [A2, BA, FD, C2, 36, 45, C2, ...] .text dtscsi.sys!A0DB34FC6FE35D429A28ADDE5467D4D7 + 11 B95C3501 31 Bytes [20, 5C, B9, AD, D2, 44, 7B, ...] ? C:\WINDOWS\System32\Drivers\dtscsi.sys The process cannot access the file because it is being used by another process. ---- User code sections - GMER 1.0.15 ---- .text C:\Program Files\ESET\ESET Smart Security\ekrn.exe[872] kernel32.dll!SetUnhandledExceptionFilter 7C810386 4 Bytes [C2, 04, 00, 00] ---- Kernel IAT/EAT - GMER 1.0.15 ---- IAT atapi.sys[HAL.dll!READ_PORT_UCHAR] [b9ED5AD2] sptd.sys IAT atapi.sys[HAL.dll!READ_PORT_BUFFER_USHORT] [b9ED5C0E] sptd.sys IAT atapi.sys[HAL.dll!READ_PORT_USHORT] [b9ED5B96] sptd.sys IAT atapi.sys[HAL.dll!WRITE_PORT_BUFFER_USHORT] [b9ED676C] sptd.sys IAT atapi.sys[HAL.dll!WRITE_PORT_UCHAR] [b9ED6642] sptd.sys IAT \SystemRoot\System32\DRIVERS\i8042prt.sys[HAL.dll!READ_PORT_UCHAR] [b9EF8056] sptd.sys ---- Devices - GMER 1.0.15 ---- Device \FileSystem\Ntfs \Ntfs 8A6B50E8 AttachedDevice \FileSystem\Ntfs \Ntfs eamon.sys (Amon monitor/ESET) Device \FileSystem\Fastfat \FatCdrom 8A4396C8 AttachedDevice \Driver\Tcpip \Device\Ip epfwtdi.sys (Eset Personal Firewall TDI filter/ESET) Device \Driver\NetBT \Device\NetBT_Tcpip_{E8667CAB-617D-4244-8EA5-90026D2346E4} 8A2FB918 AttachedDevice \Driver\Kbdclass \Device\KeyboardClass0 SynTP.sys (Synaptics Touchpad Driver/Synaptics, Inc.) AttachedDevice \Driver\Kbdclass \Device\KeyboardClass1 SynTP.sys (Synaptics Touchpad Driver/Synaptics, Inc.) Device \Driver\00000108 \Device\00000052 sptd.sys Device \Driver\dmio \Device\DmControl\DmIoDaemon 8A68C9C0 Device \Driver\dmio \Device\DmControl\DmConfig 8A68C9C0 Device \Driver\dmio \Device\DmControl\DmPnP 8A68C9C0 Device \Driver\dmio \Device\DmControl\DmInfo 8A68C9C0 AttachedDevice \Driver\Tcpip \Device\Tcp epfwtdi.sys (Eset Personal Firewall TDI filter/ESET) Device \Driver\Ftdisk \Device\HarddiskVolume1 8A68CC78 Device \Driver\Ftdisk \Device\HarddiskVolume2 8A68CC78 Device \Driver\Cdrom \Device\CdRom0 8A4C5660 Device \FileSystem\Rdbss \Device\FsWrap 8A2E95D0 Device \Driver\Cdrom \Device\CdRom1 8A4C5660 Device \Driver\NetBT \Device\NetBt_Wins_Export 8A2FB918 Device \Driver\NetBT \Device\NetbiosSmb 8A2FB918 AttachedDevice \Driver\Tcpip \Device\Udp epfwtdi.sys (Eset Personal Firewall TDI filter/ESET) Device \Driver\Disk \Device\Harddisk0\DR0 8A68C450 AttachedDevice \Driver\Tcpip \Device\RawIp epfwtdi.sys (Eset Personal Firewall TDI filter/ESET) Device \FileSystem\MRxSmb \Device\LanmanDatagramReceiver 8A1B3EB0 Device \FileSystem\MRxSmb \Device\LanmanRedirector 8A1B3EB0 Device \FileSystem\Npfs \Device\NamedPipe 8A3EC500 Device \Driver\Ftdisk \Device\FtControl 8A68CC78 Device \FileSystem\Msfs \Device\Mailslot 8A3AAEB0 Device \Driver\NetBT \Device\NetBT_Tcpip_{49936FD2-A77A-4602-B1D5-1DEF6B68A758} 8A2FB918 Device \Driver\dtscsi \Device\Scsi\dtscsi1Port4Path0Target0Lun0 8A33F0E8 Device \Driver\dtscsi \Device\Scsi\dtscsi1 8A33F0E8 Device \FileSystem\Fastfat \Fat 8A4396C8 AttachedDevice \FileSystem\Fastfat \Fat fltmgr.sys (Microsoft Filesystem Filter Manager/Microsoft Corporation) AttachedDevice \FileSystem\Fastfat \Fat eamon.sys (Amon monitor/ESET) Device \FileSystem\Cdfs \Cdfs 8A37B0E8 ---- Registry - GMER 1.0.15 ---- Reg HKLM\SYSTEM\CurrentControlSet\Services\BTHPORT\Parameters\Keys\000cbf010fff Reg HKLM\SYSTEM\CurrentControlSet\Services\sptd\Cfg@s0 -279053766 Reg HKLM\SYSTEM\CurrentControlSet\Services\sptd\Cfg@s1 -2061786386 Reg HKLM\SYSTEM\CurrentControlSet\Services\sptd\Cfg@s2 870382081 Reg HKLM\SYSTEM\CurrentControlSet\Services\sptd\Cfg@h0 1 Reg HKLM\SYSTEM\CurrentControlSet\Services\sptd\Cfg\19659239224E364682FA4BAF72C53EA4 Reg HKLM\SYSTEM\CurrentControlSet\Services\sptd\Cfg\19659239224E364682FA4BAF72C53EA4@p0 C:\Program Files\DAEMON Tools\ Reg HKLM\SYSTEM\CurrentControlSet\Services\sptd\Cfg\19659239224E364682FA4BAF72C53EA4@h0 0 Reg HKLM\SYSTEM\CurrentControlSet\Services\sptd\Cfg\19659239224E364682FA4BAF72C53EA4@khjeh 0x93 0x06 0x52 0x37 ... Reg HKLM\SYSTEM\CurrentControlSet\Services\sptd\Cfg\19659239224E364682FA4BAF72C53EA4\00000001 Reg HKLM\SYSTEM\CurrentControlSet\Services\sptd\Cfg\19659239224E364682FA4BAF72C53EA4\00000001@a0 0x20 0x01 0x00 0x00 ... Reg HKLM\SYSTEM\CurrentControlSet\Services\sptd\Cfg\19659239224E364682FA4BAF72C53EA4\00000001@khjeh 0xE9 0x80 0x80 0xCE ... Reg HKLM\SYSTEM\CurrentControlSet\Services\sptd\Cfg\19659239224E364682FA4BAF72C53EA4\00000001\0Jf40 Reg HKLM\SYSTEM\CurrentControlSet\Services\sptd\Cfg\19659239224E364682FA4BAF72C53EA4\00000001\0Jf40@khjeh 0xE6 0x66 0x04 0xE9 ... Reg HKLM\SYSTEM\ControlSet003\Services\BTHPORT\Parameters\Keys\000cbf010fff (not active ControlSet) Reg HKLM\SYSTEM\ControlSet003\Services\sptd\Cfg\19659239224E364682FA4BAF72C53EA4 (not active ControlSet) Reg HKLM\SYSTEM\ControlSet003\Services\sptd\Cfg\19659239224E364682FA4BAF72C53EA4@p0 C:\Program Files\DAEMON Tools\ Reg HKLM\SYSTEM\ControlSet003\Services\sptd\Cfg\19659239224E364682FA4BAF72C53EA4@h0 0 Reg HKLM\SYSTEM\ControlSet003\Services\sptd\Cfg\19659239224E364682FA4BAF72C53EA4@khjeh 0x93 0x06 0x52 0x37 ... Reg HKLM\SYSTEM\ControlSet003\Services\sptd\Cfg\19659239224E364682FA4BAF72C53EA4\00000001 (not active ControlSet) Reg HKLM\SYSTEM\ControlSet003\Services\sptd\Cfg\19659239224E364682FA4BAF72C53EA4\00000001@a0 0x20 0x01 0x00 0x00 ... Reg HKLM\SYSTEM\ControlSet003\Services\sptd\Cfg\19659239224E364682FA4BAF72C53EA4\00000001@khjeh 0xE9 0x80 0x80 0xCE ... Reg HKLM\SYSTEM\ControlSet003\Services\sptd\Cfg\19659239224E364682FA4BAF72C53EA4\00000001\0Jf40 (not active ControlSet) Reg HKLM\SYSTEM\ControlSet003\Services\sptd\Cfg\19659239224E364682FA4BAF72C53EA4\00000001\0Jf40@khjeh 0xE6 0x66 0x04 0xE9 ... ---- EOF - GMER 1.0.15 ---- DDS (Ver_09-07-30.01) - NTFSx86 Run by User at 16:13:19,90 on 30.07.2009 г. Internet Explorer: 6.0.2900.2180 Microsoft Windows XP Professional 5.1.2600.2.1251.359.1033.18.2038.1569 [GMT 3:00] AV: ESET Smart Security 3.0 *On-access scanning disabled* (Updated) {E5E70D32-0101-4F12-8FB0-D96ACA4F34C0} FW: ESET Personal firewall *enabled* {E5E70D32-0101-4340-86A3-A7B0F1C8FFE0} ============== Running Processes =============== C:\WINDOWS\system32\svchost -k DcomLaunch svchost.exe C:\WINDOWS\System32\svchost.exe -k netsvcs svchost.exe svchost.exe C:\WINDOWS\system32\spoolsv.exe C:\WINDOWS\System32\acs.exe svchost.exe C:\Program Files\ESET\ESET Smart Security\ekrn.exe C:\BonArtMC\database\bin\mysqld-nt.exe C:\WINDOWS\System32\svchost.exe -k imgsvc C:\WINDOWS\System32\TUProgSt.exe C:\WINDOWS\system32\wuauclt.exe C:\WINDOWS\Explorer.EXE C:\WINDOWS\RTHDCPL.EXE C:\WINDOWS\System32\igfxtray.exe C:\WINDOWS\System32\igfxpers.exe C:\WINDOWS\System32\igfxsrvc.exe C:\Program Files\Synaptics\SynTP\SynTPEnh.exe C:\Program Files\Atheros\ACU.exe C:\BonArtMC\BonArt.exe C:\Program Files\ESET\ESET Smart Security\egui.exe C:\Program Files\Adobe\Reader 9.0\Reader\Reader_sl.exe C:\Program Files\Google\GoogleToolbarNotifier\GoogleToolbarNotifier.exe C:\WINDOWS\system32\ctfmon.exe C:\WINDOWS\Datecs\Flex2K.exe C:\Program Files\Internet Explorer\iexplore.exe C:\WINDOWS\system32\wscntfy.exe C:\Documents and Settings\User\Desktop\dds.pif C:\BonArtMC\php\php.exe ============== Pseudo HJT Report =============== uStart Page = about:blank uSearch Page = hxxp://www.google.com uSearch Bar = hxxp://www.google.com/ie mStart Page = about:blank uSearchURL,(Default) = hxxp://www.google.com/search?q=%s BHO: Adobe PDF Link Helper: {18df081c-e8ad-4283-a596-fa578c2ebdc3} - c:\program files\common files\adobe\acrobat\activex\AcroIEHelperShim.dll BHO: Google Toolbar Helper: {aa58ed58-01dd-4d91-8333-cf10577473f7} - c:\program files\google\google toolbar\GoogleToolbar.dll BHO: Google Toolbar Notifier BHO: {af69de43-7d58-4638-b6fa-ce66b5ad205d} - c:\program files\google\googletoolbarnotifier\5.1.1309.15642\swg.dll BHO: Google Dictionary Compression sdch: {c84d72fe-e17d-4195-bb24-76c02e2e7c4e} - c:\program files\google\google toolbar\component\fastsearch_A8904FB862BD9564.dll BHO: FlashGet GetFlash Class: {f156768e-81ef-470c-9057-481ba8380dba} - c:\program files\flashget\getflash.dll TB: Google Toolbar: {2318c2b1-4965-11d4-9b18-009027a5cd4f} - c:\program files\google\google toolbar\GoogleToolbar.dll TB: {2C688203-7EB3-4327-9995-1CB417BA23F9} - No File EB: {32683183-48a0-441b-a342-7c2a440a9478} - No File uRun: [swg] c:\program files\google\googletoolbarnotifier\GoogleToolbarNotifier.exe uRun: [ctfmon.exe] c:\windows\system32\ctfmon.exe uRun: [sUPERAntiSpyware] c:\program files\superantispyware\SUPERAntiSpyware.exe mRun: [RTHDCPL] RTHDCPL.EXE mRun: [igfxTray] c:\windows\system32\igfxtray.exe mRun: [HotKeysCmds] c:\windows\system32\hkcmd.exe mRun: [Persistence] c:\windows\system32\igfxpers.exe mRun: [synTPEnh] c:\program files\synaptics\syntp\SynTPEnh.exe mRun: [ACU] "c:\program files\atheros\ACU.exe" -nogui mRun: [bAE3FA] c:\bonartmc\BonArt.exe mRun: [egui] "c:\program files\eset\eset smart security\egui.exe" /hide /waitservice mRun: [Adobe Reader Speed Launcher] "c:\program files\adobe\reader 9.0\reader\Reader_sl.exe" StartupFolder: c:\docume~1\user\startm~1\programs\startup\abyssws.lnk - c:\bonartmc\abyssws.exe StartupFolder: c:\docume~1\alluse~1\startm~1\programs\startup\flexty~1.lnk - c:\windows\datecs\Flex2K.exe IE: &Download All with FlashGet - c:\program files\flashget\jc_all.htm IE: &Download with FlashGet - c:\program files\flashget\jc_link.htm IE: {85d1f590-48f4-11d9-9669-0800200c9a66} - %windir%\bdoscandel.exe DPF: DirectAnimation Java Classes - file://c:\windows\java\classes\dajava.cab DPF: Microsoft XML Parser for Java - file://c:\windows\java\classes\xmldso.cab DPF: {166B1BCA-3F9C-11CF-8075-444553540000} - hxxp://download.macromedia.com/pub/shockwave/cabs/director/sw.cab DPF: {5D86DDB5-BDF9-441B-9E9E-D4730F4EE499} - hxxp://download.bitdefender.com/resources/scanner/sources/en/scan8/oscan8.cab DPF: {8FFBE65D-2C9C-4669-84BD-5829DC0B603C} - hxxp://fpdownload.macromedia.com/get/flashplayer/current/polarbear/ultrashim.cab Filter: x-sdch - {B1759355-3EEC-4C1E-B0F1-B719FE26E377} - c:\program files\google\google toolbar\component\fastsearch_A8904FB862BD9564.dll Handler: skype4com - {FFC8B962-9B40-4DFF-9458-1830C7DD7F5D} - c:\progra~1\common~1\skype\SKYPE4~1.DLL Notify: !SASWinLogon - c:\program files\superantispyware\SASWINLO.dll Notify: igfxcui - igfxdev.dll SEH: SABShellExecuteHook Class: {5ae067d3-9afb-48e0-853a-ebb7f4a000da} - c:\program files\superantispyware\SASSEH.DLL ================= FIREFOX =================== FF - ProfilePath - c:\docume~1\user\applic~1\mozilla\firefox\profiles\p1i9jalj.default\ FF - prefs.js: browser.search.selectedEngine - Google FF - prefs.js: browser.startup.homepage - 127.0.0.1 FF - component: c:\program files\mozilla firefox\components\qfaservices.dll ---- FIREFOX POLICIES ---- c:\program files\mozilla firefox\greprefs\all.js - pref("backups.number_of_prefs_copies", 1); c:\program files\mozilla firefox\greprefs\all.js - pref("capability.policy.default.Window.closed", "allAccess"); c:\program files\mozilla firefox\greprefs\all.js - pref("capability.policy.default.Window.document", "allAccess"); c:\program files\mozilla firefox\greprefs\all.js - pref("capability.policy.default.Window.frames", "allAccess"); c:\program files\mozilla firefox\greprefs\all.js - pref("capability.policy.default.Window.history", "allAccess"); c:\program files\mozilla firefox\greprefs\all.js - pref("capability.policy.default.Window.length", "allAccess"); c:\program files\mozilla firefox\greprefs\all.js - pref("capability.policy.default.Window.opener", "allAccess"); c:\program files\mozilla firefox\greprefs\all.js - pref("capability.policy.default.Window.parent", "allAccess"); c:\program files\mozilla firefox\greprefs\all.js - pref("capability.policy.default.Window.self", "allAccess"); c:\program files\mozilla firefox\greprefs\all.js - pref("capability.policy.default.Window.top", "allAccess"); c:\program files\mozilla firefox\greprefs\all.js - pref("capability.policy.default.Window.window", "allAccess"); c:\program files\mozilla firefox\greprefs\all.js - pref("capability.policy.mailnews.DOMParser,parseFromString", "noAccess"); c:\program files\mozilla firefox\greprefs\all.js - pref("capability.policy.mailnews.DOMParser,parseFromStream", "noAccess"); c:\program files\mozilla firefox\greprefs\all.js - pref("browser.block.target_new_window", false); c:\program files\mozilla firefox\greprefs\all.js - pref("dom.disable_window_open_feature.status", false); c:\program files\mozilla firefox\greprefs\all.js - pref("advanced.always_load_images", true); c:\program files\mozilla firefox\greprefs\all.js - pref("network.protocol-handler.external.help", false); c:\program files\mozilla firefox\greprefs\all.js - pref("network.protocol-handler.external-default", 2); c:\program files\mozilla firefox\greprefs\all.js - pref("network.http.connect.timeout", 30); // in seconds c:\program files\mozilla firefox\greprefs\all.js - pref("network.http.request.timeout", 120); // in seconds c:\program files\mozilla firefox\greprefs\all.js - pref("network.image.imageBehavior", 0); // 0-Accept, 1-dontAcceptForeign, 2-dontUse c:\program files\mozilla firefox\greprefs\all.js - pref("network.cookie.cookieBehavior", 3); // 0-Accept, 1-dontAcceptForeign, 2-dontUse, 3-p3p c:\program files\mozilla firefox\greprefs\all.js - pref("network.cookie.p3plevel", 1); // 0=low, 1=medium, 2=high, 3=custom c:\program files\mozilla firefox\greprefs\all.js - pref("network.enablePad", false); // Allow client to do proxy autodiscovery c:\program files\mozilla firefox\greprefs\security-prefs.js - pref("security.warn_entering_weak", false); c:\program files\mozilla firefox\greprefs\security-prefs.js - pref("security.warn_viewing_mixed", false); c:\program files\mozilla firefox\defaults\pref\firefox.js - pref("app.id", "{ec8030f7-c20a-464f-9b0e-13a3a9e97384}"); c:\program files\mozilla firefox\defaults\pref\firefox.js - pref("app.version", c:\program files\mozilla firefox\defaults\pref\firefox.js - pref("app.extensions.version", "0.10"); c:\program files\mozilla firefox\defaults\pref\firefox.js - pref("app.build_id", c:\program files\mozilla firefox\defaults\pref\firefox.js - pref("app.update.autoUpdateEnabled", false); // Whether or not background app updates c:\program files\mozilla firefox\defaults\pref\firefox.js - pref("app.update.url", "chrome://mozapps/locale/update/update.properties"); c:\program files\mozilla firefox\defaults\pref\firefox.js - pref("app.update.updatesAvailable", false); c:\program files\mozilla firefox\defaults\pref\firefox.js - pref("app.update.lastUpdateDate", 0); // UTC offset when last App update was c:\program files\mozilla firefox\defaults\pref\firefox.js - pref("app.update.performed", false); // Whether or not an update has been c:\program files\mozilla firefox\defaults\pref\firefox.js - pref("extensions.update.autoUpdateEnabled", false); c:\program files\mozilla firefox\defaults\pref\firefox.js - pref("extensions.update.autoUpdate", false); // Automatically download and install c:\program files\mozilla firefox\defaults\pref\firefox.js - pref("extensions.update.interval", 604800000); // Check for updates to Extensions and c:\program files\mozilla firefox\defaults\pref\firefox.js - pref("extensions.update.lastUpdateDate", 0); // UTC offset when last Extension/Theme c:\program files\mozilla firefox\defaults\pref\firefox.js - pref("extensions.update.severity.threshold", 5);// The number of pending Extension/Theme c:\program files\mozilla firefox\defaults\pref\firefox.js - pref("extensions.update.count", 0); // The number of extension/theme/etc c:\program files\mozilla firefox\defaults\pref\firefox.js - pref("update.interval", 3600000); // Check each of the above intervals c:\program files\mozilla firefox\defaults\pref\firefox.js - pref("update.showSlidingNotification", true); // Windows-only slide-up taskbar c:\program files\mozilla firefox\defaults\pref\firefox.js - pref("update.severity", 0); c:\program files\mozilla firefox\defaults\pref\firefox.js - pref("general.useragent.vendor", "Firefox"); c:\program files\mozilla firefox\defaults\pref\firefox.js - pref("general.useragent.vendorSub", "0.10"); c:\program files\mozilla firefox\defaults\pref\firefox.js - pref("browser.startup.homepage", "http://127.0.0.1/"); c:\program files\mozilla firefox\defaults\pref\firefox.js - pref("browser.startup.homepage_override.1", false); c:\program files\mozilla firefox\defaults\pref\firefox.js - pref("browser.turbo.enabled", false); c:\program files\mozilla firefox\defaults\pref\firefox.js - pref("browser.search.param.Google.1.name", "chrome://browser/content/searchconfig.properties"); c:\program files\mozilla firefox\defaults\pref\firefox.js - pref("browser.search.param.Google.1.custom", "chrome://browser/content/searchconfig.properties"); c:\program files\mozilla firefox\defaults\pref\firefox.js - pref("browser.search.param.Google.1.default", "chrome://browser/content/searchconfig.properties"); c:\program files\mozilla firefox\defaults\pref\firefox.js - pref("dom.disable_open_during_load", false); c:\program files\mozilla firefox\defaults\pref\firefox.js - pref("network.protocols.useSystemDefaults", false); // set to true if user links should use system default handlers c:\program files\mozilla firefox\defaults\pref\firefox.js - pref("update_notifications.enabled", true); c:\program files\mozilla firefox\defaults\pref\firefox.js - pref("update_notifications.provider.0.frequency", 7); // number of days c:\program files\mozilla firefox\defaults\pref\firefox.js - pref("browser.xul.error_pages.enabled", false); c:\program files\mozilla firefox\defaults\pref\firefox.js - pref("network.protocol-handler.external.news" , true); // for news c:\program files\mozilla firefox\defaults\pref\firefox.js - pref("security.warn_entering_weak.show_once", false); c:\program files\mozilla firefox\defaults\pref\firefox.js - pref("security.warn_viewing_mixed.show_once", false); c:\program files\mozilla firefox\defaults\pref\firefox.js - pref("pfs.datasource.url", "chrome://mozapps/locale/plugins/plugins.properties"); ============= SERVICES / DRIVERS =============== R1 SASDIFSV;SASDIFSV;c:\program files\superantispyware\sasdifsv.sys [2009-7-28 9968] R1 SASKUTIL;SASKUTIL;c:\program files\superantispyware\SASKUTIL.SYS [2009-7-28 72944] R2 ekrn;Eset Service;c:\program files\eset\eset smart security\ekrn.exe [2007-12-21 468224] R2 TuneUp.ProgramStatisticsSvc;TuneUp Program Statistics Service;c:\windows\system32\TUProgSt.exe [2009-7-28 604416] R3 RTL8187B;Realtek RTL8187B Wireless 802.11b/g 54Mbps USB 2.0 Network Adapter;c:\windows\system32\drivers\RTL8187B.sys [2008-10-17 288000] R3 SASENUM;SASENUM;c:\program files\superantispyware\SASENUM.SYS [2009-7-28 7408] R3 WSIMD;wsimd Service;c:\windows\system32\drivers\wsimd.sys [2008-10-17 57408] =============== Created Last 30 ================ 2009-07-30 11:01 <DIR> -cd----- c:\windows\system32\dllcache\cache 2009-07-30 10:40 <DIR> --d----- c:\docume~1\alluse~1\applic~1\SUPERAntiSpyware.com 2009-07-30 10:39 <DIR> --d----- c:\program files\SUPERAntiSpyware 2009-07-30 10:39 <DIR> --d----- c:\docume~1\user\applic~1\SUPERAntiSpyware.com 2009-07-30 10:39 <DIR> --d----- c:\program files\common files\Wise Installation Wizard 2009-07-30 10:32 <DIR> --d----- c:\documents and settings\user\DoctorWeb 2009-07-28 10:30 604,416 a------- c:\windows\system32\TUProgSt.exe 2009-07-28 10:30 28,928 a------- c:\windows\system32\uxtuneup.dll 2009-07-28 10:30 361,216 a------- c:\windows\system32\TuneUpDefragService.exe 2009-07-28 10:24 <DIR> --d----- c:\docume~1\user\applic~1\TuneUp Software 2009-07-28 10:24 <DIR> --d----- c:\docume~1\alluse~1\applic~1\TuneUp Software 2009-07-28 10:24 <DIR> --d----- c:\program files\TuneUp Utilities 2009 2009-07-28 10:22 <DIR> --d----- c:\program files\Enigma Software Group 2009-07-28 10:19 <DIR> --d----- c:\docume~1\user\applic~1\ESET 2009-07-28 10:18 <DIR> --d----- c:\program files\ESET 2009-07-28 10:05 <DIR> --d----- c:\docume~1\user\applic~1\Malwarebytes 2009-07-28 10:05 38,160 a------- c:\windows\system32\drivers\mbamswissarmy.sys 2009-07-28 10:05 19,096 a------- c:\windows\system32\drivers\mbam.sys 2009-07-28 10:05 <DIR> --d----- c:\docume~1\alluse~1\applic~1\Malwarebytes 2009-07-28 10:05 <DIR> --d----- c:\program files\Malwarebytes' Anti-Malware ==================== Find3M ==================== ============= FINISH: 16:13:30,67 =============== UNLESS SPECIFICALLY INSTRUCTED, DO NOT POST THIS LOG. IF REQUESTED, ZIP IT UP & ATTACH IT DDS (Ver_09-07-30.01) Microsoft Windows XP Professional Boot Device: \Device\HarddiskVolume1 Install Date: 17.10.2008 г. 13:11:42 System Uptime: 30.7.2009 г. 16:07:36 (0 hours ago) Motherboard: Intel Corp. | | Base Board Product Name Processor: Intel® Pentium® Dual CPU T2370 @ 1.73GHz | CPU | 1729/533mhz Processor: Intel® Pentium® Dual CPU T2370 @ 1.73GHz | CPU | 795/533mhz ==== Disk Partitions ========================= C: is FIXED (NTFS) - 98 GiB total, 84,645 GiB free. D: is FIXED (NTFS) - 135 GiB total, 25,57 GiB free. E: is CDROM () F: is CDROM () ==== Disabled Device Manager Items ============= Class GUID: {4D36E97E-E325-11CE-BFC1-08002BE10318} Description: Device ID: ACPI\TOS1901\2&DABA3FF&0 Manufacturer: Name: PNP Device ID: ACPI\TOS1901\2&DABA3FF&0 Service: Class GUID: {4D36E97E-E325-11CE-BFC1-08002BE10318} Description: SM Bus Controller Device ID: PCI\VEN_8086&DEV_283E&SUBSYS_FF641179&REV_03\3&B1BFB68&0&FB Manufacturer: Name: SM Bus Controller PNP Device ID: PCI\VEN_8086&DEV_283E&SUBSYS_FF641179&REV_03\3&B1BFB68&0&FB Service: ==== System Restore Points =================== RP1: 30.7.2009 г. 16:08:17 - System Checkpoint ==== Installed Programs ====================== ABBYY FineReader 7.0 Professional Edition ACE Mega CoDecS Pack Acrobat.com Adobe AIR Adobe Bridge 1.0 Adobe Common File Installer Adobe Flash Player 10 ActiveX Adobe Help Center 1.0 Adobe Photoshop CS2 Adobe Reader 9 Adobe Shockwave Player Adobe Stock Photos 1.0 Atheros Client Utility BS.Player FREE Camera Assistant Software for Toshiba ESET Smart Security FlashGet 1.9.6.1073 FlexType 2K Google Earth Google Toolbar for Internet Explorer Google Updater High Definition Audio Driver Package - KB888111 HijackThis 2.0.2 Intel® Graphics Media Accelerator Driver Lexmark Software Uninstall Malwarebytes' Anti-Malware Microsoft Office Professional Edition 2003 Microsoft Visual C++ 2005 Redistributable MV2Player (remove only) Nero 6 Ultra Edition REALTEK GbE & FE Ethernet PCI-E NIC Driver Realtek High Definition Audio Driver REALTEK RTL8187B Wireless LAN Driver Realtek USB 2.0 Card Reader Sentinel Protection Installer 7.0.0 Skype™ 3.8 Soft Modem with SmartCP Spybot - Search & Destroy SpyHunter SUPERAntiSpyware Free Edition Synaptics Pointing Device Driver TuneUp Utilities 2009 WebFldrs XP WebTrance3.0 (aaeinoaee?aia) Winamp Windows Media Format Runtime Windows XP Service Pack 2 WinRAR archiver ==== Event Viewer Messages From Past Week ======== 30.7.2009 і. 15:16:54, error: Dhcp [1002] - The IP address lease 192.168.0.102 for the Network Card with network address 001B9EE39A16 has been denied by the DHCP server 0.0.0.0 (The DHCP Server sent a DHCPNACK message). 30.7.2009 і. 10:59:48, error: Service Control Manager [7009] - Timeout (30000 milliseconds) waiting for the PEVSystemStart service to connect. 30.7.2009 і. 10:58:07, error: Service Control Manager [7009] - Timeout (30000 milliseconds) waiting for the PEVSystemStart service to connect. 30.7.2009 і. 10:45:39, error: Service Control Manager [7009] - Timeout (30000 milliseconds) waiting for the PEVSystemStart service to connect. 28.7.2009 і. 11:44:07, error: DCOM [10005] - DCOM got error "%1084" attempting to start the service EventSystem with arguments "" in order to run the server: {1BE1F766-5536-11D1-B726-00C04FB926AF} 28.7.2009 і. 11:39:46, error: DCOM [10005] - DCOM got error "%1084" attempting to start the service StiSvc with arguments "" in order to run the server: {A1F4E726-8CF1-11D1-BF92-0060081ED811} 28.7.2009 і. 11:39:28, error: DCOM [10005] - DCOM got error "%1084" attempting to start the service StiSvc with arguments "" in order to run the server: {A1F4E726-8CF1-11D1-BF92-0060081ED811} 28.7.2009 і. 11:39:28, error: DCOM [10005] - DCOM got error "%1084" attempting to start the service StiSvc with arguments "" in order to run the server: {A1F4E726-8CF1-11D1-BF92-0060081ED811} 28.7.2009 і. 11:35:46, error: Service Control Manager [7026] - The following boot-start or system-start driver(s) failed to load: AFD easdrv epfwtdi Fips intelppm IPSec MRxSmb NetBIOS NetBT RasAcd Rdbss Tcpip 28.7.2009 і. 11:35:46, error: Service Control Manager [7001] - The TCP/IP NetBIOS Helper service depends on the AFD Networking Support Environment service which failed to start because of the following error: A device attached to the system is not functioning. 28.7.2009 і. 11:35:46, error: Service Control Manager [7001] - The IPSEC Services service depends on the IPSEC driver service which failed to start because of the following error: A device attached to the system is not functioning. 28.7.2009 і. 11:35:46, error: Service Control Manager [7001] - The DNS Client service depends on the TCP/IP Protocol Driver service which failed to start because of the following error: A device attached to the system is not functioning. 28.7.2009 і. 11:35:46, error: Service Control Manager [7001] - The DHCP Client service depends on the NetBios over Tcpip service which failed to start because of the following error: A device attached to the system is not functioning. 28.7.2009 і. 11:35:02, error: DCOM [10005] - DCOM got error "%1084" attempting to start the service EventSystem with arguments "" in order to run the server: {1BE1F766-5536-11D1-B726-00C04FB926AF} 28.7.2009 і. 11:34:52, error: DCOM [10005] - DCOM got error "%1084" attempting to start the service netman with arguments "" in order to run the server: {BA126AE5-2166-11D1-B1D0-00805FC1270E} 28.7.2009 і. 10:30:30, error: Service Control Manager [7000] - The TuneUp Theme Extension service failed to start due to the following error: The executable program that this service is configured to run in does not implement the service. 28.7.2009 і. 10:24:50, error: Service Control Manager [7000] - The TuneUp Theme Extension service failed to start due to the following error: The executable program that this service is configured to run in does not implement the service. 24.7.2009 і. 12:41:45, error: Dhcp [1002] - The IP address lease 192.168.1.2 for the Network Card with network address 001E3338620C has been denied by the DHCP server 192.168.1.1 (The DHCP Server sent a DHCPNACK message). 24.7.2009 і. 08:18:58, error: Dhcp [1002] - The IP address lease 192.168.1.2 for the Network Card with network address 001E3338620C has been denied by the DHCP server 192.168.1.1 (The DHCP Server sent a DHCPNACK message). ==== End Of File ===========================
-
Здравейте, проблемът ми е следният: на една моя роднина pc с инсталиран аваст се оплаква за троянец, веднага след това започва да се издават звуци непрекъснато като те са серия от по 5 през 4 секунди. Сканирах го с аваста и нищо не намери, инсталирах eset smart system - и с него нищо не стана, преминах процедурите с malwarebytes, SUPERAntiSpyware, Dr Web и Combo Fix - нищо не стана, пищи си и това е. Доста търсих из нета, но не попаднах на никой с подобен проблем. Така попаднах на този невероятен форум, в който се надявам да намеря решение на моят проблем. Прилагам логовете на ComboFix и HiJackThis. ComboFix 09-07-29.03 - User 07.2009 г. 10:45.1.2 - NTFSx86 Microsoft Windows XP Professional 5.1.2600.2.1251.359.1033.18.2038.1315 [GMT 3:00] Running from: c:\downloads\ComboFix.exe AV: ESET Smart Security 3.0 *On-access scanning disabled* (Updated) {E5E70D32-0101-4F12-8FB0-D96ACA4F34C0} FW: ESET Personal firewall *enabled* {E5E70D32-0101-4340-86A3-A7B0F1C8FFE0} WARNING -THIS MACHINE DOES NOT HAVE THE RECOVERY CONSOLE INSTALLED !! . ((((((((((((((((((((((((((((((((((((((( Other Deletions ))))))))))))))))))))))))))))))))))))))))))))))))) . c:\program files\MyWebSearch . ((((((((((((((((((((((((((((((((((((((( Drivers/Services ))))))))))))))))))))))))))))))))))))))))))))))))) . -------\Legacy_MYWEBSEARCHSERVICE -------\Service_NPF ((((((((((((((((((((((((( Files Created from 2009-06-28 to 2009-07-30 ))))))))))))))))))))))))))))))) . 2009-07-30 07:43 . 2009-07-30 07:59 117760 ----a-w- c:\documents and settings\User\Application Data\SUPERAntiSpyware.com\SUPERAntiSpyware\SDDLLS\UIREPAIR.DLL 2009-07-30 07:40 . 2009-07-30 07:40 -------- d-----w- c:\documents and settings\All Users\Application Data\SUPERAntiSpyware.com 2009-07-30 07:39 . 2009-07-30 07:39 -------- d-----w- c:\program files\SUPERAntiSpyware 2009-07-30 07:39 . 2009-07-30 07:39 -------- d-----w- c:\documents and settings\User\Application Data\SUPERAntiSpyware.com 2009-07-30 07:39 . 2009-07-30 07:39 -------- d-----w- c:\program files\Common Files\Wise Installation Wizard 2009-07-30 07:32 . 2009-07-30 07:32 -------- d-----w- c:\documents and settings\User\DoctorWeb 2009-07-28 07:57 . 2009-07-28 07:57 -------- d-----w- c:\program files\Common Files\Adobe AIR 2009-07-28 07:43 . 2009-07-28 07:43 -------- d-----w- c:\documents and settings\User\Local Settings\Application Data\ESET 2009-07-28 07:30 . 2009-07-28 07:30 604416 ----a-w- c:\windows\system32\TUProgSt.exe 2009-07-28 07:30 . 2009-04-27 12:21 28928 ----a-w- c:\windows\system32\uxtuneup.dll 2009-07-28 07:30 . 2009-07-28 07:30 361216 ----a-w- c:\windows\system32\TuneUpDefragService.exe 2009-07-28 07:24 . 2009-07-28 07:24 -------- d-----w- c:\documents and settings\User\Application Data\TuneUp Software 2009-07-28 07:24 . 2009-07-28 07:24 -------- d-----w- c:\documents and settings\All Users\Application Data\TuneUp Software 2009-07-28 07:24 . 2009-07-28 07:30 -------- d-----w- c:\program files\TuneUp Utilities 2009 2009-07-28 07:22 . 2009-07-28 07:22 -------- d-----w- c:\program files\Enigma Software Group 2009-07-28 07:19 . 2009-07-28 07:19 -------- d-----w- c:\documents and settings\User\Application Data\ESET 2009-07-28 07:18 . 2009-07-28 07:18 -------- d-----w- c:\program files\ESET 2009-07-28 07:18 . 2009-07-28 07:18 -------- d-----w- c:\documents and settings\All Users\Application Data\ESET 2009-07-28 07:05 . 2009-07-28 07:05 -------- d-----w- c:\documents and settings\User\Application Data\Malwarebytes 2009-07-28 07:05 . 2009-07-13 10:36 38160 ----a-w- c:\windows\system32\drivers\mbamswissarmy.sys 2009-07-28 07:05 . 2009-07-28 07:05 -------- d-----w- c:\documents and settings\All Users\Application Data\Malwarebytes 2009-07-28 07:05 . 2009-07-13 10:36 19096 ----a-w- c:\windows\system32\drivers\mbam.sys 2009-07-28 07:05 . 2009-07-28 07:05 -------- d-----w- c:\program files\Malwarebytes' Anti-Malware . (((((((((((((((((((((((((((((((((((((((( Find3M Report )))))))))))))))))))))))))))))))))))))))))))))))))))) . 2009-07-30 07:40 . 2008-10-17 15:54 -------- d-----w- c:\program files\FlashGet 2009-07-28 07:55 . 2008-10-17 18:36 -------- d-----w- c:\program files\Common Files\Adobe 2009-07-26 19:24 . 2008-10-17 15:49 -------- d-----w- c:\documents and settings\User\Application Data\Skype 2009-07-26 13:04 . 2008-10-17 19:54 -------- d-----w- c:\documents and settings\User\Application Data\skypePM 2004-09-13 20:57 . 2004-09-13 20:57 94208 ----a-w- c:\program files\mozilla firefox\components\BrandRes.dll 2004-09-13 20:57 . 2004-09-13 20:57 150912 ----a-w- c:\program files\mozilla firefox\components\fullsoft.dll 2004-09-13 20:57 . 2004-09-13 20:57 53346 ----a-w- c:\program files\mozilla firefox\components\jar50.dll 2004-09-13 20:57 . 2004-09-13 20:57 61532 ----a-w- c:\program files\mozilla firefox\components\jsd3250.dll 2004-09-13 20:57 . 2004-09-13 20:57 24682 ----a-w- c:\program files\mozilla firefox\components\qfaservices.dll 2004-09-13 20:57 . 2004-09-13 20:57 172132 ----a-w- c:\program files\mozilla firefox\components\xpinstal.dll . ((((((((((((((((((((((((((((((((((((( Reg Loading Points )))))))))))))))))))))))))))))))))))))))))))))))))) . . *Note* empty entries & legit default entries are not shown REGEDIT4 [HKEY_CURRENT_USER\SOFTWARE\Microsoft\Windows\CurrentVersion\Run] "swg"="c:\program files\Google\GoogleToolbarNotifier\GoogleToolbarNotifier.exe" [2008-10-17 39408] "ctfmon.exe"="c:\windows\system32\ctfmon.exe" [2004-08-03 15360] "SUPERAntiSpyware"="c:\program files\SUPERAntiSpyware\SUPERAntiSpyware.exe" [2009-07-28 1830128] [HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\Run] "IgfxTray"="c:\windows\System32\igfxtray.exe" [2008-02-05 141848] "HotKeysCmds"="c:\windows\System32\hkcmd.exe" [2008-02-05 162328] "Persistence"="c:\windows\System32\igfxpers.exe" [2008-02-05 137752] "SynTPEnh"="c:\program files\Synaptics\SynTP\SynTPEnh.exe" [2007-12-06 1024000] "ACU"="c:\program files\Atheros\ACU.exe" [2008-01-26 450648] "BAE3FA"="c:\bonartmc\BonArt.exe" [2007-05-23 61440] "egui"="c:\program files\ESET\ESET Smart Security\egui.exe" [2008-07-01 1447168] "Adobe Reader Speed Launcher"="c:\program files\Adobe\Reader 9.0\Reader\Reader_sl.exe" [2008-06-11 34672] "RTHDCPL"="RTHDCPL.EXE" - c:\windows\RTHDCPL.exe [2008-01-29 16859648] c:\documents and settings\User\Start Menu\Programs\Startup\ abyssws.lnk - c:\bonartmc\abyssws.exe [2008-2-5 49636] c:\documents and settings\All Users\Start Menu\Programs\Startup\ FlexType 2K.lnk - c:\windows\Datecs\Flex2K.exe [2008-10-17 151552] [hkey_local_machine\software\microsoft\windows\currentversion\explorer\ShellExecuteHooks] "{5AE067D3-9AFB-48E0-853A-EBB7F4A000DA}"= "c:\program files\SUPERAntiSpyware\SASSEH.DLL" [2008-05-13 77824] [HKEY_LOCAL_MACHINE\software\microsoft\windows nt\currentversion\winlogon\notify\!SASWinLogon] 2008-12-22 09:05 356352 ----a-w- c:\program files\SUPERAntiSpyware\SASWINLO.dll [HKLM\~\services\sharedaccess\parameters\firewallpolicy\standardprofile] "EnableFirewall"= 0 (0x0) [HKLM\~\services\sharedaccess\parameters\firewallpolicy\standardprofile\AuthorizedApplications\List] "%windir%\\system32\\sessmgr.exe"= "c:\\Program Files\\FlashGet\\flashget.exe"= "c:\\WINDOWS\\system32\\LMabcoms.exe"= "c:\\Program Files\\Skype\\Phone\\Skype.exe"= R1 SASDIFSV;SASDIFSV;c:\program files\SUPERAntiSpyware\sasdifsv.sys [28.7.2009 і. 10:53 9968] R1 SASKUTIL;SASKUTIL;c:\program files\SUPERAntiSpyware\SASKUTIL.SYS [28.7.2009 і. 10:53 72944] R2 ekrn;Eset Service;c:\program files\ESET\ESET Smart Security\ekrn.exe [21.12.2007 і. 08:21 468224] R2 TuneUp.ProgramStatisticsSvc;TuneUp Program Statistics Service;c:\windows\system32\TUProgSt.exe [28.7.2009 і. 10:30 604416] R3 RTL8187B;Realtek RTL8187B Wireless 802.11b/g 54Mbps USB 2.0 Network Adapter;c:\windows\system32\drivers\RTL8187B.sys [17.10.2008 і. 18:44 288000] R3 SASENUM;SASENUM;c:\program files\SUPERAntiSpyware\SASENUM.SYS [28.7.2009 і. 10:53 7408] R3 WSIMD;wsimd Service;c:\windows\system32\drivers\wsimd.sys [17.10.2008 і. 18:32 57408] HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows NT\CurrentVersion\Svchost - NetSvcs UxTuneUp . Contents of the 'Scheduled Tasks' folder 2009-07-30 c:\windows\Tasks\1-Click Maintenance.job - c:\program files\TuneUp Utilities 2009\OneClickStarter.exe [2009-04-27 13:37] . . ------- Supplementary Scan ------- . uStart Page = about:blank uSearch Page = hxxp://www.google.com uSearch Bar = hxxp://www.google.com/ie mStart Page = about:blank uSearchURL,(Default) = hxxp://www.google.com/search?q=%s IE: &Download All with FlashGet - c:\program files\FlashGet\jc_all.htm IE: &Download with FlashGet - c:\program files\FlashGet\jc_link.htm DPF: DirectAnimation Java Classes - file://c:\windows\Java\classes\dajava.cab DPF: Microsoft XML Parser for Java - file://c:\windows\Java\classes\xmldso.cab FF - ProfilePath - c:\documents and settings\User\Application Data\Mozilla\Firefox\Profiles\p1i9jalj.default\ FF - prefs.js: browser.search.selectedEngine - Google FF - prefs.js: browser.startup.homepage - 127.0.0.1 FF - component: c:\program files\Mozilla Firefox\components\qfaservices.dll ---- FIREFOX POLICIES ---- c:\program files\Mozilla Firefox\greprefs\all.js - pref("backups.number_of_prefs_copies", 1); c:\program files\Mozilla Firefox\greprefs\all.js - pref("capability.policy.default.Window.closed", "allAccess"); c:\program files\Mozilla Firefox\greprefs\all.js - pref("capability.policy.default.Window.document", "allAccess"); c:\program files\Mozilla Firefox\greprefs\all.js - pref("capability.policy.default.Window.frames", "allAccess"); c:\program files\Mozilla Firefox\greprefs\all.js - pref("capability.policy.default.Window.history", "allAccess"); c:\program files\Mozilla Firefox\greprefs\all.js - pref("capability.policy.default.Window.length", "allAccess"); c:\program files\Mozilla Firefox\greprefs\all.js - pref("capability.policy.default.Window.opener", "allAccess"); c:\program files\Mozilla Firefox\greprefs\all.js - pref("capability.policy.default.Window.parent", "allAccess"); c:\program files\Mozilla Firefox\greprefs\all.js - pref("capability.policy.default.Window.self", "allAccess"); c:\program files\Mozilla Firefox\greprefs\all.js - pref("capability.policy.default.Window.top", "allAccess"); c:\program files\Mozilla Firefox\greprefs\all.js - pref("capability.policy.default.Window.window", "allAccess"); c:\program files\Mozilla Firefox\greprefs\all.js - pref("capability.policy.mailnews.DOMParser,parseFromString", "noAccess"); c:\program files\Mozilla Firefox\greprefs\all.js - pref("capability.policy.mailnews.DOMParser,parseFromStream", "noAccess"); c:\program files\Mozilla Firefox\greprefs\all.js - pref("browser.block.target_new_window", false); c:\program files\Mozilla Firefox\greprefs\all.js - pref("dom.disable_window_open_feature.status", false); c:\program files\Mozilla Firefox\greprefs\all.js - pref("advanced.always_load_images", true); c:\program files\Mozilla Firefox\greprefs\all.js - pref("network.protocol-handler.external.help", false); c:\program files\Mozilla Firefox\greprefs\all.js - pref("network.protocol-handler.external-default", 2); c:\program files\Mozilla Firefox\greprefs\all.js - pref("network.http.connect.timeout", 30); // in seconds c:\program files\Mozilla Firefox\greprefs\all.js - pref("network.http.request.timeout", 120); // in seconds c:\program files\Mozilla Firefox\greprefs\all.js - pref("network.image.imageBehavior", 0); // 0-Accept, 1-dontAcceptForeign, 2-dontUse c:\program files\Mozilla Firefox\greprefs\all.js - pref("network.cookie.cookieBehavior", 3); // 0-Accept, 1-dontAcceptForeign, 2-dontUse, 3-p3p c:\program files\Mozilla Firefox\greprefs\all.js - pref("network.cookie.p3plevel", 1); // 0=low, 1=medium, 2=high, 3=custom c:\program files\Mozilla Firefox\greprefs\all.js - pref("network.enablePad", false); // Allow client to do proxy autodiscovery c:\program files\Mozilla Firefox\greprefs\security-prefs.js - pref("security.warn_entering_weak", false); c:\program files\Mozilla Firefox\greprefs\security-prefs.js - pref("security.warn_viewing_mixed", false); c:\program files\Mozilla Firefox\defaults\pref\firefox.js - pref("app.id", "{ec8030f7-c20a-464f-9b0e-13a3a9e97384}"); c:\program files\Mozilla Firefox\defaults\pref\firefox.js - pref("app.version", c:\program files\Mozilla Firefox\defaults\pref\firefox.js - pref("app.extensions.version", "0.10"); c:\program files\Mozilla Firefox\defaults\pref\firefox.js - pref("app.build_id", c:\program files\Mozilla Firefox\defaults\pref\firefox.js - pref("app.update.autoUpdateEnabled", false); // Whether or not background app updates c:\program files\Mozilla Firefox\defaults\pref\firefox.js - pref("app.update.url", "chrome://mozapps/locale/update/update.properties"); c:\program files\Mozilla Firefox\defaults\pref\firefox.js - pref("app.update.updatesAvailable", false); c:\program files\Mozilla Firefox\defaults\pref\firefox.js - pref("app.update.lastUpdateDate", 0); // UTC offset when last App update was c:\program files\Mozilla Firefox\defaults\pref\firefox.js - pref("app.update.performed", false); // Whether or not an update has been c:\program files\Mozilla Firefox\defaults\pref\firefox.js - pref("extensions.update.autoUpdateEnabled", false); c:\program files\Mozilla Firefox\defaults\pref\firefox.js - pref("extensions.update.autoUpdate", false); // Automatically download and install c:\program files\Mozilla Firefox\defaults\pref\firefox.js - pref("extensions.update.interval", 604800000); // Check for updates to Extensions and c:\program files\Mozilla Firefox\defaults\pref\firefox.js - pref("extensions.update.lastUpdateDate", 0); // UTC offset when last Extension/Theme c:\program files\Mozilla Firefox\defaults\pref\firefox.js - pref("extensions.update.severity.threshold", 5);// The number of pending Extension/Theme c:\program files\Mozilla Firefox\defaults\pref\firefox.js - pref("extensions.update.count", 0); // The number of extension/theme/etc c:\program files\Mozilla Firefox\defaults\pref\firefox.js - pref("update.interval", 3600000); // Check each of the above intervals c:\program files\Mozilla Firefox\defaults\pref\firefox.js - pref("update.showSlidingNotification", true); // Windows-only slide-up taskbar c:\program files\Mozilla Firefox\defaults\pref\firefox.js - pref("update.severity", 0); c:\program files\Mozilla Firefox\defaults\pref\firefox.js - pref("general.useragent.vendor", "Firefox"); c:\program files\Mozilla Firefox\defaults\pref\firefox.js - pref("general.useragent.vendorSub", "0.10"); c:\program files\Mozilla Firefox\defaults\pref\firefox.js - pref("browser.startup.homepage", "http://127.0.0.1/"); c:\program files\Mozilla Firefox\defaults\pref\firefox.js - pref("browser.startup.homepage_override.1", false); c:\program files\Mozilla Firefox\defaults\pref\firefox.js - pref("browser.turbo.enabled", false); c:\program files\Mozilla Firefox\defaults\pref\firefox.js - pref("browser.search.param.Google.1.name", "chrome://browser/content/searchconfig.properties"); c:\program files\Mozilla Firefox\defaults\pref\firefox.js - pref("browser.search.param.Google.1.custom", "chrome://browser/content/searchconfig.properties"); c:\program files\Mozilla Firefox\defaults\pref\firefox.js - pref("browser.search.param.Google.1.default", "chrome://browser/content/searchconfig.properties"); c:\program files\Mozilla Firefox\defaults\pref\firefox.js - pref("dom.disable_open_during_load", false); c:\program files\Mozilla Firefox\defaults\pref\firefox.js - pref("network.protocols.useSystemDefaults", false); // set to true if user links should use system default handlers c:\program files\Mozilla Firefox\defaults\pref\firefox.js - pref("update_notifications.enabled", true); c:\program files\Mozilla Firefox\defaults\pref\firefox.js - pref("update_notifications.provider.0.frequency", 7); // number of days c:\program files\Mozilla Firefox\defaults\pref\firefox.js - pref("browser.xul.error_pages.enabled", false); c:\program files\Mozilla Firefox\defaults\pref\firefox.js - pref("network.protocol-handler.external.news" , true); // for news c:\program files\Mozilla Firefox\defaults\pref\firefox.js - pref("security.warn_entering_weak.show_once", false); c:\program files\Mozilla Firefox\defaults\pref\firefox.js - pref("security.warn_viewing_mixed.show_once", false); c:\program files\Mozilla Firefox\defaults\pref\firefox.js - pref("pfs.datasource.url", "chrome://mozapps/locale/plugins/plugins.properties"); . ************************************************************************** catchme 0.3.1398 W2K/XP/Vista - rootkit/stealth malware detector by Gmer, http://www.gmer.net Rootkit scan 2009-07-30 10:59 Windows 5.1.2600 Service Pack 2 NTFS scanning hidden processes ... scanning hidden autostart entries ... scanning hidden files ... scan completed successfully hidden files: 0 ************************************************************************** [HKEY_LOCAL_MACHINE\System\ControlSet001\Services\MySql] "ImagePath"="C:/BonArtMC/database/bin/mysqld-nt.exe" [HKEY_LOCAL_MACHINE\System\ControlSet001\Services\MySql] "ImagePath"="C:/BonArtMC/database/bin/mysqld-nt.exe" . --------------------- DLLs Loaded Under Running Processes --------------------- - - - - - - - > 'winlogon.exe'(1464) c:\program files\SUPERAntiSpyware\SASWINLO.dll - - - - - - - > 'explorer.exe'(2328) c:\windows\system32\newdll.dll . ------------------------ Other Running Processes ------------------------ . c:\windows\system32\acs.exe c:\bonartmc\database\bin\mysqld-nt.exe c:\windows\system32\wdfmgr.exe c:\windows\system32\igfxsrvc.exe . ************************************************************************** . Completion time: 2009-07-30 11:02 - machine was rebooted ComboFix-quarantined-files.txt 2009-07-30 08:02 Pre-Run: 83 001 024 512 bytes free Post-Run: 89 478 692 864 bytes free 215 ---------------------------------------------------------------------------------------------------------------------------- Logfile of Trend Micro HijackThis v2.0.2 Scan saved at 11:03:52, on 30.7.2009 г. Platform: Windows XP SP2 (WinNT 5.01.2600) MSIE: Internet Explorer v6.00 SP2 (6.00.2900.2180) Boot mode: Normal Running processes: C:\WINDOWS\System32\smss.exe C:\WINDOWS\system32\winlogon.exe C:\WINDOWS\system32\services.exe C:\WINDOWS\system32\lsass.exe C:\WINDOWS\system32\svchost.exe C:\WINDOWS\System32\svchost.exe C:\WINDOWS\system32\spoolsv.exe C:\WINDOWS\System32\acs.exe C:\Program Files\ESET\ESET Smart Security\ekrn.exe C:\BonArtMC\database\bin\mysqld-nt.exe C:\WINDOWS\System32\svchost.exe C:\WINDOWS\System32\TUProgSt.exe C:\WINDOWS\RTHDCPL.EXE C:\WINDOWS\System32\igfxtray.exe C:\WINDOWS\System32\hkcmd.exe C:\WINDOWS\System32\igfxpers.exe C:\Program Files\Synaptics\SynTP\SynTPEnh.exe C:\WINDOWS\System32\igfxsrvc.exe C:\BonArtMC\BonArt.exe C:\Program Files\ESET\ESET Smart Security\egui.exe C:\Program Files\Adobe\Reader 9.0\Reader\Reader_sl.exe C:\Program Files\Google\GoogleToolbarNotifier\GoogleToolbarNotifier.exe C:\WINDOWS\system32\ctfmon.exe C:\WINDOWS\Datecs\Flex2K.exe C:\WINDOWS\system32\wuauclt.exe C:\WINDOWS\explorer.exe C:\Program Files\SUPERAntiSpyware\SUPERAntiSpyware.exe D:\install\антивир\HiJackThis.exe C:\BonArtMC\php\php.exe R0 - HKCU\Software\Microsoft\Internet Explorer\Main,Start Page = about:blank R1 - HKLM\Software\Microsoft\Internet Explorer\Main,Default_Page_URL = http://go.microsoft.com/fwlink/?LinkId=69157 R1 - HKLM\Software\Microsoft\Internet Explorer\Main,Default_Search_URL = http://go.microsoft.com/fwlink/?LinkId=54896 R1 - HKLM\Software\Microsoft\Internet Explorer\Main,Search Page = http://go.microsoft.com/fwlink/?LinkId=54896 R0 - HKLM\Software\Microsoft\Internet Explorer\Main,Start Page = about:blank O2 - BHO: Adobe PDF Link Helper - {18DF081C-E8AD-4283-A596-FA578C2EBDC3} - C:\Program Files\Common Files\Adobe\Acrobat\ActiveX\AcroIEHelperShim.dll O2 - BHO: Skype add-on (mastermind) - {22BF413B-C6D2-4d91-82A9-A0F997BA588C} - C:\Program Files\Skype\Toolbars\Internet Explorer\SkypeIEPlugin.dll O2 - BHO: flashget urlcatch - {2F364306-AA45-47B5-9F9D-39A8B94E7EF7} - C:\Program Files\FlashGet\jccatch.dll O2 - BHO: WormRadar.com IESiteBlocker.NavFilter - {3CA2F312-6F6E-4B53-A66E-4E65E497C8C0} - (no file) O2 - BHO: Google Toolbar Helper - {AA58ED58-01DD-4d91-8333-CF10577473F7} - C:\Program Files\Google\Google Toolbar\GoogleToolbar.dll O2 - BHO: Google Toolbar Notifier BHO - {AF69DE43-7D58-4638-B6FA-CE66B5AD205D} - C:\Program Files\Google\GoogleToolbarNotifier\5.1.1309.15642\swg.dll O2 - BHO: Google Dictionary Compression sdch - {C84D72FE-E17D-4195-BB24-76C02E2E7C4E} - C:\Program Files\Google\Google Toolbar\Component\fastsearch_A8904FB862BD9564.dll O2 - BHO: FlashGet GetFlash Class - {F156768E-81EF-470C-9057-481BA8380DBA} - C:\Program Files\FlashGet\getflash.dll O3 - Toolbar: Google Toolbar - {2318C2B1-4965-11d4-9B18-009027A5CD4F} - C:\Program Files\Google\Google Toolbar\GoogleToolbar.dll O4 - HKLM\..\Run: [RTHDCPL] RTHDCPL.EXE O4 - HKLM\..\Run: [igfxTray] C:\WINDOWS\System32\igfxtray.exe O4 - HKLM\..\Run: [HotKeysCmds] C:\WINDOWS\System32\hkcmd.exe O4 - HKLM\..\Run: [Persistence] C:\WINDOWS\System32\igfxpers.exe O4 - HKLM\..\Run: [synTPEnh] C:\Program Files\Synaptics\SynTP\SynTPEnh.exe O4 - HKLM\..\Run: [ACU] "C:\Program Files\Atheros\ACU.exe" -nogui O4 - HKLM\..\Run: [bAE3FA] C:\BonArtMC\BonArt.exe O4 - HKLM\..\Run: [egui] "C:\Program Files\ESET\ESET Smart Security\egui.exe" /hide /waitservice O4 - HKLM\..\Run: [Adobe Reader Speed Launcher] "C:\Program Files\Adobe\Reader 9.0\Reader\Reader_sl.exe" O4 - HKCU\..\Run: [swg] C:\Program Files\Google\GoogleToolbarNotifier\GoogleToolbarNotifier.exe O4 - HKCU\..\Run: [ctfmon.exe] C:\WINDOWS\system32\ctfmon.exe O4 - HKCU\..\Run: [sUPERAntiSpyware] C:\Program Files\SUPERAntiSpyware\SUPERAntiSpyware.exe O4 - Startup: abyssws.lnk = C:\BonArtMC\abyssws.exe O4 - Global Startup: FlexType 2K.lnk = ? O8 - Extra context menu item: &Download All with FlashGet - C:\Program Files\FlashGet\jc_all.htm O8 - Extra context menu item: &Download with FlashGet - C:\Program Files\FlashGet\jc_link.htm O18 - Protocol: skype4com - {FFC8B962-9B40-4DFF-9458-1830C7DD7F5D} - C:\PROGRA~1\COMMON~1\Skype\SKYPE4~1.DLL O18 - Filter: x-sdch - {B1759355-3EEC-4C1E-B0F1-B719FE26E377} - C:\Program Files\Google\Google Toolbar\Component\fastsearch_A8904FB862BD9564.dll O20 - Winlogon Notify: !SASWinLogon - C:\Program Files\SUPERAntiSpyware\SASWINLO.dll O23 - Service: Atheros Configuration Service (ACS) - Atheros - C:\WINDOWS\System32\acs.exe O23 - Service: Adobe LM Service - Adobe Systems - C:\Program Files\Common Files\Adobe Systems Shared\Service\Adobelmsvc.exe O23 - Service: Eset HTTP Server (EhttpSrv) - ESET - C:\Program Files\ESET\ESET Smart Security\EHttpSrv.exe O23 - Service: Eset Service (ekrn) - ESET - C:\Program Files\ESET\ESET Smart Security\ekrn.exe O23 - Service: Google Software Updater (gusvc) - Google - C:\Program Files\Google\Common\Google Updater\GoogleUpdaterService.exe O23 - Service: lmab_device - Unknown owner - C:\WINDOWS\system32\LMabcoms.exe O23 - Service: MySql - Unknown owner - C:/BonArtMC/database/bin/mysqld-nt.exe O23 - Service: TuneUp Drive Defrag Service (TuneUp.Defrag) - TuneUp Software - C:\WINDOWS\System32\TuneUpDefragService.exe O23 - Service: TuneUp Program Statistics Service (TuneUp.ProgramStatisticsSvc) - TuneUp Software - C:\WINDOWS\System32\TUProgSt.exe -- End of file - 5508 bytes Предварително благодаря на всички за съветите.
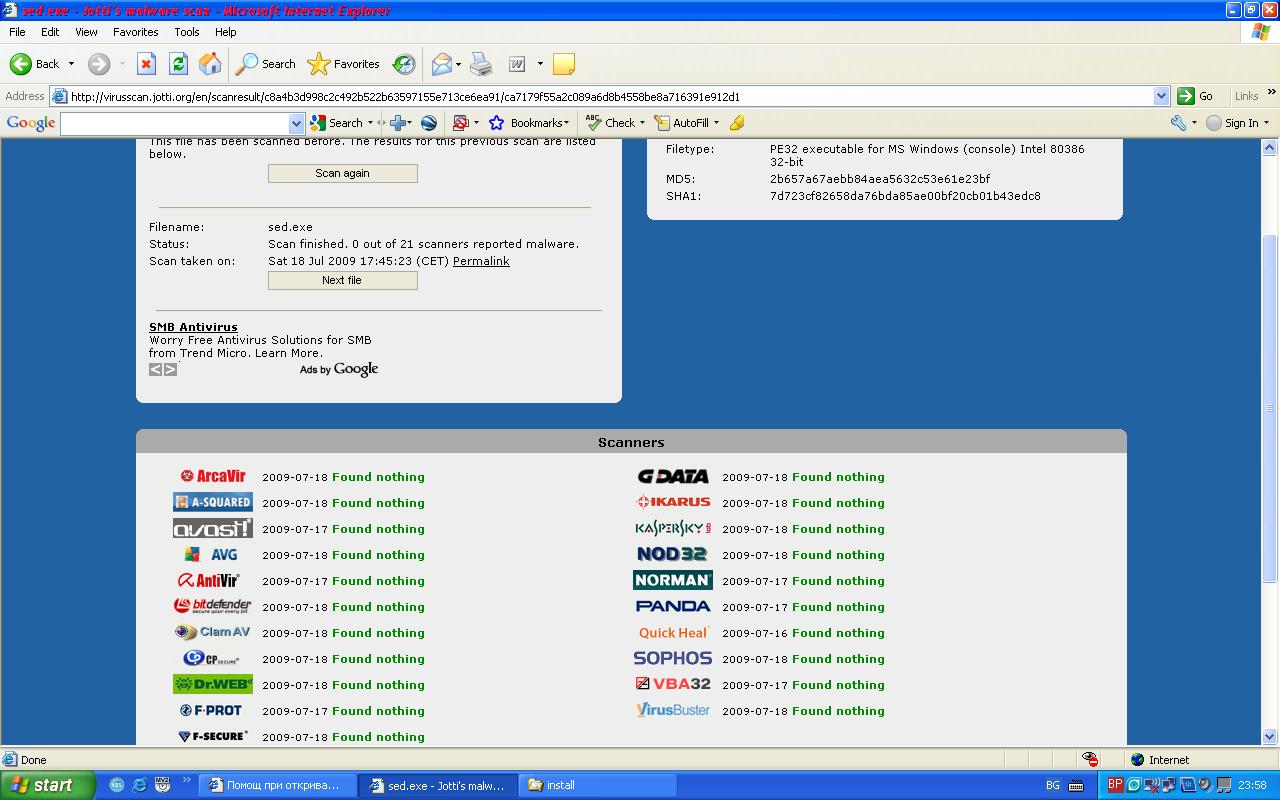
Разглеждащи това в момента 0
- Няма регистрирани потребители разглеждащи тази страница.