


morjini_f
Потребител
-
Регистрация
-
Последно онлайн
Всичко публикувано от morjini_f
-
Иначе до тук изпълних всичко мо та мо, както се казва. Вече съм с Авира
-
Стигам само до C:\Program Files\. Нататък нямам път до тези папки и деинсталатор. Май нямам HiJackThis? И друг въпрос: Когато стартирам Varija2K.inf за продължаване на работата, имам следния прозорец: Нямам такъв диск. Какво да направя?
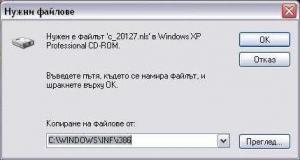
-
Тъкмо щях да поискам работещ линк Почти изтрих вече всичко, което е написано да се изтрие, приех го като писан закон Ще пиша като приключа с всичко. Как да деинсталирам HijackThis 2.0.2? Няма го в контролния панел, добавяне или премахване на програми, както и в менютата на Старт меню.
-
Това е лога от OTL: ========== OTL ========== Registry value HKEY_USERS\S-1-5-21-1957994488-1275210071-1177238915-500\Software\Microsoft\Internet Explorer\URLSearchHooks\\{472734EA-242A-422b-ADF8-83D1E48CC825} not found. Registry key HKEY_LOCAL_MACHINE\SOFTWARE\Classes\CLSID\{472734EA-242A-422b-ADF8-83D1E48CC825}\ not found. Prefs.js: {E9A1DEE0-C623-4439-8932-001E7D17607D}:2.1.0.5 removed from extensions.enabledItems Prefs.js: {4CFC8387-5FB1-47C1-8AA4-5B7B906A591E}:1.0 removed from extensions.enabledItems Prefs.js: {414b6d9d-4a95-4e8d-b5b1-149dd2d93bb3}:2.7.1.3 removed from extensions.enabledItems Prefs.js: "Secure Search" removed from browser.search.defaultenginename Prefs.js: "Softonic-Eng7 Customized Web Search" removed from browser.search.defaultthis.engineName Folder C:\Documents and Settings\Administrator\Application Data\Mozilla\Firefox\Profiles\korvvd8g.default\extensions\{414b6d9d-4a95-4e8d-b5b1-149dd2d93bb3}\ not found. Folder C:\Documents and Settings\Administrator\Application Data\Mozilla\Firefox\Profiles\korvvd8g.default\extensions\{E9A1DEE0-C623-4439-8932-001E7D17607D}\ not found. Folder C:\Documents and Settings\Administrator\Application Data\Mozilla\Firefox\Profiles\korvvd8g.default\extensions\[email protected]\ not found. File C:\Documents and Settings\Administrator\Application Data\Mozilla\Firefox\Profiles\korvvd8g.default\searchplugins\ask.xml not found. File C:\Documents and Settings\Administrator\Application Data\Mozilla\Firefox\Profiles\korvvd8g.default\searchplugins\conduit.xml not found. File C:\Program Files\Mozilla Firefox\searchplugins\wyeke127.xml not found. File C:\Program Files\Mozilla Firefox\searchplugins\wyeke129.xml not found. File C:\Program Files\Mozilla Firefox\searchplugins\wyeke131.xml not found. File C:\Program Files\Mozilla Firefox\searchplugins\wyeke133.xml not found. File C:\Program Files\Mozilla Firefox\searchplugins\wyeke137.xml not found. Starting removal of ActiveX control {31435657-9980-0010-8000-00AA00389B71} Registry key HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Code Store Database\Distribution Units\{31435657-9980-0010-8000-00AA00389B71}\ not found. Registry key HKEY_LOCAL_MACHINE\SOFTWARE\Classes\CLSID\{31435657-9980-0010-8000-00AA00389B71}\ not found. Registry key HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Active Setup\Installed Components\{31435657-9980-0010-8000-00AA00389B71}\ not found. Registry key HKEY_LOCAL_MACHINE\SOFTWARE\Classes\CLSID\{31435657-9980-0010-8000-00AA00389B71}\ not found. File oft XML Parser for Java file://C:\WINDOWS\Java\classes\xmldso.cab not found. Starting removal of ActiveX control Microsoft XML Parser for Java Registry key HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Code Store Database\Distribution Units\Microsoft XML Parser for Java\ not found. Registry key HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Active Setup\Installed Components\Microsoft XML Parser for Java\ not found. File C:\Documents and Settings\Administrator\Desktop\Active Desktop Recovery.zip not found. Unable to delete ADS C:\Documents and Settings\All Users\Application Data\TEMP:DFC5A2B2 . Unable to delete ADS C:\Documents and Settings\All Users\Application Data\TEMP:66871744 . Unable to delete ADS C:\Documents and Settings\All Users\Application Data\TEMP:178D4338 . Unable to delete ADS C:\Documents and Settings\All Users\Application Data\TEMP:3D36932D . ========== FILES ========== < ipconfig /flushdns /c > Windows IP Configuration Successfully flushed the DNS Resolver Cache. C:\Documents and Settings\Administrator\Desktop\cmd.bat deleted successfully. C:\Documents and Settings\Administrator\Desktop\cmd.txt deleted successfully. ========== COMMANDS ========== OTL by OldTimer - Version 3.2.22.3 log created on 04152011_190446 Имах проблеми с лога на GooredFix, но след няколкократно стартиране и спиране, явно съм надвила над програмата и си показа лога Ето го и него: GooredFix by jpshortstuff (03.07.10.1) Log created at 19:55 on 15/04/2011 (Administrator) Firefox version 4.0 (bg) ========== GooredScan ========== ========== GooredLog ========== C:\Program Files\Mozilla Firefox\extensions\ {972ce4c6-7e08-4474-a285-3208198ce6fd} [17:14 03/04/2011] {CAFEEFAC-0016-0000-0011-ABCDEFFEDCBA} [00:08 24/12/2008] {CAFEEFAC-0016-0000-0014-ABCDEFFEDCBA} [14:51 29/08/2009] {CAFEEFAC-0016-0000-0015-ABCDEFFEDCBA} [12:17 30/08/2009] {CAFEEFAC-0016-0000-0020-ABCDEFFEDCBA} [22:35 02/05/2010] {CAFEEFAC-0016-0000-0021-ABCDEFFEDCBA} [12:17 28/09/2010] C:\Documents and Settings\Administrator\Application Data\Mozilla\Firefox\Profiles\korvvd8g.default\extensions\ [email protected] [04:09 14/11/2009] [email protected] [21:44 09/07/2009] [email protected] [21:40 09/07/2009] [email protected] [17:16 03/04/2011] {04CA07AB-7FC3-4110-A83F-EF1E6B75D5B0} [07:36 01/08/2009] {20a82645-c095-46ed-80e3-08825760534b} [09:47 03/09/2009] {66871bd1-5ba2-4739-b485-2a15f5969bd8} [11:16 18/04/2010] {a02c0c70-605c-11da-8cd6-0800200c9a66} [11:16 18/04/2010] {d4385b60-11f0-11de-8c30-0800200c9a66} [21:35 09/07/2009] [HKEY_LOCAL_MACHINE\Software\Mozilla\Firefox\Extensions] "{20a82645-c095-46ed-80e3-08825760534b}"="C:\WINDOWS\Microsoft.NET\Framework\v3.5\Windows Presentation Foundation\DotNetAssistantExtension\" [00:07 15/08/2009] "[email protected]"="C:\Program Files\Java\jre6\lib\deploy\jqs\ff" [14:51 29/08/2009] "{B7082FAA-CB62-4872-9106-E42DD88EDE45}"="C:\Program Files\McAfee\SiteAdvisor" [12:58 05/01/2011] -=E.O.F=- След повече от 2 часа сканиране, ето лог и от Есет : ESETSmartInstaller@High as downloader log: all ok # version=7 # OnlineScannerApp.exe=1.0.0.1 # OnlineScanner.ocx=1.0.0.6427 # api_version=3.0.2 # EOSSerial=abcd3a914de1b94f82e4f112970de828 # end=finished # remove_checked=false # archives_checked=true # unwanted_checked=true # unsafe_checked=true # antistealth_checked=true # utc_time=2011-04-15 07:19:08 # local_time=2011-04-15 10:19:08 (+0200, FLE Daylight Time) # country="Bulgaria" # lang=1033 # osver=5.1.2600 NT Service Pack 3 # compatibility_mode=512 16777215 100 0 0 0 0 0 # compatibility_mode=2560 16777215 100 0 0 0 0 0 # compatibility_mode=8192 67108863 100 0 364 364 0 0 # scanned=138970 # found=0 # cleaned=0 # scan_time=8048
-
След reboot-а OTL не продължава работа и не излиза лог. Какво да направя?
-
Здравей, B-boy[styLe], Ето двата лога от OTL: OTL.Txt Extras.Txt и този от RkU: Report.txt Какво се случва до момента?
-
Ето лога: ComboFix 11-04-14.01 - Administrator 04.2011 г. 10:10:40.6.2 - x86 Microsoft Windows XP Professional 5.1.2600.3.1251.359.1033.18.1789.882 [GMT 3:00] Running from: c:\documents and settings\Administrator\Desktop\ComboFix.exe Command switches used :: c:\documents and settings\Administrator\Desktop\CFScript.txt . FILE :: "c:\program files\Softonic-Eng7\prxtbSof2.dll" "c:\windows\system32\ConduitEngine.tmp" . . ((((((((((((((((((((((((((((((((((((((( Other Deletions ))))))))))))))))))))))))))))))))))))))))))))))))) . . c:\documents and settings\Administrator\Application Data\PriceGong c:\documents and settings\Administrator\Application Data\PriceGong\Data\1.xml c:\documents and settings\Administrator\Application Data\PriceGong\Data\a.xml c:\documents and settings\Administrator\Application Data\PriceGong\Data\b.xml c:\documents and settings\Administrator\Application Data\PriceGong\Data\c.xml c:\documents and settings\Administrator\Application Data\PriceGong\Data\d.xml c:\documents and settings\Administrator\Application Data\PriceGong\Data\e.xml c:\documents and settings\Administrator\Application Data\PriceGong\Data\f.xml c:\documents and settings\Administrator\Application Data\PriceGong\Data\g.xml c:\documents and settings\Administrator\Application Data\PriceGong\Data\h.xml c:\documents and settings\Administrator\Application Data\PriceGong\Data\i.xml c:\documents and settings\Administrator\Application Data\PriceGong\Data\J.xml c:\documents and settings\Administrator\Application Data\PriceGong\Data\k.xml c:\documents and settings\Administrator\Application Data\PriceGong\Data\l.xml c:\documents and settings\Administrator\Application Data\PriceGong\Data\m.xml c:\documents and settings\Administrator\Application Data\PriceGong\Data\mru.xml c:\documents and settings\Administrator\Application Data\PriceGong\Data\n.xml c:\documents and settings\Administrator\Application Data\PriceGong\Data\o.xml c:\documents and settings\Administrator\Application Data\PriceGong\Data\p.xml c:\documents and settings\Administrator\Application Data\PriceGong\Data\q.xml c:\documents and settings\Administrator\Application Data\PriceGong\Data\r.xml c:\documents and settings\Administrator\Application Data\PriceGong\Data\s.xml c:\documents and settings\Administrator\Application Data\PriceGong\Data\t.xml c:\documents and settings\Administrator\Application Data\PriceGong\Data\u.xml c:\documents and settings\Administrator\Application Data\PriceGong\Data\v.xml c:\documents and settings\Administrator\Application Data\PriceGong\Data\w.xml c:\documents and settings\Administrator\Application Data\PriceGong\Data\x.xml c:\documents and settings\Administrator\Application Data\PriceGong\Data\y.xml c:\documents and settings\Administrator\Application Data\PriceGong\Data\z.xml c:\documents and settings\Administrator\Desktop\С°Ѕтр° c:\documents and settings\Administrator\Local Settings\Application Data\ConduitEngine c:\documents and settings\Administrator\Local Settings\Application Data\ConduitEngine\CacheIcons\http___storage_conduit_com_32_243_CT2431232_Images_634120316644468750_gif.gif c:\documents and settings\Administrator\Local Settings\Application Data\ConduitEngine\CacheIcons\http___storage_conduit_com_80_240_CT2405280_Images_634382234588362500_gif.gif c:\documents and settings\Administrator\Local Settings\Application Data\ConduitEngine\CacheIcons\http___storage_Conduit_com_bankImages_ConduitEngine_ContextMenu_About_png.png c:\documents and settings\Administrator\Local Settings\Application Data\ConduitEngine\CacheIcons\http___storage_Conduit_com_bankImages_ConduitEngine_ContextMenu_Browse_png.png c:\documents and settings\Administrator\Local Settings\Application Data\ConduitEngine\CacheIcons\http___storage_Conduit_com_bankImages_ConduitEngine_ContextMenu_Contact_png.png c:\documents and settings\Administrator\Local Settings\Application Data\ConduitEngine\CacheIcons\http___storage_Conduit_com_bankImages_ConduitEngine_ContextMenu_Hide_png.png c:\documents and settings\Administrator\Local Settings\Application Data\ConduitEngine\CacheIcons\http___storage_Conduit_com_bankImages_ConduitEngine_ContextMenu_LikeIcon_png.png c:\documents and settings\Administrator\Local Settings\Application Data\ConduitEngine\CacheIcons\http___storage_Conduit_com_bankImages_ConduitEngine_ContextMenu_More_png.png c:\documents and settings\Administrator\Local Settings\Application Data\ConduitEngine\CacheIcons\http___storage_Conduit_com_bankImages_ConduitEngine_ContextMenu_MoreFromPublisher_png.png c:\documents and settings\Administrator\Local Settings\Application Data\ConduitEngine\CacheIcons\http___storage_Conduit_com_bankImages_ConduitEngine_ContextMenu_MoveLeft_png.png c:\documents and settings\Administrator\Local Settings\Application Data\ConduitEngine\CacheIcons\http___storage_Conduit_com_bankImages_ConduitEngine_ContextMenu_MoveRight_png.png c:\documents and settings\Administrator\Local Settings\Application Data\ConduitEngine\CacheIcons\http___storage_Conduit_com_bankImages_ConduitEngine_ContextMenu_Options_png.png c:\documents and settings\Administrator\Local Settings\Application Data\ConduitEngine\CacheIcons\http___storage_Conduit_com_bankImages_ConduitEngine_ContextMenu_Privacy_png.png c:\documents and settings\Administrator\Local Settings\Application Data\ConduitEngine\CacheIcons\http___storage_Conduit_com_bankImages_ConduitEngine_ContextMenu_Refresh_png.png c:\documents and settings\Administrator\Local Settings\Application Data\ConduitEngine\CacheIcons\http___storage_Conduit_com_bankImages_ConduitEngine_ContextMenu_Upgrade_png.png c:\documents and settings\Administrator\Local Settings\Application Data\ConduitEngine\ConduitEngine.dll c:\documents and settings\Administrator\Local Settings\Application Data\ConduitEngine\Dialogs\AddedAppDialog\app-added.js c:\documents and settings\Administrator\Local Settings\Application Data\ConduitEngine\Dialogs\AddedAppDialog\main.html c:\documents and settings\Administrator\Local Settings\Application Data\ConduitEngine\Dialogs\DefualtImages\icon.png c:\documents and settings\Administrator\Local Settings\Application Data\ConduitEngine\Dialogs\DetectedAppDialog\app-2go.js c:\documents and settings\Administrator\Local Settings\Application Data\ConduitEngine\Dialogs\DetectedAppDialog\main.html c:\documents and settings\Administrator\Local Settings\Application Data\ConduitEngine\Dialogs\DialogsAPI.js c:\documents and settings\Administrator\Local Settings\Application Data\ConduitEngine\Dialogs\EngineFirstTimeDialog\EngineFirstTimeDialog.js c:\documents and settings\Administrator\Local Settings\Application Data\ConduitEngine\Dialogs\EngineFirstTimeDialog\main.html c:\documents and settings\Administrator\Local Settings\Application Data\ConduitEngine\Dialogs\EngineFirstTimeDialog\right-click.gif c:\documents and settings\Administrator\Local Settings\Application Data\ConduitEngine\Dialogs\excanvas.js c:\documents and settings\Administrator\Local Settings\Application Data\ConduitEngine\Dialogs\generalDialogStyle.css c:\documents and settings\Administrator\Local Settings\Application Data\ConduitEngine\Dialogs\PIE.htc c:\documents and settings\Administrator\Local Settings\Application Data\ConduitEngine\Dialogs\RoundedCorners.css c:\documents and settings\Administrator\Local Settings\Application Data\ConduitEngine\Dialogs\RoundedCornersIE9.css c:\documents and settings\Administrator\Local Settings\Application Data\ConduitEngine\Dialogs\SearchProtectorDialog\Images\info.png c:\documents and settings\Administrator\Local Settings\Application Data\ConduitEngine\Dialogs\SearchProtectorDialog\Images\ok-on.png c:\documents and settings\Administrator\Local Settings\Application Data\ConduitEngine\Dialogs\SearchProtectorDialog\Images\ok.png c:\documents and settings\Administrator\Local Settings\Application Data\ConduitEngine\Dialogs\SearchProtectorDialog\main.html c:\documents and settings\Administrator\Local Settings\Application Data\ConduitEngine\Dialogs\SearchProtectorDialog\SearchProtector.css c:\documents and settings\Administrator\Local Settings\Application Data\ConduitEngine\Dialogs\SearchProtectorDialog\SearchProtector.js c:\documents and settings\Administrator\Local Settings\Application Data\ConduitEngine\Dialogs\settings.js c:\documents and settings\Administrator\Local Settings\Application Data\ConduitEngine\Dialogs\ToolbarFirstTimeDialog\images\app-store-icon.png c:\documents and settings\Administrator\Local Settings\Application Data\ConduitEngine\Dialogs\ToolbarFirstTimeDialog\images\arrow.png c:\documents and settings\Administrator\Local Settings\Application Data\ConduitEngine\Dialogs\ToolbarFirstTimeDialog\images\divider.png c:\documents and settings\Administrator\Local Settings\Application Data\ConduitEngine\Dialogs\ToolbarFirstTimeDialog\images\emailNotifier.gif c:\documents and settings\Administrator\Local Settings\Application Data\ConduitEngine\Dialogs\ToolbarFirstTimeDialog\images\facebook.png c:\documents and settings\Administrator\Local Settings\Application Data\ConduitEngine\Dialogs\ToolbarFirstTimeDialog\images\radio.GIF c:\documents and settings\Administrator\Local Settings\Application Data\ConduitEngine\Dialogs\ToolbarFirstTimeDialog\images\Thumbs.db c:\documents and settings\Administrator\Local Settings\Application Data\ConduitEngine\Dialogs\ToolbarFirstTimeDialog\images\truste_welcome.GIF c:\documents and settings\Administrator\Local Settings\Application Data\ConduitEngine\Dialogs\ToolbarFirstTimeDialog\images\weather.GIF c:\documents and settings\Administrator\Local Settings\Application Data\ConduitEngine\Dialogs\ToolbarFirstTimeDialog\main.html c:\documents and settings\Administrator\Local Settings\Application Data\ConduitEngine\Dialogs\ToolbarFirstTimeDialog\ToolbarFirstTimeDialog.css c:\documents and settings\Administrator\Local Settings\Application Data\ConduitEngine\Dialogs\ToolbarFirstTimeDialog\ToolbarFirstTimeDialog.js c:\documents and settings\Administrator\Local Settings\Application Data\ConduitEngine\Dialogs\ToolbarUntrustedAppsApprovalDialog\main.html c:\documents and settings\Administrator\Local Settings\Application Data\ConduitEngine\Dialogs\ToolbarUntrustedAppsApprovalDialog\ToolbarUntrustedAppsApprovalDialog.js c:\documents and settings\Administrator\Local Settings\Application Data\ConduitEngine\Dialogs\UntrustedAddedAppDialog\main.html c:\documents and settings\Administrator\Local Settings\Application Data\ConduitEngine\Dialogs\UntrustedAddedAppDialog\UT-app-dialog-added.js c:\documents and settings\Administrator\Local Settings\Application Data\ConduitEngine\Dialogs\UntrustedAppApprovalDialog\main.html c:\documents and settings\Administrator\Local Settings\Application Data\ConduitEngine\Dialogs\UntrustedAppApprovalDialog\UT-app-dialog-needs-your-approval.js c:\documents and settings\Administrator\Local Settings\Application Data\ConduitEngine\Dialogs\UntrustedAppPendingDialog\main.html c:\documents and settings\Administrator\Local Settings\Application Data\ConduitEngine\Dialogs\UntrustedAppPendingDialog\UT-app-dialog-is-waiting.js c:\documents and settings\Administrator\Local Settings\Application Data\ConduitEngine\Dialogs\version.txt c:\documents and settings\Administrator\Local Settings\Application Data\ConduitEngine\EngineSettings.json c:\documents and settings\Administrator\Local Settings\Application Data\ConduitEngine\ExternalComponent\http___contextmenu_app_conduit-services_com_apps_TranslatedApps_ashx_productId=1&name=appContextMenu&locale=bg-bg.xml c:\documents and settings\Administrator\Local Settings\Application Data\ConduitEngine\ExternalComponent\http___contextmenu_app_conduit-services_com_apps_TranslatedApps_ashx_productId=1&name=appContextMenu2_0&locale=bg-bg.xml c:\documents and settings\Administrator\Local Settings\Application Data\ConduitEngine\ExternalComponent\http___contextmenu_engine_conduit-services_com_apps_TranslatedApps_ashx_productId=1&name=engineContextMenu&locale=bg-bg.xml c:\documents and settings\Administrator\Local Settings\Application Data\ConduitEngine\ExternalComponent\http___contextmenu_engine_conduit-services_com_apps_TranslatedApps_ashx_productId=1&name=engineContextMenu2_0&locale=bg-bg.xml c:\documents and settings\Administrator\Local Settings\Application Data\ConduitEngine\Repository\conduit_ConduitEngine\dynamicDialogs\data.txt c:\documents and settings\Administrator\Local Settings\Application Data\ConduitEngine\toolbar.cfg c:\program files\AskBarDis c:\program files\AskBarDis\bar\bin\askBar.dll c:\program files\AskBarDis\bar\bin\askPopStp.dll c:\program files\AskBarDis\bar\bin\psvince.dll c:\program files\AskBarDis\bar\Cache\000A3B81.bin c:\program files\AskBarDis\bar\Cache\000A3CD9.bin c:\program files\AskBarDis\bar\Cache\000A3FD7.bin c:\program files\AskBarDis\bar\Cache\000A413E.bin c:\program files\AskBarDis\bar\Cache\000A42B5.bin c:\program files\AskBarDis\bar\Cache\000A441C.bin c:\program files\AskBarDis\bar\Cache\000A4593.bin c:\program files\AskBarDis\bar\Cache\000A471A.bin c:\program files\AskBarDis\bar\Cache\000A4891.bin c:\program files\AskBarDis\bar\Cache\000A4A08.bin c:\program files\AskBarDis\bar\Cache\00E80C5B c:\program files\AskBarDis\bar\Cache\files.ini c:\program files\AskBarDis\bar\History\search c:\program files\AskBarDis\bar\Settings\config.dat c:\program files\AskBarDis\bar\Settings\config.dat.bak c:\program files\AskBarDis\bar\Settings\prevcfg.htm c:\program files\AskBarDis\bar\Settings\prevCfg2.htm c:\program files\AskBarDis\PopSwatter\History\notallow c:\program files\AskBarDis\unins000.dat c:\program files\AskBarDis\unins000.exe c:\program files\ConduitEngine c:\program files\ConduitEngine\appContextMenu.xml c:\program files\ConduitEngine\ConduitEngine.dll c:\program files\ConduitEngine\ConduitEngineHelper.exe c:\program files\ConduitEngine\engineContextMenu.xml c:\program files\ConduitEngine\EngineSettings.json c:\program files\ConduitEngine\prxConduitEngine.dll c:\program files\ConduitEngine\toolbar.cfg c:\program files\Softonic-Eng7\prxtbSof2.dll c:\windows\system32\ConduitEngine.tmp . . ((((((((((((((((((((((((( Files Created from 2011-03-15 to 2011-04-15 ))))))))))))))))))))))))))))))) . . 2011-04-14 15:54 . 2011-04-14 15:54 -------- d-----w- C:\_OTL 2011-04-13 20:53 . 2011-04-13 20:53 -------- d-----w- c:\documents and settings\Administrator\Application Data\ElevatedDiagnostics 2011-04-13 18:25 . 2011-04-13 18:25 -------- d-----w- c:\documents and settings\All Users\Application Data\UAB 2011-04-13 18:25 . 2011-04-13 18:25 -------- d-----w- c:\documents and settings\Administrator\Local Settings\Application Data\PC_Drivers_Headquarters 2011-04-13 17:23 . 2010-07-16 11:59 656320 ----a-w- c:\windows\system32\drivers\pctEFA.sys 2011-04-13 17:23 . 2010-07-16 11:59 338880 ----a-w- c:\windows\system32\drivers\pctDS.sys 2011-04-13 17:23 . 2011-01-17 06:10 251560 ----a-w- c:\windows\system32\drivers\pctgntdi.sys 2011-04-13 17:23 . 2010-12-10 13:57 160448 ----a-w- c:\windows\system32\drivers\PCTAppEvent.sys 2011-04-13 17:23 . 2010-12-10 10:24 239168 ----a-w- c:\windows\system32\drivers\PCTCore.sys 2011-04-13 17:23 . 2010-12-16 05:46 70536 ----a-w- c:\windows\system32\drivers\pctplsg.sys 2011-04-13 17:23 . 2011-04-13 17:29 -------- d-----w- c:\program files\Common Files\PC Tools 2011-04-13 17:23 . 2011-04-14 16:56 -------- d-----w- c:\program files\PC Tools Security 2011-04-13 17:23 . 2011-04-13 17:23 -------- d-----w- c:\documents and settings\Administrator\Application Data\PC Tools 2011-04-13 17:12 . 2011-04-13 17:23 -------- d-----w- c:\documents and settings\All Users\Application Data\PC Tools 2011-04-13 17:12 . 2011-04-13 17:12 -------- d-----w- c:\documents and settings\All Users\Application Data\PC Drivers HeadQuarters 2011-04-13 17:10 . 2011-04-13 17:10 -------- d-----w- c:\program files\PC Drivers HeadQuarters 2011-04-03 17:14 . 2011-03-18 17:55 142296 ----a-w- c:\program files\Mozilla Firefox\components\browsercomps.dll 2011-04-03 17:14 . 2011-03-18 17:55 781272 ----a-w- c:\program files\Mozilla Firefox\mozsqlite3.dll 2011-04-03 17:14 . 2011-03-18 17:55 1874904 ----a-w- c:\program files\Mozilla Firefox\mozjs.dll 2011-04-03 17:14 . 2011-03-18 17:55 16856 ----a-w- c:\program files\Mozilla Firefox\plugin-container.exe 2011-04-03 17:14 . 2011-03-18 17:55 728024 ----a-w- c:\program files\Mozilla Firefox\libGLESv2.dll 2011-04-03 17:14 . 2011-03-18 17:55 719832 ----a-w- c:\program files\Mozilla Firefox\mozcpp19.dll 2011-04-03 17:14 . 2011-03-18 17:55 1975768 ----a-w- c:\program files\Mozilla Firefox\D3DCompiler_42.dll 2011-04-03 17:14 . 2011-03-18 17:55 1893336 ----a-w- c:\program files\Mozilla Firefox\d3dx9_42.dll 2011-04-03 17:14 . 2011-03-18 17:55 15832 ----a-w- c:\program files\Mozilla Firefox\mozalloc.dll 2011-04-03 17:14 . 2011-03-18 17:55 142296 ----a-w- c:\program files\Mozilla Firefox\libEGL.dll . . . (((((((((((((((((((((((((((((((((((((((( Find3M Report )))))))))))))))))))))))))))))))))))))))))))))))))))) . 2011-03-07 05:33 . 2008-09-16 17:35 692736 ----a-w- c:\windows\system32\inetcomm.dll 2011-03-04 06:37 . 2008-04-14 12:00 420864 ----a-w- c:\windows\system32\vbscript.dll 2011-03-03 13:21 . 2008-04-14 12:00 1857920 ----a-w- c:\windows\system32\win32k.sys 2011-02-22 23:06 . 2008-04-14 12:00 916480 ----a-w- c:\windows\system32\wininet.dll 2011-02-22 23:06 . 2008-04-14 12:00 43520 ----a-w- c:\windows\system32\licmgr10.dll 2011-02-22 23:06 . 2008-04-14 12:00 1469440 ------w- c:\windows\system32\inetcpl.cpl 2011-02-22 11:41 . 2008-04-14 12:00 385024 ----a-w- c:\windows\system32\html.iec 2011-02-17 13:18 . 2008-04-14 12:00 455936 ----a-w- c:\windows\system32\drivers\mrxsmb.sys 2011-02-17 13:18 . 2008-04-14 12:00 357888 ----a-w- c:\windows\system32\drivers\srv.sys 2011-02-17 12:32 . 2009-05-09 00:00 5120 ----a-w- c:\windows\system32\xpsp4res.dll 2011-02-15 12:56 . 2008-04-14 12:00 290432 ----a-w- c:\windows\system32\atmfd.dll 2011-02-09 13:53 . 2008-04-14 12:00 270848 ----a-w- c:\windows\system32\sbe.dll 2011-02-09 13:53 . 2008-04-14 12:00 186880 ----a-w- c:\windows\system32\encdec.dll 2011-02-08 13:33 . 2008-04-14 12:00 978944 ----a-w- c:\windows\system32\mfc42.dll 2011-02-08 13:33 . 2008-04-14 12:00 974848 ----a-w- c:\windows\system32\mfc42u.dll 2011-02-02 07:58 . 2008-09-16 17:33 2067456 ----a-w- c:\windows\system32\mstscax.dll 2011-01-27 11:57 . 2008-09-16 17:33 677888 ----a-w- c:\windows\system32\mstsc.exe 2011-01-21 14:44 . 2008-04-14 12:00 439296 ----a-w- c:\windows\system32\shimgvw.dll 2011-03-18 17:55 . 2011-04-03 17:14 142296 ----a-w- c:\program files\mozilla firefox\components\browsercomps.dll . . ((((((((((((((((((((((((((((( SnapShot@2011-04-14_18.58.12 ))))))))))))))))))))))))))))))))))))))))) . + 2011-04-15 07:19 . 2011-04-15 07:19 16384 c:\windows\temp\Perflib_Perfdata_858.dat + 2008-06-09 05:10 . 2008-06-09 05:10 82224 c:\windows\system32\accelerometerst.exe . ((((((((((((((((((((((((((((((((((((( Reg Loading Points )))))))))))))))))))))))))))))))))))))))))))))))))) . . *Note* empty entries & legit default entries are not shown REGEDIT4 . [HKEY_CURRENT_USER\SOFTWARE\Microsoft\Windows\CurrentVersion\Run] "Skype"="c:\program files\Skype\Phone\Skype.exe" [2008-02-01 21898024] . [HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\Run] "StartCCC"="c:\program files\ATI Technologies\ATI.ACE\Core-Static\CLIStart.exe" [2008-01-21 61440] "QlbCtrl.exe"="c:\program files\Hewlett-Packard\HP Quick Launch Buttons\QlbCtrl.exe" [2008-06-03 177456] "accrdsub"="c:\program files\ActivIdentity\ActivClient\accrdsub.exe" [2007-05-15 293168] "PTHOSTTR"="c:\program files\Hewlett-Packard\HP ProtectTools Security Manager\PTHOSTTR.EXE" [2008-06-10 238896] "CognizanceTS"="c:\progra~1\HEWLET~1\IAM\Bin\ASTSVCC.dll" [2008-06-02 24848] "QuickTime Task"="c:\program files\QuickTime\QTTask.exe" [2010-03-18 421888] "iTunesHelper"="d:\programs\iTunes\iTunesHelper.exe" [2010-07-21 141608] "SunJavaUpdateSched"="c:\program files\Common Files\Java\Java Update\jusched.exe" [2010-05-14 248552] "Flashget"="c:\program files\FlashGet\flashget.exe" [2007-09-25 2007088] . [HKEY_USERS\.DEFAULT\Software\Microsoft\Windows\CurrentVersion\Run] "CTFMON.EXE"="c:\windows\system32\CTFMON.EXE" [2008-04-14 15360] . c:\documents and settings\Administrator\Start Menu\Programs\Startup\ Adobe Gamma.lnk - c:\program files\Common Files\Adobe\Calibration\Adobe Gamma Loader.exe [2005-3-16 113664] hamachi.lnk - c:\program files\Hamachi\hamachi.exe [2008-12-2 625952] . c:\documents and settings\All Users\Start Menu\Programs\Startup\ Bluetooth.lnk - c:\program files\WIDCOMM\Bluetooth Software\BTTray.exe [2008-5-12 576104] FlexType 2K.lnk - c:\windows\Datecs\Flex2K.exe [2008-9-16 151552] McAfee Security Scan Plus.lnk - c:\program files\McAfee Security Scan\2.0.181\SSScheduler.exe [2010-1-15 255536] . [HKEY_LOCAL_MACHINE\software\microsoft\windows nt\currentversion\winlogon\notify\ackpbsc] 2007-05-15 13:08 112640 ----a-w- c:\windows\system32\ackpbsc.dll . [HKEY_LOCAL_MACHINE\software\microsoft\windows nt\currentversion\winlogon\notify\acunlock] 2007-05-15 13:08 281088 ----a-w- c:\program files\ActivIdentity\ActivClient\acunlock.dll . [HKEY_LOCAL_MACHINE\software\microsoft\windows nt\currentversion\winlogon\notify\OneCard] 2008-06-02 09:06 112400 ----a-w- c:\program files\Hewlett-Packard\IAM\Bin\ASWLNPkg.dll . [HKEY_LOCAL_MACHINE\SYSTEM\CurrentControlSet\Control\SafeBoot\Minimal\Wdf01000.sys] @="Driver" . [HKLM\~\startupfolder\C:^DOCUME~1^ALLUSE~1^Start Menu^Programs^Startup^DVD Check.lnk] path=c:\docume~1\ALLUSE~1\Start Menu\Programs\Startup\DVD Check.lnk backup=c:\windows\pss\DVD Check.lnkCommon Startup . [HKEY_LOCAL_MACHINE\software\microsoft\shared tools\msconfig\startupreg\Skype] 2008-02-01 15:22 21898024 ----a-r- c:\program files\Skype\Phone\Skype.exe . [HKLM\~\services\sharedaccess\parameters\firewallpolicy\standardprofile\AuthorizedApplications\List] "%windir%\\Network Diagnostic\\xpnetdiag.exe"= "%windir%\\system32\\sessmgr.exe"= "c:\\Program Files\\FlashGet\\flashget.exe"= "d:\\Programs\\StrongDC++\\StrongDC.exe"= "d:\\Games\\CS\\hl.exe"= "d:\\Programs\\uTorrent\\uTorrent.exe"= "c:\\WINDOWS\\system32\\PnkBstrA.exe"= "c:\\WINDOWS\\system32\\PnkBstrB.exe"= "c:\\Program Files\\Skype\\Plugin Manager\\skypePM.exe"= "c:\\Program Files\\QuickTime\\QuickTimePlayer.exe"= "c:\\Program Files\\Bonjour\\mDNSResponder.exe"= "d:\\Programs\\iTunes\\iTunes.exe"= "c:\\Program Files\\TeamViewer\\Version6\\TeamViewer.exe"= "c:\\Program Files\\TeamViewer\\Version6\\TeamViewer_Service.exe"= "d:\\Programs\\TeamViewer\\Version4\\TeamViewer.exe"= "c:\\Program Files\\Skype\\Phone\\Skype.exe"= . [HKLM\~\services\sharedaccess\parameters\firewallpolicy\standardprofile\GloballyOpenPorts\List] "14265:TCP"= 14265:TCP:BitComet 14265 TCP "14265:UDP"= 14265:UDP:BitComet 14265 UDP . R0 ahcix86;ahcix86;c:\windows\system32\drivers\ahcix86.sys [17.9.2008 і. 01:11 174600] R0 Amddfltr;Amd Disk Lower Filter Driver;c:\windows\system32\drivers\Amddfltr.sys [16.9.2008 і. 20:51 15416] R0 PCTCore;PCTools KDS;c:\windows\system32\drivers\PCTCore.sys [13.4.2011 і. 20:23 239168] R0 pctDS;PC Tools Data Store;c:\windows\system32\drivers\pctDS.sys [13.4.2011 і. 20:23 338880] R0 pctEFA;PC Tools Extended File Attributes;c:\windows\system32\drivers\pctEFA.sys [13.4.2011 і. 20:23 656320] R0 SafeBoot;SafeBoot;c:\windows\system32\drivers\SafeBoot.sys [05.6.2008 і. 17:08 109184] R0 SbAlg;SbAlg;c:\windows\system32\drivers\SbAlg.sys [05.6.2008 і. 17:08 51376] R0 SbFsLock;SbFsLock;c:\windows\system32\drivers\SbFsLock.sys [05.6.2008 і. 17:08 12928] R0 SFAUDIO;Sonic Focus DSP Driver;c:\windows\system32\drivers\sfaudio.sys [28.3.2008 і. 10:14 24064] R1 RsvLock;RsvLock;c:\windows\system32\drivers\rsvlock.sys [05.6.2008 і. 17:08 12496] R2 accoca;ActivClient Middleware Service;c:\program files\ActivIdentity\ActivClient\accoca.exe [15.5.2007 і. 16:08 182576] R2 ASBroker;Logon Session Broker;c:\windows\System32\svchost.exe -k Cognizance [14.4.2008 і. 15:00 14336] R2 ASChannel;Local Communication Channel;c:\windows\System32\svchost.exe -k Cognizance [14.4.2008 і. 15:00 14336] R2 HP ProtectTools Service;HP ProtectTools Service;c:\program files\Hewlett-Packard\HP ProtectTools Security Manager\PTChangeFilterService.exe [10.6.2008 і. 11:13 18944] R2 HpFkCryptService;Drive Encryption Service;c:\program files\Hewlett-Packard\Drive Encryption\HpFkCrypt.exe [05.6.2008 і. 17:07 256512] R2 McAfee SiteAdvisor Service;McAfee SiteAdvisor Service;c:\progra~1\mcafee\SITEAD~1\mcsacore.exe [05.1.2011 і. 15:58 88176] R3 Com4QLBEx;Com4QLBEx;c:\program files\Hewlett-Packard\HP Quick Launch Buttons\Com4QLBEx.exe [16.9.2008 і. 21:09 193840] R3 teamviewervpn;TeamViewer VPN Adapter;c:\windows\system32\drivers\teamviewervpn.sys [25.1.2008 і. 12:12 25088] S2 clr_optimization_v4.0.30319_32;Microsoft .NET Framework NGEN v4.0.30319_X86;c:\windows\Microsoft.NET\Framework\v4.0.30319\mscorsvw.exe [18.3.2010 і. 14:16 130384] S3 McComponentHostService;McAfee Security Scan Component Host Service;c:\program files\McAfee Security Scan\2.0.181\McCHSvc.exe [15.1.2010 і. 15:49 227232] S3 SCR3XX2K;SCR3xx USB SmartCardReader;c:\windows\system32\drivers\SCR3XX2K.sys [21.6.2007 і. 04:40 56448] S3 sdAuxService;PC Tools Auxiliary Service;c:\program files\PC Tools Security\pctsAuxs.exe [13.4.2011 і. 20:23 366840] S3 WPFFontCache_v0400;Windows Presentation Foundation Font Cache 4.0.0.0;c:\windows\Microsoft.NET\Framework\v4.0.30319\WPF\WPFFontCache_v0400.exe [18.3.2010 і. 14:16 753504] S4 sptd;sptd;c:\windows\system32\drivers\sptd.sys [16.9.2008 і. 21:27 685816] . [HKEY_LOCAL_MACHINE\software\microsoft\windows nt\currentversion\svchost] HPZ12 REG_MULTI_SZ Pml Driver HPZ12 Net Driver HPZ12 Cognizance REG_MULTI_SZ ASBroker ASChannel . Contents of the 'Scheduled Tasks' folder . 2011-04-12 c:\windows\Tasks\AppleSoftwareUpdate.job - c:\program files\Apple Software Update\SoftwareUpdate.exe [2009-10-22 08:50] . 2010-06-07 c:\windows\Tasks\expressripShakeIcon.job - c:\program files\NCH Swift Sound\ExpressRip\expressrip.exe [2010-05-28 06:05] . 2011-04-15 c:\windows\Tasks\User_Feed_Synchronization-{723CA83C-C32A-448C-9FE6-94BF21620942}.job - c:\windows\system32\msfeedssync.exe [2009-03-08 02:31] . . ------- Supplementary Scan ------- . uInternet Connection Wizard,ShellNext = iexplore uInternet Settings,ProxyOverride = *.local uSearchURL,(Default) = hxxp://toolbar.ask.com/toolbarv/askRedirect?o=101699&gct=&gc=1&q=%s IE: &Download All using 4shared Desktop - d:\programs\4shared Desktop\down_all.htm IE: &Download All with FlashGet - c:\program files\FlashGet\jc_all.htm IE: &Download with FlashGet - c:\program files\FlashGet\jc_link.htm IE: Add to Google Photos Screensa&ver - c:\windows\system32\GPhotos.scr/200 IE: E&xport to Microsoft Excel - c:\progra~1\MICROS~2\OFFICE11\EXCEL.EXE/3000 IE: Send to &Bluetooth Device... - c:\program files\WIDCOMM\Bluetooth Software\btsendto_ie_ctx.htm IE: Send To Bluetooth - c:\program files\WIDCOMM\Bluetooth Software\btsendto_ie.htm LSP: c:\program files\Common Files\PC Tools\Lsp\PCTLsp.dll TCP: {9B2D9B85-5FF1-4AE4-AD0F-97B50F0AD220} = 212.39.90.42,212.39.90.43 DPF: Microsoft XML Parser for Java - file://c:\windows\Java\classes\xmldso.cab FF - ProfilePath - c:\documents and settings\Administrator\Application Data\Mozilla\Firefox\Profiles\korvvd8g.default\ FF - prefs.js: browser.startup.homepage - google.bg FF - prefs.js: keyword.URL - hxxp://search.yahoo.com/search?fr=mcafee&p= . - - - - ORPHANS REMOVED - - - - . MSConfigStartUp-Adobe Reader Speed Launcher - c:\program files\Adobe\Reader 8.0\Reader\Reader_sl.exe MSConfigStartUp-WinampAgent - c:\program files\Winamp\winampa.exe AddRemove-Ask Toolbar_is1 - c:\program files\AskBarDis\unins000.exe . . . ************************************************************************** . catchme 0.3.1398 W2K/XP/Vista - rootkit/stealth malware detector by Gmer, http://www.gmer.net Rootkit scan 2011-04-15 10:20 Windows 5.1.2600 Service Pack 3 NTFS . scanning hidden processes ... . scanning hidden autostart entries ... . scanning hidden files ... . scan completed successfully hidden files: 0 . ************************************************************************** . --------------------- DLLs Loaded Under Running Processes --------------------- . - - - - - - - > 'winlogon.exe'(1252) c:\windows\system32\ackpbsc.dll c:\windows\system32\aclog.dll c:\windows\system32\ACLIBEAY.dll c:\windows\system32\acevtsub.dll c:\windows\system32\asphat32.dll c:\windows\system32\acerrmes.dll c:\windows\system32\aspcom.dll c:\program files\ActivIdentity\ActivClient\Resources\Merged\acerrmrc.dll c:\program files\ActivIdentity\ActivClient\Resources\Merged\asphatrc.dll c:\windows\system32\msi.dll c:\windows\system32\Ati2evxx.dll c:\program files\Hewlett-Packard\IAM\Bin\ASWLNPkg.dll c:\program files\Hewlett-Packard\IAM\bin\ItMsg.dll c:\program files\Hewlett-Packard\IAM\Bin\TrayIcon.dll c:\program files\Hewlett-Packard\IAM\bin\brand.dll c:\program files\Hewlett-Packard\IAM\Bin\AsChnl.dll c:\program files\Hewlett-Packard\IAM\Bin\HPPlugIn.dll c:\program files\Hewlett-Packard\HP ProtectTools Security Manager\PTHostServices.dll c:\program files\Hewlett-Packard\HP ProtectTools Security Manager\Interop.HPQWMIEXLib.dll c:\program files\ActivIdentity\ActivClient\acunlock.dll c:\windows\system32\aipingui.dll c:\program files\ActivIdentity\ActivClient\Resources\Merged\aipinguirc.dll c:\program files\ActivIdentity\ActivClient\resources\acCobAPIrc.dll c:\program files\ActivIdentity\ActivClient\Resources\Merged\acunlockrc.dll c:\program files\Hewlett-Packard\HP ProtectTools Security Manager\Interop.PTHstServsLib.dll c:\program files\Hewlett-Packard\HP ProtectTools Security Manager\PTHstServs.dll c:\program files\Hewlett-Packard\HP ProtectTools Security Manager\BIOSDomain.dll c:\program files\Hewlett-Packard\HP ProtectTools Security Manager\Interop.PTPluginLib.dll c:\program files\Hewlett-Packard\HP ProtectTools Security Manager\PTStrings.dll c:\program files\Hewlett-Packard\HP ProtectTools Security Manager\HPjCard.dll c:\windows\system32\acomx.dll c:\windows\system32\acbsi21.dll c:\program files\Hewlett-Packard\IAM\Bin\ItVCClient.dll c:\program files\Hewlett-Packard\IAM\Bin\ItReports.DLL c:\program files\Hewlett-Packard\IAM\Bin\ItVCard.dll c:\program files\Hewlett-Packard\IAM\Bin\NetAdmin.dll . - - - - - - - > 'lsass.exe'(1308) c:\program files\Common Files\PC Tools\Lsp\PCTLsp.dll . - - - - - - - > 'explorer.exe'(6264) c:\windows\system32\WININET.dll c:\program files\FlashGet\fgmgr.dll c:\progra~1\mcafee\SITEAD~1\saHook.dll c:\windows\system32\newdll.dll c:\windows\system32\APSHook.dll c:\windows\system32\webcheck.dll c:\windows\system32\IEFRAME.dll c:\progra~1\COMMON~1\MICROS~1\WEBCOM~1\10\OWC10.DLL c:\windows\system32\Msi.dll c:\program files\Common Files\Microsoft Shared\Web Components\10\1026\OWCI10.DLL c:\progra~1\COMMON~1\MICROS~1\WEBCOM~1\11\OWC11.DLL c:\program files\Common Files\Microsoft Shared\Web Components\11\1026\OWCI11.DLL c:\windows\system32\btmmhook.dll c:\windows\system32\mshtml.dll c:\windows\system32\msls31.dll . ------------------------ Other Running Processes ------------------------ . c:\windows\system32\Ati2evxx.exe c:\program files\WIDCOMM\Bluetooth Software\bin\btwdins.exe c:\windows\System32\SCardSvr.exe c:\program files\ActivIdentity\ActivClient\acevents.exe c:\windows\system32\Ati2evxx.exe c:\program files\Hewlett-Packard\IAM\Bin\AsGHost.exe c:\windows\system32\agrsmsvc.exe c:\program files\Common Files\Apple\Mobile Device Support\AppleMobileDeviceService.exe c:\program files\Bonjour\mDNSResponder.exe c:\program files\Java\jre6\bin\jqs.exe c:\program files\Microsoft SQL Server\MSSQL.1\MSSQL\Binn\sqlservr.exe c:\windows\system32\PnkBstrA.exe c:\program files\Microsoft SQL Server\90\Shared\sqlwriter.exe c:\windows\system32\wdfmgr.exe c:\progra~1\WIDCOMM\BLUETO~1\BTSTAC~1.EXE c:\program files\ActivIdentity\ActivClient\acevents.exe c:\program files\Hewlett-Packard\Shared\hpqwmiex.exe c:\windows\system32\rundll32.exe c:\windows\system32\wscntfy.exe c:\program files\iPod\bin\iPodService.exe c:\program files\ATI Technologies\ATI.ACE\Core-Static\MOM.exe c:\program files\ATI Technologies\ATI.ACE\Core-Static\ccc.exe . ************************************************************************** . Completion time: 2011-04-15 10:26:08 - machine was rebooted ComboFix-quarantined-files.txt 2011-04-15 07:25 ComboFix2.txt 2011-04-14 19:03 ComboFix3.txt 2009-06-14 17:56 . Pre-Run: 21 367 484 416 bytes free Post-Run: 21 388 529 664 bytes free . - - End Of File - - D9C762702FD591151764467101E436D8
-
ComboFix лог: ComboFix 11-04-13.06 - Administrator 04.2011 г. 21:46:53.5.2 - x86 Microsoft Windows XP Professional 5.1.2600.3.1251.359.1033.18.1789.485 [GMT 3:00] Running from: c:\documents and settings\Administrator\Desktop\ComboFix.exe . . ((((((((((((((((((((((((((((((((((((((( Other Deletions ))))))))))))))))))))))))))))))))))))))))))))))))) . . c:\documents and settings\Administrator\Application Data\PriceGong c:\documents and settings\Administrator\Application Data\PriceGong\Data\1.xml c:\documents and settings\Administrator\Application Data\PriceGong\Data\a.xml c:\documents and settings\Administrator\Application Data\PriceGong\Data\b.xml c:\documents and settings\Administrator\Application Data\PriceGong\Data\c.xml c:\documents and settings\Administrator\Application Data\PriceGong\Data\d.xml c:\documents and settings\Administrator\Application Data\PriceGong\Data\e.xml c:\documents and settings\Administrator\Application Data\PriceGong\Data\f.xml c:\documents and settings\Administrator\Application Data\PriceGong\Data\g.xml c:\documents and settings\Administrator\Application Data\PriceGong\Data\h.xml c:\documents and settings\Administrator\Application Data\PriceGong\Data\i.xml c:\documents and settings\Administrator\Application Data\PriceGong\Data\J.xml c:\documents and settings\Administrator\Application Data\PriceGong\Data\k.xml c:\documents and settings\Administrator\Application Data\PriceGong\Data\l.xml c:\documents and settings\Administrator\Application Data\PriceGong\Data\m.xml c:\documents and settings\Administrator\Application Data\PriceGong\Data\mru.xml c:\documents and settings\Administrator\Application Data\PriceGong\Data\n.xml c:\documents and settings\Administrator\Application Data\PriceGong\Data\o.xml c:\documents and settings\Administrator\Application Data\PriceGong\Data\p.xml c:\documents and settings\Administrator\Application Data\PriceGong\Data\q.xml c:\documents and settings\Administrator\Application Data\PriceGong\Data\r.xml c:\documents and settings\Administrator\Application Data\PriceGong\Data\s.xml c:\documents and settings\Administrator\Application Data\PriceGong\Data\t.xml c:\documents and settings\Administrator\Application Data\PriceGong\Data\u.xml c:\documents and settings\Administrator\Application Data\PriceGong\Data\v.xml c:\documents and settings\Administrator\Application Data\PriceGong\Data\w.xml c:\documents and settings\Administrator\Application Data\PriceGong\Data\x.xml c:\documents and settings\Administrator\Application Data\PriceGong\Data\y.xml c:\documents and settings\Administrator\Application Data\PriceGong\Data\z.xml c:\documents and settings\Administrator\Desktop\С°Ѕтр° c:\documents and settings\Administrator\Desktop\Andrea c:\documents and settings\Administrator\Desktop\Blank c:\documents and settings\Administrator\Desktop\Desislava c:\documents and settings\Administrator\Desktop\DJ Dario G feat DJ Sako c:\documents and settings\Administrator\Desktop\Jamie Foxx ft. Kanye West c:\documents and settings\Administrator\Desktop\Lil Wayne c:\documents and settings\Administrator\Desktop\Nicola Fasano c:\documents and settings\Administrator\Desktop\Pitbull c:\documents and settings\Administrator\Desktop\SNG c:\documents and settings\Administrator\Desktop\Teodora c:\documents and settings\Administrator\Desktop\Wisin c:\documents and settings\Administrator\Recent\Thumbs.db c:\documents and settings\Administrator\WINDOWS c:\documents and settings\All Users\Application Data\Adobe Systems c:\documents and settings\All Users\Application Data\Adobe Systems\Product licenses\B2C59000.dat c:\program files\AskSearch\bin\DefaultSearch.dll c:\windows\system32\html c:\windows\system32\html\calendar.html c:\windows\system32\html\calendarbottom.html c:\windows\system32\html\calendartop.html c:\windows\system32\html\crystalexportdialog.htm c:\windows\system32\html\crystalprinthost.html c:\windows\system32\images c:\windows\system32\images\toolbar\calendar.gif c:\windows\system32\images\toolbar\crlogo.gif c:\windows\system32\images\toolbar\export.gif c:\windows\system32\images\toolbar\export_over.gif c:\windows\system32\images\toolbar\exportd.gif c:\windows\system32\images\toolbar\First.gif c:\windows\system32\images\toolbar\first_over.gif c:\windows\system32\images\toolbar\Firstd.gif c:\windows\system32\images\toolbar\gotopage.gif c:\windows\system32\images\toolbar\gotopage_over.gif c:\windows\system32\images\toolbar\gotopaged.gif c:\windows\system32\images\toolbar\grouptree.gif c:\windows\system32\images\toolbar\grouptree_over.gif c:\windows\system32\images\toolbar\grouptreed.gif c:\windows\system32\images\toolbar\grouptreepressed.gif c:\windows\system32\images\toolbar\Last.gif c:\windows\system32\images\toolbar\last_over.gif c:\windows\system32\images\toolbar\Lastd.gif c:\windows\system32\images\toolbar\Next.gif c:\windows\system32\images\toolbar\next_over.gif c:\windows\system32\images\toolbar\Nextd.gif c:\windows\system32\images\toolbar\Prev.gif c:\windows\system32\images\toolbar\prev_over.gif c:\windows\system32\images\toolbar\Prevd.gif c:\windows\system32\images\toolbar\print.gif c:\windows\system32\images\toolbar\print_over.gif c:\windows\system32\images\toolbar\printd.gif c:\windows\system32\images\toolbar\Refresh.gif c:\windows\system32\images\toolbar\refresh_over.gif c:\windows\system32\images\toolbar\refreshd.gif c:\windows\system32\images\toolbar\Search.gif c:\windows\system32\images\toolbar\search_over.gif c:\windows\system32\images\toolbar\searchd.gif c:\windows\system32\images\toolbar\up.gif c:\windows\system32\images\toolbar\up_over.gif c:\windows\system32\images\toolbar\upd.gif c:\windows\system32\images\tree\begindots.gif c:\windows\system32\images\tree\beginminus.gif c:\windows\system32\images\tree\beginplus.gif c:\windows\system32\images\tree\blank.gif c:\windows\system32\images\tree\blankdots.gif c:\windows\system32\images\tree\dots.gif c:\windows\system32\images\tree\lastdots.gif c:\windows\system32\images\tree\lastminus.gif c:\windows\system32\images\tree\lastplus.gif c:\windows\system32\images\tree\Magnify.gif c:\windows\system32\images\tree\minus.gif c:\windows\system32\images\tree\minusbox.gif c:\windows\system32\images\tree\plus.gif c:\windows\system32\images\tree\plusbox.gif c:\windows\system32\images\tree\singleminus.gif c:\windows\system32\images\tree\singleplus.gif c:\windows\system32\klipxm32.dll c:\windows\winhelp.ini . . ((((((((((((((((((((((((( Files Created from 2011-03-14 to 2011-04-14 ))))))))))))))))))))))))))))))) . . 2011-04-14 15:54 . 2011-04-14 15:54 -------- d-----w- C:\_OTL 2011-04-13 20:53 . 2011-04-13 20:53 -------- d-----w- c:\documents and settings\Administrator\Application Data\ElevatedDiagnostics 2011-04-13 18:25 . 2011-04-13 18:25 -------- d-----w- c:\documents and settings\All Users\Application Data\UAB 2011-04-13 18:25 . 2011-04-13 18:25 -------- d-----w- c:\documents and settings\Administrator\Local Settings\Application Data\PC_Drivers_Headquarters 2011-04-13 17:23 . 2010-07-16 11:59 656320 ----a-w- c:\windows\system32\drivers\pctEFA.sys 2011-04-13 17:23 . 2010-07-16 11:59 338880 ----a-w- c:\windows\system32\drivers\pctDS.sys 2011-04-13 17:23 . 2011-01-17 06:10 251560 ----a-w- c:\windows\system32\drivers\pctgntdi.sys 2011-04-13 17:23 . 2010-12-10 13:57 160448 ----a-w- c:\windows\system32\drivers\PCTAppEvent.sys 2011-04-13 17:23 . 2010-12-10 10:24 239168 ----a-w- c:\windows\system32\drivers\PCTCore.sys 2011-04-13 17:23 . 2010-12-16 05:46 70536 ----a-w- c:\windows\system32\drivers\pctplsg.sys 2011-04-13 17:23 . 2011-04-13 17:29 -------- d-----w- c:\program files\Common Files\PC Tools 2011-04-13 17:23 . 2011-04-14 16:56 -------- d-----w- c:\program files\PC Tools Security 2011-04-13 17:23 . 2011-04-13 17:23 -------- d-----w- c:\documents and settings\Administrator\Application Data\PC Tools 2011-04-13 17:12 . 2011-04-13 17:23 -------- d-----w- c:\documents and settings\All Users\Application Data\PC Tools 2011-04-13 17:12 . 2011-04-13 17:12 -------- d-----w- c:\documents and settings\All Users\Application Data\PC Drivers HeadQuarters 2011-04-13 17:10 . 2011-04-13 17:10 -------- d-----w- c:\program files\PC Drivers HeadQuarters 2011-04-03 17:14 . 2011-03-18 17:55 142296 ----a-w- c:\program files\Mozilla Firefox\components\browsercomps.dll 2011-04-03 17:14 . 2011-03-18 17:55 781272 ----a-w- c:\program files\Mozilla Firefox\mozsqlite3.dll 2011-04-03 17:14 . 2011-03-18 17:55 1874904 ----a-w- c:\program files\Mozilla Firefox\mozjs.dll 2011-04-03 17:14 . 2011-03-18 17:55 16856 ----a-w- c:\program files\Mozilla Firefox\plugin-container.exe 2011-04-03 17:14 . 2011-03-18 17:55 728024 ----a-w- c:\program files\Mozilla Firefox\libGLESv2.dll 2011-04-03 17:14 . 2011-03-18 17:55 719832 ----a-w- c:\program files\Mozilla Firefox\mozcpp19.dll 2011-04-03 17:14 . 2011-03-18 17:55 1975768 ----a-w- c:\program files\Mozilla Firefox\D3DCompiler_42.dll 2011-04-03 17:14 . 2011-03-18 17:55 1893336 ----a-w- c:\program files\Mozilla Firefox\d3dx9_42.dll 2011-04-03 17:14 . 2011-03-18 17:55 15832 ----a-w- c:\program files\Mozilla Firefox\mozalloc.dll 2011-04-03 17:14 . 2011-03-18 17:55 142296 ----a-w- c:\program files\Mozilla Firefox\libEGL.dll 2011-04-01 10:42 . 2011-04-01 11:08 -------- d-----w- c:\documents and settings\Administrator\Local Settings\Application Data\ConduitEngine 2011-04-01 10:42 . 2011-04-01 10:42 -------- d-----w- c:\program files\ConduitEngine 2011-04-01 10:42 . 2011-04-01 10:42 0 ----a-w- c:\windows\system32\ConduitEngine.tmp . . . (((((((((((((((((((((((((((((((((((((((( Find3M Report )))))))))))))))))))))))))))))))))))))))))))))))))))) . 2011-03-07 05:33 . 2008-09-16 17:35 692736 ----a-w- c:\windows\system32\inetcomm.dll 2011-03-04 06:37 . 2008-04-14 12:00 420864 ----a-w- c:\windows\system32\vbscript.dll 2011-03-03 13:21 . 2008-04-14 12:00 1857920 ----a-w- c:\windows\system32\win32k.sys 2011-02-22 23:06 . 2008-04-14 12:00 916480 ----a-w- c:\windows\system32\wininet.dll 2011-02-22 23:06 . 2008-04-14 12:00 43520 ----a-w- c:\windows\system32\licmgr10.dll 2011-02-22 23:06 . 2008-04-14 12:00 1469440 ------w- c:\windows\system32\inetcpl.cpl 2011-02-22 11:41 . 2008-04-14 12:00 385024 ----a-w- c:\windows\system32\html.iec 2011-02-17 13:18 . 2008-04-14 12:00 455936 ----a-w- c:\windows\system32\drivers\mrxsmb.sys 2011-02-17 13:18 . 2008-04-14 12:00 357888 ----a-w- c:\windows\system32\drivers\srv.sys 2011-02-17 12:32 . 2009-05-09 00:00 5120 ----a-w- c:\windows\system32\xpsp4res.dll 2011-02-15 12:56 . 2008-04-14 12:00 290432 ----a-w- c:\windows\system32\atmfd.dll 2011-02-09 13:53 . 2008-04-14 12:00 270848 ----a-w- c:\windows\system32\sbe.dll 2011-02-09 13:53 . 2008-04-14 12:00 186880 ----a-w- c:\windows\system32\encdec.dll 2011-02-08 13:33 . 2008-04-14 12:00 978944 ----a-w- c:\windows\system32\mfc42.dll 2011-02-08 13:33 . 2008-04-14 12:00 974848 ----a-w- c:\windows\system32\mfc42u.dll 2011-02-02 07:58 . 2008-09-16 17:33 2067456 ----a-w- c:\windows\system32\mstscax.dll 2011-01-27 11:57 . 2008-09-16 17:33 677888 ----a-w- c:\windows\system32\mstsc.exe 2011-01-21 14:44 . 2008-04-14 12:00 439296 ----a-w- c:\windows\system32\shimgvw.dll 2011-03-18 17:55 . 2011-04-03 17:14 142296 ----a-w- c:\program files\mozilla firefox\components\browsercomps.dll . <pre> c:\program files\Analog Devices\Core\smax4pnp .exe c:\program files\Hewlett-Packard\HP Wireless Assistant\hpwamain .exe c:\program files\Synaptics\SynTP\syntpenh .exe c:\windows\system32\accelerometerst .exe </pre> . ((((((((((((((((((((((((((((((((((((( Reg Loading Points )))))))))))))))))))))))))))))))))))))))))))))))))) . . *Note* empty entries & legit default entries are not shown REGEDIT4 . [HKEY_CURRENT_USER\Software\Microsoft\Internet Explorer\URLSearchHooks] "{414b6d9d-4a95-4e8d-b5b1-149dd2d93bb3}"= "c:\program files\Softonic-Eng7\prxtbSof2.dll" [2011-01-17 175912] . [HKEY_CLASSES_ROOT\clsid\{414b6d9d-4a95-4e8d-b5b1-149dd2d93bb3}] . [HKEY_LOCAL_MACHINE\~\Browser Helper Objects\{201f27d4-3704-41d6-89c1-aa35e39143ed}] 2008-11-18 09:58 333192 ----a-w- c:\program files\AskBarDis\bar\bin\askBar.dll . [HKEY_LOCAL_MACHINE\~\Browser Helper Objects\{30F9B915-B755-4826-820B-08FBA6BD249D}] 2011-01-17 14:54 175912 ----a-w- c:\program files\ConduitEngine\prxConduitEngine.dll . [HKEY_LOCAL_MACHINE\~\Browser Helper Objects\{414b6d9d-4a95-4e8d-b5b1-149dd2d93bb3}] 2011-01-17 14:54 175912 ----a-w- c:\program files\Softonic-Eng7\prxtbSof2.dll . [HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Internet Explorer\Toolbar] "{3041d03e-fd4b-44e0-b742-2d9b88305f98}"= "c:\program files\AskBarDis\bar\bin\askBar.dll" [2008-11-18 333192] "{414b6d9d-4a95-4e8d-b5b1-149dd2d93bb3}"= "c:\program files\Softonic-Eng7\prxtbSof2.dll" [2011-01-17 175912] . [HKEY_CLASSES_ROOT\clsid\{3041d03e-fd4b-44e0-b742-2d9b88305f98}] [HKEY_CLASSES_ROOT\TypeLib\{4b1c1e16-6b34-430e-b074-5928eca4c150}] . [HKEY_CLASSES_ROOT\clsid\{414b6d9d-4a95-4e8d-b5b1-149dd2d93bb3}] . [HKEY_CURRENT_USER\Software\Microsoft\Internet Explorer\Toolbar\Webbrowser] "{414B6D9D-4A95-4E8D-B5B1-149DD2D93BB3}"= "c:\program files\Softonic-Eng7\prxtbSof2.dll" [2011-01-17 175912] "{3041D03E-FD4B-44E0-B742-2D9B88305F98}"= "c:\program files\AskBarDis\bar\bin\askBar.dll" [2008-11-18 333192] . [HKEY_CLASSES_ROOT\clsid\{414b6d9d-4a95-4e8d-b5b1-149dd2d93bb3}] . [HKEY_CLASSES_ROOT\clsid\{3041d03e-fd4b-44e0-b742-2d9b88305f98}] [HKEY_CLASSES_ROOT\TypeLib\{4b1c1e16-6b34-430e-b074-5928eca4c150}] . [HKEY_CURRENT_USER\SOFTWARE\Microsoft\Windows\CurrentVersion\Run] "Skype"="c:\program files\Skype\Phone\Skype.exe" [2008-02-01 21898024] . [HKEY_LOCAL_MACHINE\SOFTWARE\Microsoft\Windows\CurrentVersion\Run] "StartCCC"="c:\program files\ATI Technologies\ATI.ACE\Core-Static\CLIStart.exe" [2008-01-21 61440] "QlbCtrl.exe"="c:\program files\Hewlett-Packard\HP Quick Launch Buttons\QlbCtrl.exe" [2008-06-03 177456] "accrdsub"="c:\program files\ActivIdentity\ActivClient\accrdsub.exe" [2007-05-15 293168] "PTHOSTTR"="c:\program files\Hewlett-Packard\HP ProtectTools Security Manager\PTHOSTTR.EXE" [2008-06-10 238896] "CognizanceTS"="c:\progra~1\HEWLET~1\IAM\Bin\ASTSVCC.dll" [2008-06-02 24848] "QuickTime Task"="c:\program files\QuickTime\QTTask.exe" [2010-03-18 421888] "iTunesHelper"="d:\programs\iTunes\iTunesHelper.exe" [2010-07-21 141608] "SunJavaUpdateSched"="c:\program files\Common Files\Java\Java Update\jusched.exe" [2010-05-14 248552] "Flashget"="c:\program files\FlashGet\flashget.exe" [2007-09-25 2007088] . [HKEY_USERS\.DEFAULT\Software\Microsoft\Windows\CurrentVersion\Run] "CTFMON.EXE"="c:\windows\system32\CTFMON.EXE" [2008-04-14 15360] . c:\documents and settings\Administrator\Start Menu\Programs\Startup\ Adobe Gamma.lnk - c:\program files\Common Files\Adobe\Calibration\Adobe Gamma Loader.exe [2005-3-16 113664] hamachi.lnk - c:\program files\Hamachi\hamachi.exe [2008-12-2 625952] . c:\documents and settings\All Users\Start Menu\Programs\Startup\ Bluetooth.lnk - c:\program files\WIDCOMM\Bluetooth Software\BTTray.exe [2008-5-12 576104] FlexType 2K.lnk - c:\windows\Datecs\Flex2K.exe [2008-9-16 151552] McAfee Security Scan Plus.lnk - c:\program files\McAfee Security Scan\2.0.181\SSScheduler.exe [2010-1-15 255536] . [HKEY_LOCAL_MACHINE\software\microsoft\windows nt\currentversion\winlogon\notify\ackpbsc] 2007-05-15 13:08 112640 ----a-w- c:\windows\system32\ackpbsc.dll . [HKEY_LOCAL_MACHINE\software\microsoft\windows nt\currentversion\winlogon\notify\acunlock] 2007-05-15 13:08 281088 ----a-w- c:\program files\ActivIdentity\ActivClient\acunlock.dll . [HKEY_LOCAL_MACHINE\software\microsoft\windows nt\currentversion\winlogon\notify\OneCard] 2008-06-02 09:06 112400 ----a-w- c:\program files\Hewlett-Packard\IAM\Bin\ASWLNPkg.dll . [HKEY_LOCAL_MACHINE\software\microsoft\windows nt\currentversion\windows] "AppInit_DLLs"=c:\windows\system32\APSHook.dll . [HKEY_LOCAL_MACHINE\SYSTEM\CurrentControlSet\Control\SafeBoot\Minimal\Wdf01000.sys] @="Driver" . [HKLM\~\startupfolder\C:^DOCUME~1^ALLUSE~1^Start Menu^Programs^Startup^DVD Check.lnk] path=c:\docume~1\ALLUSE~1\Start Menu\Programs\Startup\DVD Check.lnk backup=c:\windows\pss\DVD Check.lnkCommon Startup . [HKEY_LOCAL_MACHINE\software\microsoft\shared tools\msconfig\startupreg\Adobe Reader Speed Launcher] c:\program files\Adobe\Reader 8.0\Reader\Reader_sl.exe [N/A] . [HKEY_LOCAL_MACHINE\software\microsoft\shared tools\msconfig\startupreg\Skype] 2008-02-01 15:22 21898024 ----a-r- c:\program files\Skype\Phone\Skype.exe . [HKEY_LOCAL_MACHINE\software\microsoft\shared tools\msconfig\startupreg\WinampAgent] c:\program files\Winamp\winampa.exe [N/A] . [HKEY_LOCAL_MACHINE\software\microsoft\security center] "AntiVirusOverride"=dword:00000001 . [HKLM\~\services\sharedaccess\parameters\firewallpolicy\standardprofile\AuthorizedApplications\List] "%windir%\\Network Diagnostic\\xpnetdiag.exe"= "%windir%\\system32\\sessmgr.exe"= "c:\\Program Files\\FlashGet\\flashget.exe"= "d:\\Programs\\StrongDC++\\StrongDC.exe"= "d:\\Games\\CS\\hl.exe"= "d:\\Programs\\uTorrent\\uTorrent.exe"= "c:\\WINDOWS\\system32\\PnkBstrA.exe"= "c:\\WINDOWS\\system32\\PnkBstrB.exe"= "c:\\Program Files\\Skype\\Plugin Manager\\skypePM.exe"= "c:\\Program Files\\QuickTime\\QuickTimePlayer.exe"= "c:\\Program Files\\Bonjour\\mDNSResponder.exe"= "d:\\Programs\\iTunes\\iTunes.exe"= "c:\\Program Files\\TeamViewer\\Version6\\TeamViewer.exe"= "c:\\Program Files\\TeamViewer\\Version6\\TeamViewer_Service.exe"= "d:\\Programs\\TeamViewer\\Version4\\TeamViewer.exe"= "c:\\Program Files\\Skype\\Phone\\Skype.exe"= . [HKLM\~\services\sharedaccess\parameters\firewallpolicy\standardprofile\GloballyOpenPorts\List] "14265:TCP"= 14265:TCP:BitComet 14265 TCP "14265:UDP"= 14265:UDP:BitComet 14265 UDP . R0 ahcix86;ahcix86;c:\windows\system32\drivers\ahcix86.sys [17.9.2008 і. 01:11 174600] R0 Amddfltr;Amd Disk Lower Filter Driver;c:\windows\system32\drivers\Amddfltr.sys [16.9.2008 і. 20:51 15416] R0 PCTCore;PCTools KDS;c:\windows\system32\drivers\PCTCore.sys [13.4.2011 і. 20:23 239168] R0 pctDS;PC Tools Data Store;c:\windows\system32\drivers\pctDS.sys [13.4.2011 і. 20:23 338880] R0 pctEFA;PC Tools Extended File Attributes;c:\windows\system32\drivers\pctEFA.sys [13.4.2011 і. 20:23 656320] R0 SafeBoot;SafeBoot;c:\windows\system32\drivers\SafeBoot.sys [05.6.2008 і. 17:08 109184] R0 SbAlg;SbAlg;c:\windows\system32\drivers\SbAlg.sys [05.6.2008 і. 17:08 51376] R0 SbFsLock;SbFsLock;c:\windows\system32\drivers\SbFsLock.sys [05.6.2008 і. 17:08 12928] R0 SFAUDIO;Sonic Focus DSP Driver;c:\windows\system32\drivers\sfaudio.sys [28.3.2008 і. 10:14 24064] R1 RsvLock;RsvLock;c:\windows\system32\drivers\rsvlock.sys [05.6.2008 і. 17:08 12496] R2 accoca;ActivClient Middleware Service;c:\program files\ActivIdentity\ActivClient\accoca.exe [15.5.2007 і. 16:08 182576] R2 ASBroker;Logon Session Broker;c:\windows\System32\svchost.exe -k Cognizance [14.4.2008 і. 15:00 14336] R2 ASChannel;Local Communication Channel;c:\windows\System32\svchost.exe -k Cognizance [14.4.2008 і. 15:00 14336] R2 HP ProtectTools Service;HP ProtectTools Service;c:\program files\Hewlett-Packard\HP ProtectTools Security Manager\PTChangeFilterService.exe [10.6.2008 і. 11:13 18944] R2 HpFkCryptService;Drive Encryption Service;c:\program files\Hewlett-Packard\Drive Encryption\HpFkCrypt.exe [05.6.2008 і. 17:07 256512] R2 McAfee SiteAdvisor Service;McAfee SiteAdvisor Service;c:\progra~1\mcafee\SITEAD~1\mcsacore.exe [05.1.2011 і. 15:58 88176] R3 Com4QLBEx;Com4QLBEx;c:\program files\Hewlett-Packard\HP Quick Launch Buttons\Com4QLBEx.exe [16.9.2008 і. 21:09 193840] R3 teamviewervpn;TeamViewer VPN Adapter;c:\windows\system32\drivers\teamviewervpn.sys [25.1.2008 і. 12:12 25088] S2 clr_optimization_v4.0.30319_32;Microsoft .NET Framework NGEN v4.0.30319_X86;c:\windows\Microsoft.NET\Framework\v4.0.30319\mscorsvw.exe [18.3.2010 і. 14:16 130384] S3 McComponentHostService;McAfee Security Scan Component Host Service;c:\program files\McAfee Security Scan\2.0.181\McCHSvc.exe [15.1.2010 і. 15:49 227232] S3 SCR3XX2K;SCR3xx USB SmartCardReader;c:\windows\system32\drivers\SCR3XX2K.sys [21.6.2007 і. 04:40 56448] S3 sdAuxService;PC Tools Auxiliary Service;c:\program files\PC Tools Security\pctsAuxs.exe [13.4.2011 і. 20:23 366840] S3 WPFFontCache_v0400;Windows Presentation Foundation Font Cache 4.0.0.0;c:\windows\Microsoft.NET\Framework\v4.0.30319\WPF\WPFFontCache_v0400.exe [18.3.2010 і. 14:16 753504] S4 sptd;sptd;c:\windows\system32\drivers\sptd.sys [16.9.2008 і. 21:27 685816] . [HKEY_LOCAL_MACHINE\software\microsoft\windows nt\currentversion\svchost] HPZ12 REG_MULTI_SZ Pml Driver HPZ12 Net Driver HPZ12 Cognizance REG_MULTI_SZ ASBroker ASChannel . Contents of the 'Scheduled Tasks' folder . 2011-04-12 c:\windows\Tasks\AppleSoftwareUpdate.job - c:\program files\Apple Software Update\SoftwareUpdate.exe [2009-10-22 08:50] . 2010-06-07 c:\windows\Tasks\expressripShakeIcon.job - c:\program files\NCH Swift Sound\ExpressRip\expressrip.exe [2010-05-28 06:05] . 2011-04-14 c:\windows\Tasks\User_Feed_Synchronization-{723CA83C-C32A-448C-9FE6-94BF21620942}.job - c:\windows\system32\msfeedssync.exe [2009-03-08 02:31] . . ------- Supplementary Scan ------- . uStart Page = hxxp://search.conduit.com?SearchSource=10&ctid=CT2405280 uInternet Connection Wizard,ShellNext = iexplore uInternet Settings,ProxyOverride = *.local uSearchURL,(Default) = hxxp://toolbar.ask.com/toolbarv/askRedirect?o=101699&gct=&gc=1&q=%s IE: &Download All using 4shared Desktop - d:\programs\4shared Desktop\down_all.htm IE: &Download All with FlashGet - c:\program files\FlashGet\jc_all.htm IE: &Download with FlashGet - c:\program files\FlashGet\jc_link.htm IE: Add to Google Photos Screensa&ver - c:\windows\system32\GPhotos.scr/200 IE: E&xport to Microsoft Excel - c:\progra~1\MICROS~2\OFFICE11\EXCEL.EXE/3000 IE: Send to &Bluetooth Device... - c:\program files\WIDCOMM\Bluetooth Software\btsendto_ie_ctx.htm IE: Send To Bluetooth - c:\program files\WIDCOMM\Bluetooth Software\btsendto_ie.htm LSP: c:\program files\Common Files\PC Tools\Lsp\PCTLsp.dll TCP: {9B2D9B85-5FF1-4AE4-AD0F-97B50F0AD220} = 212.39.90.42,212.39.90.43 DPF: Microsoft XML Parser for Java - file://c:\windows\Java\classes\xmldso.cab FF - ProfilePath - c:\documents and settings\Administrator\Application Data\Mozilla\Firefox\Profiles\korvvd8g.default\ FF - prefs.js: browser.search.defaulturl - hxxp://search.conduit.com/ResultsExt.aspx?ctid=CT2405280&SearchSource=3&q={searchTerms} FF - prefs.js: browser.search.selectedEngine - Secure Search FF - prefs.js: browser.startup.homepage - google.bg FF - prefs.js: keyword.URL - hxxp://search.yahoo.com/search?fr=mcafee&p= FF - prefs.js: network.proxy.type - 4 . - - - - ORPHANS REMOVED - - - - . AddRemove-HijackThis - c:\program files\HiJackThis\HijackThis.exe AddRemove-mIRC - d:\programs\VipScript\mirc.exe AddRemove-The Wizard's Pen 1.01 - d:\games\WizardsPen\The Wizard's Pen\PopUninstall.exe . . . ************************************************************************** . catchme 0.3.1398 W2K/XP/Vista - rootkit/stealth malware detector by Gmer, http://www.gmer.net Rootkit scan 2011-04-14 21:57 Windows 5.1.2600 Service Pack 3 NTFS . scanning hidden processes ... . scanning hidden autostart entries ... . scanning hidden files ... . scan completed successfully hidden files: 0 . ************************************************************************** . --------------------- LOCKED REGISTRY KEYS --------------------- . [HKEY_USERS\S-1-5-21-1957994488-1275210071-1177238915-500\Software\Microsoft\Internet Explorer\User Preferences] @Denied: (2) (Administrator) "88D7D0879DAB32E14DE5B3A805A34F98AFF34F5977"=hex:01,00,00,00,d0,8c,9d,df,01,15, d1,11,8c,7a,00,c0,4f,c2,97,eb,01,00,00,00,37,2b,75,ec,20,51,f1,48,a2,a3,62,\ "2D53CFFC5C1A3DD2E97B7979AC2A92BD59BC839E81"=hex:01,00,00,00,d0,8c,9d,df,01,15, d1,11,8c,7a,00,c0,4f,c2,97,eb,01,00,00,00,95,eb,97,81,98,92,25,49,82,81,83,\ "6256FFB019F8FDFBD36745B06F4540E9AEAF222A25"=hex:01,00,00,00,d0,8c,9d,df,01,15, d1,11,8c,7a,00,c0,4f,c2,97,eb,01,00,00,00,37,2b,75,ec,20,51,f1,48,a2,a3,62,\ . --------------------- DLLs Loaded Under Running Processes --------------------- . - - - - - - - > 'winlogon.exe'(1260) c:\windows\system32\ackpbsc.dll c:\windows\system32\aclog.dll c:\windows\system32\ACLIBEAY.dll c:\windows\system32\acevtsub.dll c:\windows\system32\asphat32.dll c:\windows\system32\acerrmes.dll c:\windows\system32\aspcom.dll c:\program files\ActivIdentity\ActivClient\Resources\Merged\acerrmrc.dll c:\program files\ActivIdentity\ActivClient\Resources\Merged\asphatrc.dll c:\windows\system32\msi.dll c:\windows\system32\Ati2evxx.dll c:\program files\Hewlett-Packard\IAM\Bin\ASWLNPkg.dll c:\program files\Hewlett-Packard\IAM\bin\ItMsg.dll c:\program files\Hewlett-Packard\IAM\Bin\TrayIcon.dll c:\program files\Hewlett-Packard\IAM\bin\brand.dll c:\program files\Hewlett-Packard\IAM\Bin\AsChnl.dll c:\program files\Hewlett-Packard\IAM\Bin\HPPlugIn.dll c:\program files\Hewlett-Packard\HP ProtectTools Security Manager\PTHostServices.dll c:\program files\Hewlett-Packard\HP ProtectTools Security Manager\Interop.HPQWMIEXLib.dll c:\program files\ActivIdentity\ActivClient\acunlock.dll c:\windows\system32\aipingui.dll c:\program files\ActivIdentity\ActivClient\Resources\Merged\aipinguirc.dll c:\program files\ActivIdentity\ActivClient\resources\acCobAPIrc.dll c:\program files\ActivIdentity\ActivClient\Resources\Merged\acunlockrc.dll c:\program files\Hewlett-Packard\HP ProtectTools Security Manager\Interop.PTHstServsLib.dll c:\program files\Hewlett-Packard\HP ProtectTools Security Manager\PTHstServs.dll c:\program files\Hewlett-Packard\HP ProtectTools Security Manager\BIOSDomain.dll c:\program files\Hewlett-Packard\HP ProtectTools Security Manager\Interop.PTPluginLib.dll c:\program files\Hewlett-Packard\HP ProtectTools Security Manager\PTStrings.dll c:\program files\Hewlett-Packard\HP ProtectTools Security Manager\HPjCard.dll c:\windows\system32\acomx.dll c:\windows\system32\acbsi21.dll c:\program files\Hewlett-Packard\IAM\Bin\ItVCClient.dll c:\program files\Hewlett-Packard\IAM\Bin\ItReports.DLL c:\program files\Hewlett-Packard\IAM\Bin\ItVCard.dll c:\program files\Hewlett-Packard\IAM\Bin\NetAdmin.dll . - - - - - - - > 'lsass.exe'(1316) c:\program files\Common Files\PC Tools\Lsp\PCTLsp.dll . - - - - - - - > 'explorer.exe'(9376) c:\windows\system32\WININET.dll c:\program files\FlashGet\fgmgr.dll c:\progra~1\mcafee\SITEAD~1\saHook.dll c:\windows\system32\newdll.dll c:\windows\system32\APSHook.dll c:\windows\system32\webcheck.dll c:\windows\system32\IEFRAME.dll c:\progra~1\COMMON~1\MICROS~1\WEBCOM~1\10\OWC10.DLL c:\windows\system32\Msi.dll c:\program files\Common Files\Microsoft Shared\Web Components\10\1026\OWCI10.DLL c:\progra~1\COMMON~1\MICROS~1\WEBCOM~1\11\OWC11.DLL c:\program files\Common Files\Microsoft Shared\Web Components\11\1026\OWCI11.DLL c:\windows\system32\btmmhook.dll c:\windows\system32\mshtml.dll c:\windows\system32\msls31.dll . ------------------------ Other Running Processes ------------------------ . c:\windows\system32\Ati2evxx.exe c:\program files\WIDCOMM\Bluetooth Software\bin\btwdins.exe c:\windows\System32\SCardSvr.exe c:\program files\ActivIdentity\ActivClient\acevents.exe c:\windows\system32\Ati2evxx.exe c:\program files\Hewlett-Packard\IAM\Bin\AsGHost.exe c:\windows\system32\agrsmsvc.exe c:\program files\Common Files\Apple\Mobile Device Support\AppleMobileDeviceService.exe c:\program files\Bonjour\mDNSResponder.exe c:\program files\Java\jre6\bin\jqs.exe c:\program files\Microsoft SQL Server\MSSQL.1\MSSQL\Binn\sqlservr.exe c:\windows\system32\PnkBstrA.exe c:\program files\Microsoft SQL Server\90\Shared\sqlwriter.exe c:\windows\system32\wdfmgr.exe c:\program files\Hewlett-Packard\Shared\hpqwmiex.exe c:\windows\system32\rundll32.exe c:\progra~1\WIDCOMM\BLUETO~1\BTSTAC~1.EXE c:\program files\ActivIdentity\ActivClient\acevents.exe c:\program files\iPod\bin\iPodService.exe c:\program files\ATI Technologies\ATI.ACE\Core-Static\MOM.exe c:\program files\ATI Technologies\ATI.ACE\Core-Static\ccc.exe . ************************************************************************** . Completion time: 2011-04-14 22:03:49 - machine was rebooted ComboFix-quarantined-files.txt 2011-04-14 19:03 ComboFix2.txt 2009-06-14 17:56 . Pre-Run: 15 386 038 272 bytes free Post-Run: 21 238 546 432 bytes free . WindowsXP-KB310994-SP2-Pro-BootDisk-ENU.exe [boot loader] timeout=2 default=multi(0)disk(0)rdisk(0)partition(1)\WINDOWS [operating systems] c:\cmdcons\BOOTSECT.DAT="Microsoft Windows Recovery Console" /cmdcons UnsupportedDebug="do not select this" /debug multi(0)disk(0)rdisk(0)partition(1)\WINDOWS="Microsoft Windows XP Professional" /noexecute=optin /fastdetect /usepmtimer . - - End Of File - - 1FF10D5BFEBD354BA0F4A82BCADED9FC Обаче C:\BUG.txt няма, няма такъв файл в папката, и с търсачката също не го намирам. Десктопа ми си върна стария вид, няма го вече белия екран с надписа Active Desctop Recovery. Какво следва сега?
-
Не, не, нормални рестарта бяха. След като всяка от трите програми приключваше, искаше рестарт.
-
Три пъти се рестартира общо. Има ли значение това, че не използвам Microsoft Internet Explorer изобщо, а само Мозила. Тя е моя браузър по подразбиране. И не, не е проблем изключването на autorun функцията на всички CD, Floppy и USB устройства. Още тегля ComboFix. След отговора ви ще започна работа с него.
-
С търпение към прогрес! OTL лог: ========== FILES ========== File\Folder c:\windows\system32\msn not found. ========== REGISTRY ========== Registry key HKEY_LOCAL_MACHINE\software\microsoft\active setup\installed components\{ABB0EEF9-CE96-4474-2285-E68550D75C8F}\ not found. Registry key HKEY_LOCAL_MACHINE\SOFTWARE\Classes\CLSID\{ABB0EEF9-CE96-4474-2285-E68550D75C8F}\ not found. ========== COMMANDS ========== OTL by OldTimer - Version 3.2.22.3 log created on 04142011_190004 Malwarebytes' Anti-Malware лог: Malwarebytes' Anti-Malware 1.50.1.1100 www.malwarebytes.org Версия на базата от данни: 6363 Windows 5.1.2600 Service Pack 3 Internet Explorer 8.0.6001.18702 14.4.2011 г. 19:28:04 mbam-log-2011-04-14 (19-28-04).txt Тип сканиране: Бързо сканиране Сканирани обекти: 160738 Изминало време: 17 минута(и), 30 секунда(и) Заразени процеси в паметта: 0 Заразени модули в паметта: 0 Заразени ключове в регистратурата: 2 Заразени стойности в регистратурата: 0 Заразени информационни обекти в регистратурата: 0 Заразени папки: 6 Заразени файлове: 5 Заразени процеси в паметта: (Не бяха открити зловредни обекти) Заразени модули в паметта: (Не бяха открити зловредни обекти) Заразени ключове в регистратурата: HKEY_LOCAL_MACHINE\Software\Wyeke (Adware.Agent) -> Quarantined and deleted successfully. HKEY_LOCAL_MACHINE\Software\Microsoft\Windows\CurrentVersion\Uninstall\Wyeke (Adware.Agent) -> Quarantined and deleted successfully. Заразени стойности в регистратурата: (Не бяха открити зловредни обекти) Заразени информационни обекти в регистратурата: (Не бяха открити зловредни обекти) Заразени папки: c:\program files\Wyeke (Adware.Agent) -> Quarantined and deleted successfully. c:\documents and settings\all users\application data\Wyeke (Adware.Wyeke) -> Quarantined and deleted successfully. c:\program files\mozilla firefox\extensions\{4cfc8387-5fb1-47c1-8aa4-5b7b906a591e} (Adware.Wyeke) -> Quarantined and deleted successfully. c:\program files\mozilla firefox\extensions\{4cfc8387-5fb1-47c1-8aa4-5b7b906a591e}\chrome (Adware.Wyeke) -> Quarantined and deleted successfully. c:\program files\mozilla firefox\extensions\{4cfc8387-5fb1-47c1-8aa4-5b7b906a591e}\defaults (Adware.Wyeke) -> Quarantined and deleted successfully. c:\program files\mozilla firefox\extensions\{4cfc8387-5fb1-47c1-8aa4-5b7b906a591e}\defaults\preferences (Adware.Wyeke) -> Quarantined and deleted successfully. Заразени файлове: c:\program files\Wyeke\uninstall.exe (Adware.Agent) -> Quarantined and deleted successfully. c:\program files\mozilla firefox\extensions\{4cfc8387-5fb1-47c1-8aa4-5b7b906a591e}\chrome.manifest (Adware.Wyeke) -> Quarantined and deleted successfully. c:\program files\mozilla firefox\extensions\{4cfc8387-5fb1-47c1-8aa4-5b7b906a591e}\install.rdf (Adware.Wyeke) -> Quarantined and deleted successfully. c:\program files\mozilla firefox\extensions\{4cfc8387-5fb1-47c1-8aa4-5b7b906a591e}\chrome\wyeke.jar (Adware.Wyeke) -> Quarantined and deleted successfully. c:\program files\mozilla firefox\extensions\{4cfc8387-5fb1-47c1-8aa4-5b7b906a591e}\defaults\preferences\prefs.js (Adware.Wyeke) -> Quarantined and deleted successfully. Това е. След края на всяка програма, компютъра се рестартираше.
-
От няколко дни лаптопа ми започна да се изключва сам в бял или черен екран, най-често докато сърфирам с Мозила. А от днес ми се появи белия екран с Active Desktop Recovery. До две седмици ще сложа Windows 7 и предполагам (тъй като сканирах със Spyware Doctor и отчете доста грешки които не можах да изчистя, защото не намерих лицензирана версия), че всичко ще е напълно обновено и чисто, но до тогава не искам да мъча системата и да изникнат още проблеми. Attach: . UNLESS SPECIFICALLY INSTRUCTED, DO NOT POST THIS LOG. IF REQUESTED, ZIP IT UP & ATTACH IT . DDS (Ver_11-03-05.01) . Microsoft Windows XP Professional Boot Device: \Device\HarddiskVolume1 Install Date: 16.9.2008 г. 20:40:34 System Uptime: 14.4.2011 г. 00:14:34 (0 hours ago) . Motherboard: Hewlett-Packard | | 30E4 Processor: AMD AthlonX2 DualCore QL-60 | Unknown | 1900/200mhz . ==== Disk Partitions ========================= . C: is FIXED (NTFS) - 39 GiB total, 15,213 GiB free. D: is FIXED (NTFS) - 98 GiB total, 20,046 GiB free. E: is FIXED (NTFS) - 96 GiB total, 10,489 GiB free. F: is CDROM () G: is CDROM () H: is CDROM () I: is CDROM () J: is CDROM () . ==== Disabled Device Manager Items ============= . ==== System Restore Points =================== . RP494: 27.2.2011 г. 18:30:31 - Контролна точка на системата RP495: 28.2.2011 г. 18:34:22 - Контролна точка на системата RP496: 01.3.2011 г. 21:14:30 - Контролна точка на системата RP497: 03.3.2011 г. 01:50:40 - Контролна точка на системата RP498: 04.3.2011 г. 02:30:27 - Контролна точка на системата RP499: 05.3.2011 г. 04:16:05 - Контролна точка на системата RP500: 06.3.2011 г. 04:42:04 - Контролна точка на системата RP501: 07.3.2011 г. 10:28:01 - Контролна точка на системата RP502: 08.3.2011 г. 11:02:51 - Контролна точка на системата RP503: 09.3.2011 г. 12:42:22 - Контролна точка на системата RP504: 09.3.2011 г. 23:50:19 - Software Distribution Service 3.0 RP505: 11.3.2011 г. 13:31:20 - Контролна точка на системата RP506: 12.3.2011 г. 13:37:27 - Контролна точка на системата RP507: 13.3.2011 г. 14:09:17 - Контролна точка на системата RP508: 14.3.2011 г. 19:55:52 - Контролна точка на системата RP509: 15.3.2011 г. 20:41:51 - Контролна точка на системата RP510: 16.3.2011 г. 21:40:53 - Контролна точка на системата RP511: 17.3.2011 г. 21:59:16 - Контролна точка на системата RP512: 19.3.2011 г. 00:03:48 - Контролна точка на системата RP513: 20.3.2011 г. 10:42:27 - Контролна точка на системата RP514: 21.3.2011 г. 11:59:44 - Контролна точка на системата RP515: 22.3.2011 г. 13:59:42 - Контролна точка на системата RP516: 23.3.2011 г. 14:02:20 - Контролна точка на системата RP517: 24.3.2011 г. 20:08:19 - Контролна точка на системата RP518: 25.3.2011 г. 03:00:18 - Software Distribution Service 3.0 RP519: 26.3.2011 г. 03:31:26 - Контролна точка на системата RP520: 27.3.2011 г. 03:34:48 - Контролна точка на системата RP521: 28.3.2011 г. 05:21:17 - Контролна точка на системата RP522: 29.3.2011 г. 05:21:31 - Контролна точка на системата RP523: 30.3.2011 г. 15:32:25 - Removed Syberia RP524: 30.3.2011 г. 18:59:16 - ClearAnswersPanel RP525: 31.3.2011 г. 20:09:27 - Контролна точка на системата RP526: 02.4.2011 г. 14:12:48 - Контролна точка на системата RP527: 03.4.2011 г. 14:49:53 - Контролна точка на системата RP528: 04.4.2011 г. 17:15:46 - Контролна точка на системата RP529: 05.4.2011 г. 18:30:37 - Контролна точка на системата RP530: 06.4.2011 г. 19:00:44 - Контролна точка на системата RP531: 08.4.2011 г. 01:35:32 - Контролна точка на системата RP532: 09.4.2011 г. 03:07:05 - Контролна точка на системата RP533: 10.4.2011 г. 03:44:20 - Контролна точка на системата RP534: 11.4.2011 г. 20:39:49 - Контролна точка на системата RP535: 13.4.2011 г. 11:54:33 - Контролна точка на системата RP536: 13.4.2011 г. 20:10:49 - Installed Driver Detective. RP537: 13.4.2011 г. 20:18:51 - Removed ESET NOD32 Antivirus RP538: 13.4.2011 г. 20:19:23 - Removed ESET NOD32 Antivirus RP539: 13.4.2011 г. 23:51:32 - Installed %1 %2. . ==== Installed Programs ====================== . П°єµт ·° съІјµстёјѕст ·° сёстµј°т° Office 2007 32 Bit HP CIO Components Installer ActivClient 6.1 x86 Adobe Bridge 1.0 Adobe Common File Installer Adobe Flash Player 10 Plugin Adobe Flash Player ActiveX Adobe Help Center 2.0 Adobe Premiere Pro 2.0 Adobe Stock Photos 1.0 AGEIA PhysX v7.07.24 Agere Systems HDA Modem AMD Driver Support for HP 3D DriverGuard AMD Processor Driver Apple Application Support Apple Mobile Device Support Apple Software Update ATI Catalyst Control Center ATI Display Driver Bonjour Broadcom 802.11 Wireless LAN Adapter BS.Player FREE powered by AdVantage BSPlayer Catalyst Control Center - Branding Catalyst Control Center Core Implementation Catalyst Control Center Graphics Full Existing Catalyst Control Center Graphics Full New Catalyst Control Center Graphics Light Catalyst Control Center Localization Chinese Standard Catalyst Control Center Localization Chinese Traditional Catalyst Control Center Localization Czech Catalyst Control Center Localization Danish Catalyst Control Center Localization Dutch Catalyst Control Center Localization Finnish Catalyst Control Center Localization French Catalyst Control Center Localization German Catalyst Control Center Localization Greek Catalyst Control Center Localization Hungarian Catalyst Control Center Localization Italian Catalyst Control Center Localization Japanese Catalyst Control Center Localization Korean Catalyst Control Center Localization Norwegian Catalyst Control Center Localization Polish Catalyst Control Center Localization Portuguese Catalyst Control Center Localization Russian Catalyst Control Center Localization Spanish Catalyst Control Center Localization Swedish Catalyst Control Center Localization Thai Catalyst Control Center Localization Turkish ccc-core-preinstall ccc-core-static ccc-utility CCC Help Chinese Standard CCC Help Chinese Traditional CCC Help Czech CCC Help Danish CCC Help Dutch CCC Help English CCC Help Finnish CCC Help French CCC Help German CCC Help Greek CCC Help Hungarian CCC Help Italian CCC Help Japanese CCC Help Korean CCC Help Norwegian CCC Help Polish CCC Help Portuguese CCC Help Russian CCC Help Spanish CCC Help Swedish CCC Help Thai CCC Help Turkish Counter-Strike 1.6 Credential Manager for HP ProtectTools Crystal Reports Basic for Visual Studio 2008 Drive Encryption for HP ProtectTools Driver Detective Dynomite Deluxe 2.71 Express Rip FlashGet 1.9.6.1073 FlexType 2K FormatFactory 2.60 Foxit Reader Foxit Toolbar Hamachi 1.0.3.0 HijackThis 2.0.2 Hotfix for Microsoft .NET Framework 3.5 SP1 (KB953595) Hotfix for Microsoft .NET Framework 3.5 SP1 (KB958484) Hotfix for Windows XP (KB2158563) Hotfix for Windows XP (KB2443685) Hotfix for Windows XP (KB942288-v3) Hotfix for Windows XP (KB952287) Hotfix for Windows XP (KB954550-v5) Hotfix for Windows XP (KB958655-v2) Hotfix for Windows XP (KB961118) Hotfix for Windows XP (KB970653-v3) Hotfix for Windows XP (KB976002-v5) Hotfix for Windows XP (KB976098-v2) Hotfix for Windows XP (KB979306) Hotfix for Windows XP (KB981793) HP 3D DriveGuard HP Integrated Module with Bluetooth wireless technology HP JavaCard for HP ProtectTools HP ProtectTools Security Manager HP ProtectTools Security Manager Suite HP Quick Launch Buttons 6.40 F1 HP Webcam HP Webcam Application HP Wireless Assistant Image Resizer Powertoy for Windows XP iTunes Java Auto Updater Java 6 Update 21 K-Lite Codec Pack 3.8.5 Full Last.fm 1.5.4.24567 Malwarebytes' Anti-Malware Marvell Miniport Driver McAfee Security Scan Plus McAfee SiteAdvisor Microsoft .NET Compact Framework 2.0 SP2 Microsoft .NET Compact Framework 3.5 Microsoft .NET Framework 2.0 Service Pack 2 Microsoft .NET Framework 3.0 Service Pack 2 Microsoft .NET Framework 3.5 SP1 Microsoft .NET Framework 4 Client Profile Microsoft .NET Framework 4 Extended Microsoft Application Error Reporting Microsoft Device Emulator version 3.0 - ENU Microsoft Document Explorer 2008 Microsoft Kernel-Mode Driver Framework Feature Pack 1.5 Microsoft Office 2003 Bulgarian User Interface Pack Microsoft Office Professional Edition 2003 Microsoft SQL Server 2005 Microsoft SQL Server 2005 Express Edition (SQLEXPRESS) Microsoft SQL Server 2005 Tools Express Edition Microsoft SQL Server Compact 3.5 Design Tools ENU Microsoft SQL Server Compact 3.5 ENU Microsoft SQL Server Compact 3.5 for Devices ENU Microsoft SQL Server Database Publishing Wizard 1.2 Microsoft SQL Server Native Client Microsoft SQL Server Setup Support Files (English) Microsoft SQL Server VSS Writer Microsoft Visual C++ 2005 Redistributable Microsoft Visual C++ 2008 Redistributable - x86 9.0.30729.17 Microsoft Visual C++ 2008 Redistributable - x86 9.0.30729.4974 Microsoft Visual C++ 2010 x86 Runtime - 10.0.30319 Microsoft Visual Studio 2005 Tools for Office Runtime Microsoft Windows SDK for Visual Studio 2008 .NET Framework Tools Microsoft Windows SDK for Visual Studio 2008 Headers and Libraries Microsoft Windows SDK for Visual Studio 2008 SDK Reference Assemblies and IntelliSense Microsoft Windows SDK for Visual Studio 2008 Tools Microsoft Windows SDK for Visual Studio 2008 Win32 Tools Microsoft WSE 3.0 Runtime mIRC Mozilla Firefox 4.0 (x86 bg) MP3 To Ringtone Gold 5.80 MSXML 4.0 SP2 (KB954430) MSXML 4.0 SP2 (KB973688) MSXML 6.0 Parser Mystery P.I. - The Lottery Ticket 1.0.0.5 NCH Toolbox Nero 8 Lite 8.3.2.1 NOD32 v3.x FiX 1.1 by TemDono (Free Updates - Expire in 2050) OpenAL Picasa 3 PunkBuster Services QuickTime SA Dictionary 2005 T2 SCR3xxx Smart Card Reader Security Update for Microsoft .NET Framework 3.5 SP1 (KB2416473) Security Update for Microsoft .NET Framework 4 Extended (KB2416472) Security Update for Windows Internet Explorer 8 (KB2183461) Security Update for Windows Internet Explorer 8 (KB2360131) Security Update for Windows Internet Explorer 8 (KB2416400) Security Update for Windows Internet Explorer 8 (KB2482017) Security Update for Windows Internet Explorer 8 (KB971961) Security Update for Windows Internet Explorer 8 (KB974455) Security Update for Windows Internet Explorer 8 (KB976325) Security Update for Windows Internet Explorer 8 (KB978207) Security Update for Windows Internet Explorer 8 (KB981332) Security Update for Windows Internet Explorer 8 (KB982381) Security Update for Windows Media Player (KB2378111) Security Update for Windows Media Player (KB952069) Security Update for Windows Media Player (KB954155) Security Update for Windows Media Player (KB968816) Security Update for Windows Media Player (KB973540) Security Update for Windows Media Player (KB975558) Security Update for Windows Media Player (KB978695) Security Update for Windows Media Player (KB979402) Security Update for Windows XP (KB2079403) Security Update for Windows XP (KB2115168) Security Update for Windows XP (KB2121546) Security Update for Windows XP (KB2160329) Security Update for Windows XP (KB2229593) Security Update for Windows XP (KB2259922) Security Update for Windows XP (KB2279986) Security Update for Windows XP (KB2286198) Security Update for Windows XP (KB2296011) Security Update for Windows XP (KB2296199) Security Update for Windows XP (KB2347290) Security Update for Windows XP (KB2360937) Security Update for Windows XP (KB2387149) Security Update for Windows XP (KB2393802) Security Update for Windows XP (KB2419632) Security Update for Windows XP (KB2423089) Security Update for Windows XP (KB2436673) Security Update for Windows XP (KB2440591) Security Update for Windows XP (KB2443105) Security Update for Windows XP (KB2476687) Security Update for Windows XP (KB2478960) Security Update for Windows XP (KB2478971) Security Update for Windows XP (KB2479628) Security Update for Windows XP (KB2479943) Security Update for Windows XP (KB2481109) Security Update for Windows XP (KB2483185) Security Update for Windows XP (KB2485376) Security Update for Windows XP (KB2524375) Security Update for Windows XP (KB923561) Security Update for Windows XP (KB938464-v2) Security Update for Windows XP (KB941569) Security Update for Windows XP (KB946648) Security Update for Windows XP (KB950760) Security Update for Windows XP (KB950762) Security Update for Windows XP (KB950974) Security Update for Windows XP (KB951066) Security Update for Windows XP (KB951376-v2) Security Update for Windows XP (KB951748) Security Update for Windows XP (KB952004) Security Update for Windows XP (KB952954) Security Update for Windows XP (KB954459) Security Update for Windows XP (KB954600) Security Update for Windows XP (KB955069) Security Update for Windows XP (KB956572) Security Update for Windows XP (KB956744) Security Update for Windows XP (KB956802) Security Update for Windows XP (KB956803) Security Update for Windows XP (KB956844) Security Update for Windows XP (KB957097) Security Update for Windows XP (KB958644) Security Update for Windows XP (KB958687) Security Update for Windows XP (KB958690) Security Update for Windows XP (KB958869) Security Update for Windows XP (KB959426) Security Update for Windows XP (KB960225) Security Update for Windows XP (KB960715) Security Update for Windows XP (KB960803) Security Update for Windows XP (KB960859) Security Update for Windows XP (KB961371) Security Update for Windows XP (KB961373) Security Update for Windows XP (KB961501) Security Update for Windows XP (KB963027) Security Update for Windows XP (KB968537) Security Update for Windows XP (KB969059) Security Update for Windows XP (KB969897) Security Update for Windows XP (KB969898) Security Update for Windows XP (KB969947) Security Update for Windows XP (KB970238) Security Update for Windows XP (KB970430) Security Update for Windows XP (KB971468) Security Update for Windows XP (KB971486) Security Update for Windows XP (KB971557) Security Update for Windows XP (KB971633) Security Update for Windows XP (KB971657) Security Update for Windows XP (KB971961) Security Update for Windows XP (KB972260) Security Update for Windows XP (KB972270) Security Update for Windows XP (KB973346) Security Update for Windows XP (KB973354) Security Update for Windows XP (KB973507) Security Update for Windows XP (KB973525) Security Update for Windows XP (KB973869) Security Update for Windows XP (KB973904) Security Update for Windows XP (KB974112) Security Update for Windows XP (KB974318) Security Update for Windows XP (KB974392) Security Update for Windows XP (KB974455) Security Update for Windows XP (KB974571) Security Update for Windows XP (KB975025) Security Update for Windows XP (KB975467) Security Update for Windows XP (KB975560) Security Update for Windows XP (KB975561) Security Update for Windows XP (KB975562) Security Update for Windows XP (KB975713) Security Update for Windows XP (KB977165) Security Update for Windows XP (KB977816) Security Update for Windows XP (KB977914) Security Update for Windows XP (KB978037) Security Update for Windows XP (KB978251) Security Update for Windows XP (KB978262) Security Update for Windows XP (KB978338) Security Update for Windows XP (KB978542) Security Update for Windows XP (KB978601) Security Update for Windows XP (KB978706) Security Update for Windows XP (KB979309) Security Update for Windows XP (KB979482) Security Update for Windows XP (KB979559) Security Update for Windows XP (KB979683) Security Update for Windows XP (KB979687) Security Update for Windows XP (KB980195) Security Update for Windows XP (KB980218) Security Update for Windows XP (KB980232) Security Update for Windows XP (KB980436) Security Update for Windows XP (KB981322) Security Update for Windows XP (KB981852) Security Update for Windows XP (KB981957) Security Update for Windows XP (KB981997) Security Update for Windows XP (KB982132) Security Update for Windows XP (KB982214) Security Update for Windows XP (KB982665) Security Update for Windows XP (KB982802) Skins Skype™ 3.6 Softonic-Eng7 Toolbar SoundMAX Spybot - Search & Destroy Spyware Doctor 8.0 StrongDC Synaptics Pointing Device Driver TeamViewer 4 TeamViewer 6 The KMPlayer (remove only) The Wizard's Pen 1.01 Update for Microsoft .NET Framework 3.5 SP1 (KB963707) Update for Microsoft .NET Framework 4 Client Profile (KB2473228) Update for Windows Internet Explorer 8 (KB975364) Update for Windows Internet Explorer 8 (KB976662) Update for Windows Internet Explorer 8 (KB976749) Update for Windows Internet Explorer 8 (KB980182) Update for Windows XP (KB2141007) Update for Windows XP (KB2345886) Update for Windows XP (KB2467659) Update for Windows XP (KB898461) Update for Windows XP (KB951978) Update for Windows XP (KB955759) Update for Windows XP (KB955839) Update for Windows XP (KB967715) Update for Windows XP (KB968389) Update for Windows XP (KB971029) Update for Windows XP (KB971737) Update for Windows XP (KB973687) Update for Windows XP (KB973815) Update for Windows XP (KB976749) V8400 Digital Camera Driver Visual Studio Tools for the Office system 3.0 Runtime VLC media player 1.0.5 WavePad Sound Editor WebFldrs XP Winamp Windows Bulgarian Interface Pack Windows Feature Pack for Storage (32-bit) - IMAPI update for Blu-Ray Windows Genuine Advantage Notifications (KB905474) Windows Internet Explorer 8 Windows Media Format Runtime Windows Mobile 5.0 SDK R2 for Pocket PC Windows Mobile 5.0 SDK R2 for Smartphone Windows PowerShell 1.0 Wyeke 1.0 build 137 ррхёІ°тѕр WinRAR µTorrent . ==== Event Viewer Messages From Past Week ======== . 14.4.2011 і. 00:19:00, error: Service Control Manager [7034] - The HP ProtectTools Service service terminated unexpectedly. It has done this 1 time(s). 14.4.2011 і. 00:18:05, error: Service Control Manager [7034] - The McAfee SiteAdvisor Service service terminated unexpectedly. It has done this 1 time(s). 14.4.2011 і. 00:18:05, error: Service Control Manager [7022] - The McAfee SiteAdvisor Service service hung on starting. 14.4.2011 і. 00:16:13, error: Service Control Manager [7023] - The Logical Disk Manager service terminated with the following error: The specified module could not be found. 13.4.2011 і. 22:53:59, error: Service Control Manager [7023] - The Logical Disk Manager service terminated with the following error: The specified module could not be found. 13.4.2011 і. 20:21:41, error: Service Control Manager [7023] - The Logical Disk Manager service terminated with the following error: The specified module could not be found. 13.4.2011 і. 19:58:00, error: Service Control Manager [7023] - The Logical Disk Manager service terminated with the following error: The specified module could not be found. 13.4.2011 і. 19:31:55, error: Service Control Manager [7011] - Timeout (30000 milliseconds) waiting for a transaction response from the Bonjour Service service. 13.4.2011 і. 19:31:54, error: Service Control Manager [7011] - Timeout (30000 milliseconds) waiting for a transaction response from the Schedule service. 13.4.2011 і. 19:31:54, error: Service Control Manager [7011] - Timeout (30000 milliseconds) waiting for a transaction response from the HpFkCryptService service. 13.4.2011 і. 16:08:54, error: Service Control Manager [7023] - The Logical Disk Manager service terminated with the following error: The specified module could not be found. 13.4.2011 і. 14:27:12, error: Service Control Manager [7023] - The Logical Disk Manager service terminated with the following error: The specified module could not be found. 13.4.2011 і. 14:26:59, error: ati2mtag [2] - Unable to map required address ranges for graphics card. 13.4.2011 і. 10:40:39, error: Service Control Manager [7023] - The Logical Disk Manager service terminated with the following error: The specified module could not be found. 13.4.2011 і. 10:21:01, error: Service Control Manager [7023] - The Logical Disk Manager service terminated with the following error: The specified module could not be found. 13.4.2011 і. 10:07:35, error: Service Control Manager [7023] - The Logical Disk Manager service terminated with the following error: The specified module could not be found. 13.4.2011 і. 09:55:25, error: Service Control Manager [7023] - The Logical Disk Manager service terminated with the following error: The specified module could not be found. 13.4.2011 і. 09:36:38, error: Service Control Manager [7023] - The Logical Disk Manager service terminated with the following error: The specified module could not be found. 13.4.2011 і. 00:27:19, error: Service Control Manager [7034] - The McAfee SiteAdvisor Service service terminated unexpectedly. It has done this 1 time(s). 13.4.2011 і. 00:27:19, error: Service Control Manager [7034] - The HP ProtectTools Service service terminated unexpectedly. It has done this 1 time(s). 13.4.2011 і. 00:27:18, error: Service Control Manager [7022] - The McAfee SiteAdvisor Service service hung on starting. 13.4.2011 і. 00:25:31, error: Service Control Manager [7023] - The Logical Disk Manager service terminated with the following error: The specified module could not be found. 13.4.2011 і. 00:24:37, error: NetBT [4307] - Initialization failed because the transport refused to open initial Addresses. 13.4.2011 і. 00:19:58, error: Service Control Manager [7023] - The Logical Disk Manager service terminated with the following error: The specified module could not be found. 13.4.2011 і. 00:19:38, error: ati2mtag [2] - Unable to map required address ranges for graphics card. 12.4.2011 і. 21:24:31, error: Service Control Manager [7023] - The Logical Disk Manager service terminated with the following error: The specified module could not be found. 12.4.2011 і. 20:17:13, error: Service Control Manager [7023] - The Logical Disk Manager service terminated with the following error: The specified module could not be found. 12.4.2011 і. 19:11:13, error: Service Control Manager [7023] - The Logical Disk Manager service terminated with the following error: The specified module could not be found. 12.4.2011 і. 16:36:02, error: Service Control Manager [7023] - The Logical Disk Manager service terminated with the following error: The specified module could not be found. 12.4.2011 і. 16:28:12, error: Service Control Manager [7023] - The Logical Disk Manager service terminated with the following error: The specified module could not be found. 12.4.2011 і. 16:20:29, error: Service Control Manager [7023] - The Logical Disk Manager service terminated with the following error: The specified module could not be found. 12.4.2011 і. 16:20:07, error: Dhcp [1002] - The IP address lease 192.168.1.4 for the Network Card with network address 0021003C9641 has been denied by the DHCP server 192.168.1.1 (The DHCP Server sent a DHCPNACK message). 12.4.2011 і. 09:26:48, error: Dhcp [1001] - Your computer was not assigned an address from the network (by the DHCP Server) for the Network Card with network address 0021003C9641. The following error occurred: The operation was canceled by the user. . Your computer will continue to try and obtain an address on its own from the network address (DHCP) server. 12.4.2011 і. 09:26:43, error: Dhcp [1001] - Your computer was not assigned an address from the network (by the DHCP Server) for the Network Card with network address 0021003C9641. The following error occurred: The operation was canceled by the user. . Your computer will continue to try and obtain an address on its own from the network address (DHCP) server. 12.4.2011 і. 08:49:35, error: Service Control Manager [7023] - The Logical Disk Manager service terminated with the following error: The specified module could not be found. 12.4.2011 і. 07:34:15, error: Service Control Manager [7023] - The Logical Disk Manager service terminated with the following error: The specified module could not be found. 12.4.2011 і. 00:06:16, error: Service Control Manager [7023] - The Logical Disk Manager service terminated with the following error: The specified module could not be found. 11.4.2011 і. 19:17:52, error: Service Control Manager [7023] - The Logical Disk Manager service terminated with the following error: The specified module could not be found. 11.4.2011 і. 19:17:16, error: Dhcp [1002] - The IP address lease 192.168.1.2 for the Network Card with network address 0021003C9641 has been denied by the DHCP server 192.168.1.1 (The DHCP Server sent a DHCPNACK message). 11.4.2011 і. 19:15:43, error: Dhcp [1002] - The IP address lease 192.168.1.2 for the Network Card with network address 0021003C9641 has been denied by the DHCP server 192.168.1.1 (The DHCP Server sent a DHCPNACK message). 11.4.2011 і. 10:49:22, error: Service Control Manager [7023] - The Logical Disk Manager service terminated with the following error: The specified module could not be found. 11.4.2011 і. 10:36:41, error: Service Control Manager [7023] - The Logical Disk Manager service terminated with the following error: The specified module could not be found. 10.4.2011 і. 23:50:38, error: Service Control Manager [7023] - The Logical Disk Manager service terminated with the following error: The specified module could not be found. 10.4.2011 і. 22:44:17, error: Service Control Manager [7023] - The Logical Disk Manager service terminated with the following error: The specified module could not be found. 10.4.2011 і. 21:57:07, error: Service Control Manager [7023] - The Logical Disk Manager service terminated with the following error: The specified module could not be found. 10.4.2011 і. 19:57:54, error: Service Control Manager [7023] - The Logical Disk Manager service terminated with the following error: The specified module could not be found. 10.4.2011 і. 00:13:39, error: Service Control Manager [7023] - The Logical Disk Manager service terminated with the following error: The specified module could not be found. 09.4.2011 і. 22:35:07, error: Service Control Manager [7023] - The Logical Disk Manager service terminated with the following error: The specified module could not be found. 09.4.2011 і. 02:20:35, error: Server [2505] - The server could not bind to the transport \Device\NetBT_Tcpip_{1B78AF90-62D6-4B81-80B7-F00C07C6929B} because another computer on the network has the same name. The server could not start. 08.4.2011 і. 21:18:09, error: Service Control Manager [7023] - The Logical Disk Manager service terminated with the following error: The specified module could not be found. 08.4.2011 і. 21:17:46, error: Dhcp [1002] - The IP address lease 192.168.1.3 for the Network Card with network address 0021003C9641 has been denied by the DHCP server 192.168.1.1 (The DHCP Server sent a DHCPNACK message). 08.4.2011 і. 19:27:04, error: Service Control Manager [7023] - The Logical Disk Manager service terminated with the following error: The specified module could not be found. 08.4.2011 і. 16:34:15, error: Service Control Manager [7023] - The Logical Disk Manager service terminated with the following error: The specified module could not be found. 08.4.2011 і. 16:25:41, error: Service Control Manager [7023] - The Logical Disk Manager service terminated with the following error: The specified module could not be found. 08.4.2011 і. 11:33:49, error: Service Control Manager [7023] - The Logical Disk Manager service terminated with the following error: The specified module could not be found. 07.4.2011 і. 20:33:16, error: Service Control Manager [7023] - The Logical Disk Manager service terminated with the following error: The specified module could not be found. 07.4.2011 і. 12:48:12, error: Dhcp [1002] - The IP address lease 192.168.1.4 for the Network Card with network address 0021003C9641 has been denied by the DHCP server 192.168.1.1 (The DHCP Server sent a DHCPNACK message). 07.4.2011 і. 12:44:19, error: Service Control Manager [7023] - The Logical Disk Manager service terminated with the following error: The specified module could not be found. . ==== End Of File =========================== DDS: . DDS (Ver_11-03-05.01) - NTFSx86 Run by Administrator at 0:46:06,87 on 14.04.2011 г. Internet Explorer: 8.0.6001.18702 BrowserJavaVersion: 1.6.0_21 Microsoft Windows XP Professional 5.1.2600.3.1251.359.1033.18.1789.509 [GMT 3:00] . . ============== Running Processes =============== . C:\WINDOWS\System32\svchost.exe -k Cognizance C:\WINDOWS\system32\Ati2evxx.exe C:\WINDOWS\system32\svchost -k DcomLaunch c:\Program Files\Hewlett-Packard\Drive Encryption\HpFkCrypt.exe svchost.exe C:\WINDOWS\System32\svchost.exe -k netsvcs C:\Program Files\WIDCOMM\Bluetooth Software\bin\btwdins.exe svchost.exe svchost.exe C:\WINDOWS\system32\Ati2evxx.exe C:\WINDOWS\system32\spoolsv.exe C:\WINDOWS\Explorer.EXE C:\Program Files\Hewlett-Packard\HP Quick Launch Buttons\QlbCtrl.exe C:\Program Files\ActivIdentity\ActivClient\accrdsub.exe C:\Program Files\Hewlett-Packard\HP ProtectTools Security Manager\PTHOSTTR.EXE D:\Programs\iTunes\iTunesHelper.exe C:\Program Files\Common Files\Java\Java Update\jusched.exe C:\Program Files\PC Tools Security\pctsGui.exe C:\Program Files\DAEMON Tools\daemon.exe c:\Program Files\ActivIdentity\ActivClient\acevents.exe C:\Program Files\Messenger\msmsgs.exe C:\WINDOWS\system32\ctfmon.exe svchost.exe C:\Program Files\Skype\Phone\Skype.exe C:\Program Files\WIDCOMM\Bluetooth Software\BTTray.exe C:\WINDOWS\Datecs\Flex2K.exe C:\Program Files\McAfee Security Scan\2.0.181\SSScheduler.exe C:\Program Files\Hamachi\hamachi.exe c:\Program Files\ActivIdentity\ActivClient\accoca.exe C:\PROGRA~1\WIDCOMM\BLUETO~1\BTSTAC~1.EXE C:\WINDOWS\system32\agrsmsvc.exe C:\Program Files\Common Files\Apple\Mobile Device Support\AppleMobileDeviceService.exe C:\Program Files\Bonjour\mDNSResponder.exe C:\WINDOWS\Microsoft.NET\Framework\v4.0.30319\mscorsvw.exe C:\Program Files\Java\jre6\bin\jqs.exe C:\WINDOWS\System32\svchost.exe -k HPZ12 C:\WINDOWS\System32\svchost.exe -k HPZ12 C:\WINDOWS\system32\PnkBstrA.exe C:\Program Files\PC Tools Security\pctsAuxs.exe C:\Program Files\PC Tools Security\pctsSvc.exe C:\Program Files\Microsoft SQL Server\90\Shared\sqlwriter.exe C:\WINDOWS\system32\svchost.exe -k imgsvc c:\Program Files\ATI Technologies\ATI.ACE\Core-Static\MOM.exe c:\Program Files\ATI Technologies\ATI.ACE\Core-Static\ccc.exe C:\Program Files\Mozilla Firefox\firefox.exe C:\Program Files\Skype\Plugin Manager\skypePM.exe C:\Program Files\Hewlett-Packard\Shared\hpqwmiex.exe C:\Program Files\iPod\bin\iPodService.exe c:\PROGRA~1\mcafee\SITEAD~1\mcsacore.exe C:\Program Files\Hewlett-Packard\HP Quick Launch Buttons\Com4QLBEx.exe C:\WINDOWS\system32\rundll32.exe C:\WINDOWS\System32\svchost.exe -k HTTPFilter C:\Program Files\Mozilla Firefox\plugin-container.exe c:\Program Files\Hewlett-Packard\Shared\HpqToaster.exe C:\Documents and Settings\Administrator\Desktop\dds.scr . ============== Pseudo HJT Report =============== . uStart Page = hxxp://search.conduit.com?SearchSource=10&ctid=CT2405280 uInternet Connection Wizard,ShellNext = iexplore uInternet Settings,ProxyOverride = *.local uSearchURL,(Default) = hxxp://toolbar.ask.com/toolbarv/askRedirect?o=101699&gct=&gc=1&q=%s uURLSearchHooks: DefaultSearchHook Class: {c94e154b-1459-4a47-966b-4b843befc7db} - c:\program files\asksearch\bin\DefaultSearch.dll uURLSearchHooks: Softonic-Eng7 Toolbar: {414b6d9d-4a95-4e8d-b5b1-149dd2d93bb3} - c:\program files\softonic-eng7\prxtbSof2.dll uURLSearchHooks: McAfee SiteAdvisor Toolbar: {0ebbbe48-bad4-4b4c-8e5a-516abecae064} - c:\progra~1\mcafee\sitead~1\mcieplg.dll uURLSearchHooks: H - No File BHO: AskBar BHO: {201f27d4-3704-41d6-89c1-aa35e39143ed} - c:\program files\askbardis\bar\bin\askBar.dll BHO: FGCatchUrl: {2f364306-aa45-47b5-9f9d-39a8b94e7ef7} - c:\program files\flashget\jccatch.dll BHO: Conduit Engine : {30f9b915-b755-4826-820b-08fba6bd249d} - c:\program files\conduitengine\prxConduitEngine.dll BHO: Softonic-Eng7 Toolbar: {414b6d9d-4a95-4e8d-b5b1-149dd2d93bb3} - c:\program files\softonic-eng7\prxtbSof2.dll BHO: Spybot-S&D IE Protection: {53707962-6f74-2d53-2644-206d7942484f} - c:\progra~1\spybot~1\SDHelper.dll BHO: McAfee SiteAdvisor BHO: {b164e929-a1b6-4a06-b104-2cd0e90a88ff} - c:\progra~1\mcafee\sitead~1\mcieplg.dll BHO: Java Plug-In 2 SSV Helper: {dbc80044-a445-435b-bc74-9c25c1c588a9} - c:\program files\java\jre6\bin\jp2ssv.dll BHO: Credential Manager for HP ProtectTools: {df21f1db-80c6-11d3-9483-b03d0ec10000} - c:\program files\hewlett-packard\iam\bin\ItIEAddIn.dll BHO: JQSIEStartDetectorImpl Class: {e7e6f031-17ce-4c07-bc86-eabfe594f69c} - c:\program files\java\jre6\lib\deploy\jqs\ie\jqs_plugin.dll BHO: FlashGet GetFlash Class: {f156768e-81ef-470c-9057-481ba8380dba} - c:\program files\flashget\getflash.dll TB: Foxit Toolbar: {3041d03e-fd4b-44e0-b742-2d9b88305f98} - c:\program files\askbardis\bar\bin\askBar.dll TB: Softonic-Eng7 Toolbar: {414b6d9d-4a95-4e8d-b5b1-149dd2d93bb3} - c:\program files\softonic-eng7\prxtbSof2.dll TB: McAfee SiteAdvisor Toolbar: {0ebbbe48-bad4-4b4c-8e5a-516abecae064} - c:\progra~1\mcafee\sitead~1\mcieplg.dll uRun: [DAEMON Tools] "c:\program files\daemon tools\daemon.exe" -lang 1033 uRun: [MSMSGS] "c:\program files\messenger\msmsgs.exe" /background uRun: [ctfmon.exe] c:\windows\system32\ctfmon.exe uRun: [skype] "c:\program files\skype\phone\Skype.exe" /nosplash /minimized mRun: [startCCC] "c:\program files\ati technologies\ati.ace\core-static\CLIStart.exe" mRun: [QlbCtrl.exe] c:\program files\hewlett-packard\hp quick launch buttons\QlbCtrl.exe /Start mRun: [accrdsub] "c:\program files\actividentity\activclient\accrdsub.exe" mRun: [PTHOSTTR] c:\program files\hewlett-packard\hp protecttools security manager\PTHOSTTR.EXE /Start mRun: [CognizanceTS] rundll32.exe c:\progra~1\hewlet~1\iam\bin\ASTSVCC.dll,RegisterModule mRun: [QuickTime Task] "c:\program files\quicktime\QTTask.exe" -atboottime mRun: [iTunesHelper] "d:\programs\itunes\iTunesHelper.exe" mRun: [sunJavaUpdateSched] "c:\program files\common files\java\java update\jusched.exe" mRun: [Flashget] c:\program files\flashget\flashget.exe /min mRun: [iSTray] "c:\program files\pc tools security\pctsGui.exe" /hideGUI mRun: [DWQueuedReporting] "c:\progra~1\common~1\micros~1\dw\dwtrig20.exe" -t dRun: [CTFMON.EXE] c:\windows\system32\CTFMON.EXE StartupFolder: c:\docume~1\admini~1\startm~1\programs\startup\adobeg~1.lnk - c:\program files\common files\adobe\calibration\Adobe Gamma Loader.exe StartupFolder: c:\docume~1\admini~1\startm~1\programs\startup\hamachi.lnk - c:\program files\hamachi\hamachi.exe StartupFolder: c:\docume~1\alluse~1\startm~1\programs\startup\blueto~1.lnk - c:\program files\widcomm\bluetooth software\BTTray.exe StartupFolder: c:\docume~1\alluse~1\startm~1\programs\startup\flexty~1.lnk - c:\windows\datecs\Flex2K.exe StartupFolder: c:\docume~1\alluse~1\startm~1\programs\startup\mcafee~1.lnk - c:\program files\mcafee security scan\2.0.181\SSScheduler.exe IE: &Download All using 4shared Desktop - d:\programs\4shared desktop\down_all.htm IE: &Download All with FlashGet - c:\program files\flashget\jc_all.htm IE: &Download with FlashGet - c:\program files\flashget\jc_link.htm IE: Add to Google Photos Screensa&ver - c:\windows\system32\GPhotos.scr/200 IE: E&xport to Microsoft Excel - c:\progra~1\micros~2\office11\EXCEL.EXE/3000 IE: Send to &Bluetooth Device... - c:\program files\widcomm\bluetooth software\btsendto_ie_ctx.htm IE: Send To Bluetooth - c:\program files\widcomm\bluetooth software\btsendto_ie.htm IE: {CCA281CA-C863-46ef-9331-5C8D4460577F} - c:\program files\widcomm\bluetooth software\btsendto_ie.htm IE: {D6E814A0-E0C5-11d4-8D29-0050BA6940E3} - c:\program files\flashget\FlashGet.exe IE: {e2e2dd38-d088-4134-82b7-f2ba38496583} - %windir%\Network Diagnostic\xpnetdiag.exe IE: {FB5F1910-F110-11d2-BB9E-00C04F795683} - c:\program files\messenger\msmsgs.exe IE: {92780B25-18CC-41C8-B9BE-3C9C571A8263} - {FF059E31-CC5A-4E2E-BF3B-96E929D65503} - c:\progra~1\micros~2\office11\REFIEBAR.DLL IE: {DFB852A3-47F8-48C4-A200-58CAB36FD2A2} - {53707962-6F74-2D53-2644-206D7942484F} - c:\progra~1\spybot~1\SDHelper.dll LSP: c:\program files\common files\pc tools\lsp\PCTLsp.dll DPF: Microsoft XML Parser for Java - file://c:\windows\java\classes\xmldso.cab DPF: {31435657-9980-0010-8000-00AA00389B71} - hxxp://download.microsoft.com/download/e/2/f/e2fcec4b-6c8b-48b7-adab-ab9c403a978f/wvc1dmo.cab DPF: {8AD9C840-044E-11D1-B3E9-00805F499D93} - hxxp://java.sun.com/update/1.6.0/jinstall-1_6_0_21-windows-i586.cab DPF: {CAFEEFAC-0016-0000-0021-ABCDEFFEDCBA} - hxxp://java.sun.com/update/1.6.0/jinstall-1_6_0_21-windows-i586.cab DPF: {CAFEEFAC-FFFF-FFFF-FFFF-ABCDEFFEDCBA} - hxxp://java.sun.com/update/1.6.0/jinstall-1_6_0_21-windows-i586.cab TCP: {9B2D9B85-5FF1-4AE4-AD0F-97B50F0AD220} = 212.39.90.42,212.39.90.43 Handler: dssrequest - {5513F07E-936B-4E52-9B00-067394E91CC5} - c:\progra~1\mcafee\sitead~1\McIEPlg.dll Handler: sacore - {5513F07E-936B-4E52-9B00-067394E91CC5} - c:\progra~1\mcafee\sitead~1\McIEPlg.dll Handler: skype4com - {FFC8B962-9B40-4DFF-9458-1830C7DD7F5D} - c:\progra~1\common~1\skype\SKYPE4~1.DLL Notify: ackpbsc - c:\windows\system32\ackpbsc.dll Notify: acunlock - c:\program files\actividentity\activclient\acunlock.dll Notify: AtiExtEvent - Ati2evxx.dll Notify: OneCard - c:\program files\hewlett-packard\iam\bin\ASWLNPkg.dll AppInit_DLLs: APSHook.dll LSA: Notification Packages = scecli ASWLNPkg mASetup: {ABB0EEF9-CE96-4474-2285-E68550D75C8F} - c:\windows\system32\msn\msn.exe s . ================= FIREFOX =================== . FF - ProfilePath - c:\docume~1\admini~1\applic~1\mozilla\firefox\profiles\korvvd8g.default\ FF - prefs.js: browser.search.defaulturl - hxxp://search.conduit.com/ResultsExt.aspx?ctid=CT2405280&SearchSource=3&q={searchTerms} FF - prefs.js: browser.search.selectedEngine - Secure Search FF - prefs.js: browser.startup.homepage - google.bg FF - prefs.js: keyword.URL - hxxp://search.yahoo.com/search?fr=mcafee&p= FF - prefs.js: network.proxy.type - 4 FF - component: c:\documents and settings\administrator\application data\mozilla\firefox\profiles\korvvd8g.default\extensions\{414b6d9d-4a95-4e8d-b5b1-149dd2d93bb3}\components\FFExternalAlert.dll FF - component: c:\documents and settings\administrator\application data\mozilla\firefox\profiles\korvvd8g.default\extensions\{414b6d9d-4a95-4e8d-b5b1-149dd2d93bb3}\components\RadioWMPCore.dll FF - component: c:\program files\mcafee\siteadvisor\components\McFFPlg.dll FF - plugin: c:\documents and settings\all users\application data\zylom\zylomgamesplayer\npzylomgamesplayer.dll FF - plugin: c:\program files\java\jre6\bin\new_plugin\npdeployJava1.dll FF - plugin: c:\program files\mozilla firefox\plugins\npdeployJava1.dll FF - plugin: c:\program files\mozilla firefox\plugins\npFoxitReaderPlugin.dll FF - plugin: c:\program files\mozilla firefox\plugins\npzylomgamesplayer.dll FF - plugin: d:\programs\itunes\mozilla plugins\npitunes.dll FF - plugin: d:\programs\picasa 3.1 build 71.36\picasa3\npPicasa3.dll . ============= SERVICES / DRIVERS =============== . R0 ahcix86;ahcix86;c:\windows\system32\drivers\ahcix86.sys [2008-9-17 174600] R0 Amddfltr;Amd Disk Lower Filter Driver;c:\windows\system32\drivers\Amddfltr.sys [2008-9-16 15416] R0 PCTCore;PCTools KDS;c:\windows\system32\drivers\PCTCore.sys [2011-4-13 239168] R0 pctDS;PC Tools Data Store;c:\windows\system32\drivers\pctDS.sys [2011-4-13 338880] R0 pctEFA;PC Tools Extended File Attributes;c:\windows\system32\drivers\pctEFA.sys [2011-4-13 656320] R0 SafeBoot;SafeBoot;c:\windows\system32\drivers\SafeBoot.sys [2008-6-5 109184] R0 SbAlg;SbAlg;c:\windows\system32\drivers\SbAlg.sys [2008-6-5 51376] R0 SbFsLock;SbFsLock;c:\windows\system32\drivers\SbFsLock.sys [2008-6-5 12928] R0 SFAUDIO;Sonic Focus DSP Driver;c:\windows\system32\drivers\sfaudio.sys [2008-3-28 24064] R1 RsvLock;RsvLock;c:\windows\system32\drivers\rsvlock.sys [2008-6-5 12496] R2 accoca;ActivClient Middleware Service;c:\program files\actividentity\activclient\accoca.exe [2007-5-15 182576] R2 ASBroker;Logon Session Broker;c:\windows\system32\svchost.exe -k Cognizance [2008-4-14 14336] R2 ASChannel;Local Communication Channel;c:\windows\system32\svchost.exe -k Cognizance [2008-4-14 14336] R2 clr_optimization_v4.0.30319_32;Microsoft .NET Framework NGEN v4.0.30319_X86;c:\windows\microsoft.net\framework\v4.0.30319\mscorsvw.exe [2010-3-18 130384] R2 HpFkCryptService;Drive Encryption Service;c:\program files\hewlett-packard\drive encryption\HpFkCrypt.exe [2008-6-5 256512] R2 McAfee SiteAdvisor Service;McAfee SiteAdvisor Service;c:\progra~1\mcafee\sitead~1\mcsacore.exe [2011-1-5 88176] R2 sdAuxService;PC Tools Auxiliary Service;c:\program files\pc tools security\pctsAuxs.exe [2011-4-13 366840] R2 sdCoreService;PC Tools Security Service;c:\program files\pc tools security\pctsSvc.exe [2011-4-13 1150936] R3 Com4QLBEx;Com4QLBEx;c:\program files\hewlett-packard\hp quick launch buttons\Com4QLBEx.exe [2008-9-16 193840] R3 teamviewervpn;TeamViewer VPN Adapter;c:\windows\system32\drivers\teamviewervpn.sys [2008-1-25 25088] S2 HP ProtectTools Service;HP ProtectTools Service;c:\program files\hewlett-packard\hp protecttools security manager\PTChangeFilterService.exe [2008-6-10 18944] S3 McComponentHostService;McAfee Security Scan Component Host Service;c:\program files\mcafee security scan\2.0.181\McCHSvc.exe [2010-1-15 227232] S3 SCR3XX2K;SCR3xx USB SmartCardReader;c:\windows\system32\drivers\SCR3XX2K.sys [2007-6-21 56448] S3 WPFFontCache_v0400;Windows Presentation Foundation Font Cache 4.0.0.0;c:\windows\microsoft.net\framework\v4.0.30319\wpf\WPFFontCache_v0400.exe [2010-3-18 753504] . =============== Created Last 30 ================ . 2011-04-13 20:53:43 -------- d-----w- c:\docume~1\admini~1\applic~1\ElevatedDiagnostics 2011-04-13 18:25:55 -------- d-----w- c:\docume~1\alluse~1\applic~1\UAB 2011-04-13 18:25:49 -------- d-----w- c:\docume~1\admini~1\locals~1\applic~1\PC_Drivers_Headquarters 2011-04-13 17:23:48 656320 ----a-w- c:\windows\system32\drivers\pctEFA.sys 2011-04-13 17:23:48 338880 ----a-w- c:\windows\system32\drivers\pctDS.sys 2011-04-13 17:23:47 251560 ----a-w- c:\windows\system32\drivers\pctgntdi.sys 2011-04-13 17:23:41 239168 ----a-w- c:\windows\system32\drivers\PCTCore.sys 2011-04-13 17:23:41 160448 ----a-w- c:\windows\system32\drivers\PCTAppEvent.sys 2011-04-13 17:23:36 70536 ----a-w- c:\windows\system32\drivers\pctplsg.sys 2011-04-13 17:23:13 -------- d-----w- c:\program files\common files\PC Tools 2011-04-13 17:23:12 -------- d-----w- c:\program files\PC Tools Security 2011-04-13 17:23:12 -------- d-----w- c:\docume~1\admini~1\applic~1\PC Tools 2011-04-13 17:12:30 -------- d-----w- c:\docume~1\alluse~1\applic~1\PC Tools 2011-04-13 17:12:14 -------- d-----w- c:\docume~1\alluse~1\applic~1\PC Drivers HeadQuarters 2011-04-13 17:10:51 -------- d-----w- c:\program files\PC Drivers HeadQuarters 2011-04-03 17:14:21 142296 ----a-w- c:\program files\mozilla firefox\components\browsercomps.dll 2011-04-03 17:14:20 781272 ----a-w- c:\program files\mozilla firefox\mozsqlite3.dll 2011-04-03 17:14:20 1874904 ----a-w- c:\program files\mozilla firefox\mozjs.dll 2011-04-03 17:14:20 16856 ----a-w- c:\program files\mozilla firefox\plugin-container.exe 2011-04-03 17:14:19 728024 ----a-w- c:\program files\mozilla firefox\libGLESv2.dll 2011-04-03 17:14:19 719832 ----a-w- c:\program files\mozilla firefox\mozcpp19.dll 2011-04-03 17:14:19 1975768 ----a-w- c:\program files\mozilla firefox\D3DCompiler_42.dll 2011-04-03 17:14:19 1893336 ----a-w- c:\program files\mozilla firefox\d3dx9_42.dll 2011-04-03 17:14:19 15832 ----a-w- c:\program files\mozilla firefox\mozalloc.dll 2011-04-03 17:14:19 142296 ----a-w- c:\program files\mozilla firefox\libEGL.dll 2011-04-01 10:42:47 -------- d-----w- c:\docume~1\admini~1\locals~1\applic~1\ConduitEngine 2011-04-01 10:42:46 0 ----a-w- c:\windows\system32\ConduitEngine.tmp 2011-04-01 10:42:46 -------- d-----w- c:\program files\ConduitEngine . ==================== Find3M ==================== . 2011-02-09 13:53:52 270848 ----a-w- c:\windows\system32\sbe.dll 2011-02-09 13:53:52 186880 ----a-w- c:\windows\system32\encdec.dll 2011-02-02 07:58:35 2067456 ----a-w- c:\windows\system32\mstscax.dll 2011-01-27 11:57:06 677888 ----a-w- c:\windows\system32\mstsc.exe 2011-01-21 14:44:37 439296 ----a-w- c:\windows\system32\shimgvw.dll . ============= FINISH: 0:47:45,26 ===============


Разглеждащи това в момента 0
- Няма регистрирани потребители разглеждащи тази страница.