


chuekit
Потребител
-
Регистрация
-
Последно онлайн
Всичко публикувано от chuekit
-
Не държа на физически отделни бутони, трябва ми нещо тествано което да работи и сте доволни от него. До колкото разучих софтуера на Razer е добър. За сега се насочвам към : 1. https://www.ozone.bg/product/geyming-klaviatura-razer-cynosa-lite-us-layout-cherna/ - 45 лв. 2. https://www.ozone.bg/product/geyming-klaviatura-razer-cynosa-v2-us-layout/ - 90 лв.
-
Здравейте , искам да си купя клавиатура,с която мога да правя макро за MMORPG игра. Харесал съм една на RedDragon и една на Razer( в момента е на ~50лв промоция).Бюджет до 100-150 лв . , естествено може и по-евтино Не държа да има мултимедиа бутони , подсветки и т.н . Моля за съвети , какво ползвате , от какво сте доволни. Благодаря предварително !
-
UP , а нещо за моя проблем ? Някой с идея от къде мога да го купя ?
-
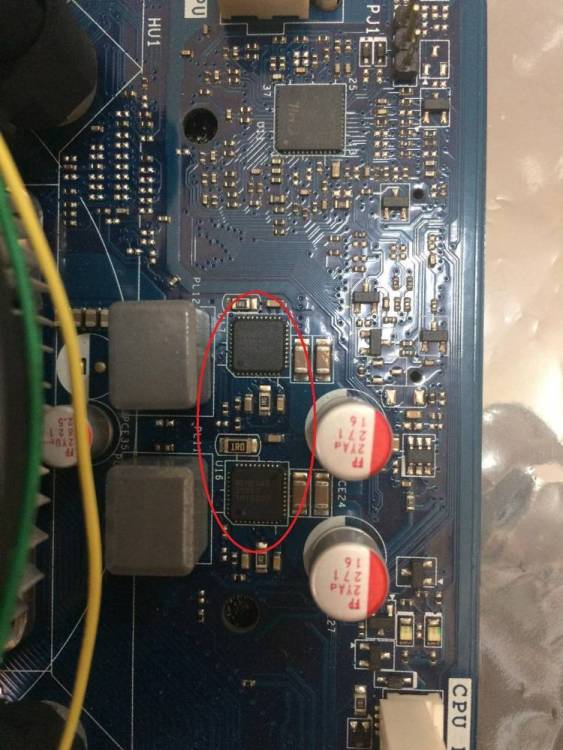
Здравейте отново, Диагнозата е поставена от сервиз , добър електричар с който работя отдавна. Дънната платка е Intel-ска модел : INTEL DESKTOP BOARD DZ77SL50K
-
Здравейте , имам проблем с дънната платка и търся чип : Renesas 20657 1M152D3 Случайно някой да може да ми каже от къде мога да си купя/поръчам такива чипове ?
-
И двете 2-3 на ден , понякога и повече. Имам дълъг маркуч , но точно вън от помещението е паркинга и колите стават ... за автомивка
-
Здравейте , търся нещо такова да закупя от България. В алито се водят Air duster ,разгледах доста БГ онлайн магазини ,но никъде не открих .Моля ,ако някой е мяркал някъде подобно нещо да сподели.И също ако имате наблюдение дали стават . Ще се почистват компютри и лаптопи с това устройсто, тъй като компресора който имаме във фирмата се намира в затворено помещение и ... стават облаци от прах като отида да чистя там. Благодаря предварително на всички ! Лек и спорен ден !

-
Извинявам се , намерихме проблема. Преконфигурираха модема и сега всичко е наред. Благодаря ви за съдействието !
-
При ползване на Мтел хот спот от телефона и теленорски хотспот , нито на компютъра нито на лаптопа имам проблеми. Май всичко идва от ISP-то. Свързах се с тях , чакам сега смяна на IP . Да видим какво ще се получи утре като ми сменят IPто.
-
Здравейте , DNS-ите са автоматично от IPS-то. Настройките на рутерите ми са автоматични. Каквото ми предоставят те , това ползвам. Проблема се получава при всички браузъри.По принцип ползвам само Хром, но пробвах и с Мозила и там проблема е същия. Току що се свързах с IPS-то , попитах ги дали имат проблеми с вируси и т.н и отговора е : Може IP-то да ти е .... ( каквото и да значи това).
-
Здравейте , Имам проблем с вирус. Става единствено, когато отварям БГ страници ( дир.бг, абв.бг , спортал , и т.н) . Когато отварям чужди страници нямам проблем. Другото до което нямам достъп е гмайл , което ме притеснява най-много. Имам пинг до гмайл, гугъл , но гмайл не се отваря. Сканирах с windows defender-a , malwarebytes , superantispyware - Откриват само програми с кракове ,които си пазя от години и cookie-та. В момента сканирам с Eset online scanner - не откри нищо.KVRT - също не открива нищо. Моля за помощ ! П.П и на десктопа и на лаптопа е същото.На десктопа не се отварят почти никакви сайтове ( дори фейсбук и ютуб не отварям) .Основно се играе игра.Приятелката ми се оплака преди ден-два ,че не може да отваря сайтове от телефона си ,но не направих връзка. Дава и грешка за изтекъл сертификат и невъзможност да отвори някои сайтове. FRST : Scan result of Farbar Recovery Scan Tool (FRST) (x64) Version: 10-01-2022 01 Ran by User-33TL (administrator) on DESKTOP-J4MB6U6 (Hewlett-Packard HP Z230 Tower Workstation) (13-01-2022 00:58:18) Running from C:\Users\User-33TL\Downloads Loaded Profiles: User-33TL Platform: Microsoft Windows 10 Pro Version 21H2 19044.1415 (X64) Language: Английски (Съединени щати) -> Български (България) Default browser: Chrome Boot Mode: Normal ==================== Processes (Whitelisted) ================= (If an entry is included in the fixlist, the process will be closed. The file will not be moved.) (A FOUR TECH CO., LTD. -> ) C:\Program Files (x86)\X7OscarLite\X7OscarLite\X7OscarLite.exe (Adobe Inc. -> Adobe Inc.) C:\Program Files (x86)\Common Files\Adobe\ARM\1.0\armsvc.exe (Google LLC -> Google LLC) C:\Program Files\Google\Chrome\Application\chrome.exe <9> (Innova Intellectual Properties S.à r.l. -> Innova Co.) D:\L2EU\system\Frost\LineageII.exe <2> (Innova Intellectual Properties S.àr.l -> Innova Co. SARL) C:\Program Files (x86)\Innova\4game2.0\bin\Innova.Launcher.exe (Intel Corporation - Embedded Subsystems and IP Blocks Group -> Intel Corporation) C:\Program Files (x86)\Intel\Intel(R) Management Engine Components\DAL\jhi_service.exe (Intel Corporation - Embedded Subsystems and IP Blocks Group -> Intel Corporation) C:\Program Files (x86)\Intel\Intel(R) Management Engine Components\LMS\LMS.exe (Intel(R) pGFX -> Intel Corporation) C:\Windows\System32\igfxCUIService.exe (Khrona LLC -> Khrona LLC) D:\L2EU\system\AwesomiumProcess.exe <6> (Microsoft Corporation -> Microsoft Corporation) C:\Windows\Microsoft.NET\Framework64\v3.0\WPF\PresentationFontCache.exe (Microsoft Windows -> Microsoft Corporation) C:\Windows\ImmersiveControlPanel\SystemSettings.exe (Microsoft Windows -> Microsoft Corporation) C:\Windows\System32\dllhost.exe (Microsoft Windows -> Microsoft Corporation) C:\Windows\System32\smartscreen.exe (Microsoft Windows -> Microsoft Corporation) C:\Windows\SysWOW64\wbem\WmiPrvSE.exe (Microsoft Windows Publisher -> Microsoft Corporation) C:\ProgramData\Microsoft\Windows Defender\Platform\4.18.2111.5-0\MpCopyAccelerator.exe (Microsoft Windows Publisher -> Microsoft Corporation) C:\ProgramData\Microsoft\Windows Defender\Platform\4.18.2111.5-0\MsMpEng.exe (Microsoft Windows Publisher -> Microsoft Corporation) C:\ProgramData\Microsoft\Windows Defender\Platform\4.18.2111.5-0\NisSrv.exe (NCSOFT Corporation -> ) D:\L2EU\system\L2.exe <2> (NVIDIA Corporation -> ) C:\Windows\System32\nvwmi64.exe (NVIDIA Corporation -> NVIDIA Corporation) C:\Program Files (x86)\NVIDIA Corporation\3D Vision\nvSCPAPISvr.exe (NVIDIA Corporation -> NVIDIA Corporation) C:\Program Files\NVIDIA Corporation\Display\nvxdsync.exe (NVIDIA Corporation -> NVIDIA Corporation) C:\Windows\System32\nvvsvc.exe <2> (philandro Software GmbH -> philandro Software GmbH) C:\Program Files (x86)\AnyDesk\AnyDesk.exe <2> (Realtek Semiconductor Corp -> Realtek Semiconductor) C:\Program Files\Realtek\Audio\HDA\RAVBg64.exe <3> (Realtek Semiconductor Corp -> Realtek Semiconductor) C:\Program Files\Realtek\Audio\HDA\RAVCpl64.exe (Realtek Semiconductor Corp -> Realtek Semiconductor) C:\Program Files\Realtek\Audio\HDA\RtkAudioService64.exe (Thales DIS CPL USA, Inc. -> Thales Group) C:\Program Files (x86)\Common Files\Aladdin Shared\HASP\hasplms.exe (Thales DIS CPL USA, Inc. -> Thales Group) C:\Program Files (x86)\Common Files\Aladdin Shared\HASP\hasplmv.exe (The CefSharp Authors) [File not signed] C:\Program Files (x86)\Innova\4game2.0\bin\CefSharp.BrowserSubprocess.exe <3> ==================== Registry (Whitelisted) =================== (If an entry is included in the fixlist, the registry item will be restored to default or removed. The file will not be moved.) HKLM\...\Run: [RtHDVCpl] => C:\Program Files\Realtek\Audio\HDA\RAVCpl64.exe [14062848 2015-07-03] (Realtek Semiconductor Corp -> Realtek Semiconductor) HKLM\...\Run: [RtHDVBg] => C:\Program Files\Realtek\Audio\HDA\RAVBg64.exe [1402624 2015-07-03] (Realtek Semiconductor Corp -> Realtek Semiconductor) HKU\S-1-5-21-4171439222-1843728066-1652194855-1001\...\Run: [X7OscarLite] => C:\Program Files (x86)\X7OscarLite\X7OscarLite\X7OscarLite.exe [13071056 2020-11-03] (A FOUR TECH CO., LTD. -> ) HKLM\Software\Microsoft\Active Setup\Installed Components: [{8A69D345-D564-463c-AFF1-A69D9E530F96}] -> C:\Program Files\Google\Chrome\Application\97.0.4692.71\Installer\chrmstp.exe [2022-01-11] (Google LLC -> Google LLC) Startup: C:\ProgramData\Microsoft\Windows\Start Menu\Programs\Startup\AnyDesk.lnk [2021-05-05] ShortcutTarget: AnyDesk.lnk -> C:\Program Files (x86)\AnyDesk\AnyDesk.exe (philandro Software GmbH -> philandro Software GmbH) ==================== Scheduled Tasks (Whitelisted) ============ (If an entry is included in the fixlist, it will be removed from the registry. The file will not be moved unless listed separately.) Task: {1AA89949-A8C4-4181-A55F-C431EE240AD4} - System32\Tasks\RtHDVBg_PushButton => C:\Program Files\Realtek\Audio\HDA\RAVBg64.exe [1402624 2015-07-03] (Realtek Semiconductor Corp -> Realtek Semiconductor) Task: {2CF66C44-FD2C-4D0B-83B7-C974DA2D14B8} - System32\Tasks\Mozilla\Firefox Default Browser Agent 308046B0AF4A39CB => C:\Program Files\Mozilla Firefox\default-browser-agent.exe do-task "308046B0AF4A39CB" Task: {37EE00DE-E646-441A-B3AD-CFF28FB9A979} - System32\Tasks\GoogleUpdateTaskMachineUA => C:\Program Files (x86)\Google\Update\GoogleUpdate.exe [154456 2021-05-05] (Google LLC -> Google LLC) Task: {3EC8385B-3DDC-4729-9065-0BC98317A886} - System32\Tasks\GoogleUpdateTaskMachineCore => C:\Program Files (x86)\Google\Update\GoogleUpdate.exe [154456 2021-05-05] (Google LLC -> Google LLC) Task: {538831BE-A2FD-4939-977D-0C4FA582F6C8} - System32\Tasks\Adobe Acrobat Update Task => C:\Program Files (x86)\Common Files\Adobe\ARM\1.0\AdobeARM.exe [1564424 2021-11-17] (Adobe Inc. -> Adobe Inc.) Task: {74BDF347-6F0A-4681-8A62-65CDE2356F1E} - System32\Tasks\Microsoft\Windows\Windows Defender\Windows Defender Scheduled Scan => C:\ProgramData\Microsoft\Windows Defender\Platform\4.18.2111.5-0\MpCmdRun.exe [901048 2021-12-16] (Microsoft Windows Publisher -> Microsoft Corporation) Task: {7C7320CF-0FF6-4904-A4AE-A2DAE1E6D4D6} - System32\Tasks\EOSv3 Scheduler onLogOn => C:\Users\User-33TL\Downloads\esetonlinescanner_enu.exe [14562400 2022-01-12] (ESET, spol. s r.o. -> ESET spol. s r.o.) Task: {815C4F08-4B59-471A-AABE-808CA4F7AC5F} - System32\Tasks\EOSv3 Scheduler onTime => C:\Users\User-33TL\Downloads\esetonlinescanner_enu.exe [14562400 2022-01-12] (ESET, spol. s r.o. -> ESET spol. s r.o.) Task: {A569FFDD-1868-4176-BA33-47AAA55561A0} - System32\Tasks\Intel PTT EK Recertification => C:\Program Files\Intel\iCLS Client\IntelPTTEKRecertification.exe [909112 2016-06-14] (Intel(R) Trusted Connect Service -> Intel(R) Corporation) Task: {BC224353-E9B4-4BB6-A3A4-CAAAE6F0783C} - System32\Tasks\Microsoft\Windows\Windows Defender\Windows Defender Verification => C:\ProgramData\Microsoft\Windows Defender\Platform\4.18.2111.5-0\MpCmdRun.exe [901048 2021-12-16] (Microsoft Windows Publisher -> Microsoft Corporation) Task: {EBA6A610-F2F7-4DD2-8AE6-F1137E8C616B} - System32\Tasks\Microsoft\Windows\Windows Defender\Windows Defender Cache Maintenance => C:\ProgramData\Microsoft\Windows Defender\Platform\4.18.2111.5-0\MpCmdRun.exe [901048 2021-12-16] (Microsoft Windows Publisher -> Microsoft Corporation) Task: {FAE29BC4-5F64-4558-81EB-9FDC372540AA} - System32\Tasks\Microsoft\Windows\Windows Defender\Windows Defender Cleanup => C:\ProgramData\Microsoft\Windows Defender\Platform\4.18.2111.5-0\MpCmdRun.exe [901048 2021-12-16] (Microsoft Windows Publisher -> Microsoft Corporation) (If an entry is included in the fixlist, the task (.job) file will be moved. The file which is running by the task will not be moved.) ==================== Internet (Whitelisted) ==================== (If an item is included in the fixlist, if it is a registry item it will be removed or restored to default.) Tcpip\Parameters: [DhcpNameServer] 45.144.64.151 185.204.2.172 Tcpip\..\Interfaces\{4359bd2c-94bb-4914-9971-b288452e8b5a}: [DhcpNameServer] 192.168.0.1 Tcpip\..\Interfaces\{4d887317-5d48-4a5a-8781-3cad0138f42f}: [DhcpNameServer] 192.168.100.1 Tcpip\..\Interfaces\{763f1778-01c9-416e-9e89-9533aa8058c7}: [DhcpNameServer] 45.144.64.151 185.204.2.172 Tcpip\..\Interfaces\{eef272d9-84a6-472a-b89a-2279d158f9e6}: [DhcpNameServer] 192.168.0.1 Edge: ======= Edge DefaultProfile: Default Edge Profile: C:\Users\User-33TL\AppData\Local\Microsoft\Edge\User Data\Default [2022-01-12] FireFox: ======== FF DefaultProfile: 2fdwzk6f.default FF ProfilePath: C:\Users\User-33TL\AppData\Roaming\Mozilla\Firefox\Profiles\2fdwzk6f.default [2021-05-05] FF ProfilePath: C:\Users\User-33TL\AppData\Roaming\Mozilla\Firefox\Profiles\83axs5bv.default-release [2022-01-12] FF Extension: (AdBlock - Най-добрия в блокирането на реклами) - C:\Users\User-33TL\AppData\Roaming\Mozilla\Firefox\Profiles\83axs5bv.default-release\Extensions\[email protected] [2022-01-12] FF Plugin: @videolan.org/vlc,version=3.0.12 -> C:\Program Files\VideoLAN\VLC\npvlc.dll [2021-01-04] (VideoLAN -> VideoLAN) FF Plugin-x32: @nvidia.com/3DVision -> C:\Program Files (x86)\NVIDIA Corporation\3D Vision\npnv3dv.dll [2015-07-23] (NVIDIA Corporation PE Sign v2014 -> NVIDIA Corporation) [File not signed] FF Plugin-x32: @nvidia.com/3DVisionStreaming -> C:\Program Files (x86)\NVIDIA Corporation\3D Vision\npnv3dvstreaming.dll [2015-07-23] (NVIDIA Corporation PE Sign v2014 -> NVIDIA Corporation) [File not signed] FF Plugin-x32: Adobe Reader -> C:\Program Files (x86)\Adobe\Acrobat Reader DC\Reader\AIR\nppdf32.dll [2021-10-05] (Adobe Inc. -> Adobe Systems Inc.) Chrome: ======= CHR Profile: C:\Users\User-33TL\AppData\Local\Google\Chrome\User Data\Default [2022-01-13] CHR Extension: (Презентации) - C:\Users\User-33TL\AppData\Local\Google\Chrome\User Data\Default\Extensions\aapocclcgogkmnckokdopfmhonfmgoek [2021-05-05] CHR Extension: (Документи) - C:\Users\User-33TL\AppData\Local\Google\Chrome\User Data\Default\Extensions\aohghmighlieiainnegkcijnfilokake [2021-05-05] CHR Extension: (Google Диск) - C:\Users\User-33TL\AppData\Local\Google\Chrome\User Data\Default\Extensions\apdfllckaahabafndbhieahigkjlhalf [2021-05-05] CHR Extension: (YouTube) - C:\Users\User-33TL\AppData\Local\Google\Chrome\User Data\Default\Extensions\blpcfgokakmgnkcojhhkbfbldkacnbeo [2021-05-05] CHR Extension: (Adblock Plus — безплатен блокер на реклами) - C:\Users\User-33TL\AppData\Local\Google\Chrome\User Data\Default\Extensions\cfhdojbkjhnklbpkdaibdccddilifddb [2022-01-12] CHR Extension: (Таблици) - C:\Users\User-33TL\AppData\Local\Google\Chrome\User Data\Default\Extensions\felcaaldnbdncclmgdcncolpebgiejap [2021-05-05] CHR Extension: (Google Документи офлайн) - C:\Users\User-33TL\AppData\Local\Google\Chrome\User Data\Default\Extensions\ghbmnnjooekpmoecnnnilnnbdlolhkhi [2021-12-12] CHR Extension: (AdBlock - Най-добрия в блокирането на реклами) - C:\Users\User-33TL\AppData\Local\Google\Chrome\User Data\Default\Extensions\gighmmpiobklfepjocnamgkkbiglidom [2022-01-12] CHR Extension: (Плащания в уеб магазина на Chrome) - C:\Users\User-33TL\AppData\Local\Google\Chrome\User Data\Default\Extensions\nmmhkkegccagdldgiimedpiccmgmieda [2021-05-05] CHR Extension: (Gmail) - C:\Users\User-33TL\AppData\Local\Google\Chrome\User Data\Default\Extensions\pjkljhegncpnkpknbcohdijeoejaedia [2021-05-05] ==================== Services (Whitelisted) =================== (If an entry is included in the fixlist, it will be removed from the registry. The file will not be moved unless listed separately.) R2 AdobeARMservice; C:\Program Files (x86)\Common Files\Adobe\ARM\1.0\armsvc.exe [169728 2021-11-17] (Adobe Inc. -> Adobe Inc.) R2 AnyDesk; C:\Program Files (x86)\AnyDesk\AnyDesk.exe [3743984 2021-11-15] (philandro Software GmbH -> philandro Software GmbH) R2 hasplms; C:\Program Files (x86)\Common Files\Aladdin Shared\HASP\hasplms.exe [7892472 2021-07-07] (Thales DIS CPL USA, Inc. -> Thales Group) R2 NVWMI; C:\Windows\system32\nvwmi64.exe [3173552 2015-07-29] (NVIDIA Corporation -> ) S3 Sense; C:\Program Files\Windows Defender Advanced Threat Protection\MsSense.exe [6138112 2021-12-15] (Microsoft Windows Publisher -> Microsoft Corporation) R3 WdNisSvc; C:\ProgramData\Microsoft\Windows Defender\Platform\4.18.2111.5-0\NisSrv.exe [2876152 2021-12-16] (Microsoft Windows Publisher -> Microsoft Corporation) R2 WinDefend; C:\ProgramData\Microsoft\Windows Defender\Platform\4.18.2111.5-0\MsMpEng.exe [128360 2021-12-16] (Microsoft Windows Publisher -> Microsoft Corporation) ===================== Drivers (Whitelisted) =================== (If an entry is included in the fixlist, it will be removed from the registry. The file will not be moved unless listed separately.) S3 akshasp; C:\Windows\system32\DRIVERS\akshasp.sys [69560 2021-07-07] (Gemalto, Inc. -> SafeNet, Inc.) S3 akshhl; C:\Windows\system32\DRIVERS\akshhl.sys [68536 2021-07-07] (Gemalto, Inc. -> SafeNet, Inc.) S3 aksusb; C:\Windows\System32\drivers\aksusb.sys [313784 2021-07-07] (Gemalto, Inc. -> SafeNet, Inc.) S3 aksusb; C:\Windows\SysWOW64\drivers\aksusb.sys [18944 2001-10-19] (Aladdin Knowledge Systems) [File not signed] S3 athur; C:\Windows\System32\drivers\athuw8x.sys [2919936 2013-06-02] (Microsoft Windows Hardware Compatibility Publisher -> Qualcomm Atheros Communications, Inc.) S3 BthA2dp; C:\Windows\System32\drivers\BthA2dp.sys [279040 2019-12-07] (Microsoft Corporation) [File not signed] S3 BthHFEnum; C:\Windows\System32\drivers\bthhfenum.sys [144896 2019-12-07] (Microsoft Corporation) [File not signed] S2 Hardlock; C:\Windows\system32\drivers\hardlock.sys [314368 2006-12-04] (Microsoft Windows Hardware Compatibility Publisher -> Aladdin Knowledge Systems Ltd.) R3 MpKsl4a92d2d9; C:\ProgramData\Microsoft\Windows Defender\Definition Updates\{75C28AE4-9185-42CC-B510-C606415C5384}\MpKslDrv.sys [134376 2022-01-13] (Microsoft Windows -> Microsoft Corporation) S0 WdBoot; C:\Windows\System32\drivers\wd\WdBoot.sys [48536 2021-12-16] (Microsoft Windows Early Launch Anti-malware Publisher -> Microsoft Corporation) R0 WdFilter; C:\Windows\System32\drivers\wd\WdFilter.sys [435432 2021-12-16] (Microsoft Windows -> Microsoft Corporation) R3 WdNisDrv; C:\Windows\System32\drivers\wd\WdNisDrv.sys [86248 2021-12-16] (Microsoft Windows -> Microsoft Corporation) ==================== NetSvcs (Whitelisted) =================== (If an entry is included in the fixlist, it will be removed from the registry. The file will not be moved unless listed separately.) ==================== One month (created) (Whitelisted) ========= (If an entry is included in the fixlist, the file/folder will be moved.) 2022-01-13 00:58 - 2022-01-13 00:58 - 000014945 _____ C:\Users\User-33TL\Downloads\FRST.txt 2022-01-13 00:57 - 2022-01-13 00:58 - 000000000 ____D C:\FRST 2022-01-13 00:51 - 2022-01-13 00:51 - 000319720 _____ (AO Kaspersky Lab) C:\Windows\system32\Drivers\klupd_b6b64664a_klark.sys 2022-01-13 00:50 - 2022-01-13 00:50 - 000299544 _____ (AO Kaspersky Lab) C:\Windows\system32\Drivers\b6b64664.sys 2022-01-13 00:50 - 2022-01-13 00:50 - 000229248 _____ (AO Kaspersky Lab) C:\Windows\system32\Drivers\klupd_b6b64664a_mark.sys 2022-01-13 00:50 - 2022-01-13 00:50 - 000000000 ____D C:\KVRT2020_Data 2022-01-13 00:43 - 2022-01-13 00:43 - 000003828 _____ C:\Windows\system32\Tasks\EOSv3 Scheduler onLogOn 2022-01-13 00:43 - 2022-01-13 00:43 - 000003386 _____ C:\Windows\system32\Tasks\EOSv3 Scheduler onTime 2022-01-12 23:47 - 2022-01-12 23:50 - 112580096 _____ (AO Kaspersky Lab) C:\Users\User-33TL\Downloads\KVRT.exe 2022-01-12 23:46 - 2022-01-12 23:54 - 000000674 _____ C:\Users\User-33TL\Desktop\ESET Online Scanner.lnk 2022-01-12 23:45 - 2022-01-12 23:45 - 000000773 _____ C:\Users\User-33TL\AppData\Roaming\Microsoft\Windows\Start Menu\Programs\ESET Online Scanner.lnk 2022-01-12 23:45 - 2022-01-12 23:45 - 000000000 ____D C:\Users\User-33TL\AppData\Local\ESET 2022-01-12 23:44 - 2022-01-12 23:45 - 014562400 _____ (ESET spol. s r.o.) C:\Users\User-33TL\Downloads\esetonlinescanner_enu.exe 2022-01-12 23:43 - 2022-01-12 23:43 - 002311680 _____ (Farbar) C:\Users\User-33TL\Downloads\FRST64.exe 2022-01-12 23:00 - 2022-01-12 23:01 - 188022856 _____ (SUPERAntiSpyware) C:\Users\User-33TL\Downloads\SUPERAntiSpyware.exe 2022-01-11 23:25 - 2022-01-11 23:25 - 000000000 ___HD C:\$WinREAgent 2022-01-07 14:46 - 2022-01-07 14:46 - 000001023 _____ C:\Users\User-33TL\Desktop\Frozen Throne - Пряк път.lnk 2021-12-21 19:21 - 2016-11-07 12:51 - 000054728 _____ (NVIDIA Corporation) C:\Windows\system32\nvhdap64.dll 2021-12-21 19:20 - 2021-12-21 19:20 - 000000000 ____D C:\Program Files\Waves 2021-12-21 19:19 - 2021-12-21 19:19 - 000000000 ____D C:\Windows\system32\SRSLabs 2021-12-21 19:19 - 2015-07-03 21:24 - 003271912 _____ (Realtek Semiconductor Corp.) C:\Windows\system32\RtkApi64.dll 2021-12-21 19:19 - 2015-07-03 21:24 - 003232448 _____ (Fortemedia Corporation) C:\Windows\system32\FMAPO64.dll 2021-12-21 19:19 - 2015-07-03 21:24 - 002966144 _____ (Realtek Semiconductor Corp.) C:\Windows\system32\RltkAPO64.dll 2021-12-21 19:19 - 2015-07-03 21:24 - 001599792 _____ (Conexant Systems Inc.) C:\Windows\system32\CX64APO.dll 2021-12-21 19:19 - 2015-07-03 21:24 - 001435144 _____ (Synopsys, Inc.) C:\Windows\system32\SRRPTR64.dll 2021-12-21 19:19 - 2015-07-03 21:24 - 001331336 _____ (Realtek Semiconductor Corp.) C:\Windows\system32\RTCOM64.dll 2021-12-21 19:19 - 2015-07-03 21:24 - 000645464 _____ (Realtek Semiconductor Corp.) C:\Windows\system32\RtDataProc64.dll 2021-12-21 19:19 - 2015-07-03 21:24 - 000574248 _____ (Andrea Electronics Corporation) C:\Windows\system32\AERTAC64.dll 2021-12-21 19:19 - 2015-07-03 21:24 - 000467160 _____ (Synopsys, Inc.) C:\Windows\system32\SRAPO64.dll 2021-12-21 19:19 - 2015-07-03 21:24 - 000387320 _____ (Dolby Laboratories, Inc.) C:\Windows\system32\RTEEP64A.dll 2021-12-21 19:19 - 2015-07-03 21:24 - 000381416 _____ (Synopsys, Inc.) C:\Windows\system32\SRCOM64.dll 2021-12-21 19:19 - 2015-07-03 21:24 - 000343712 _____ (Realtek Semiconductor Corp.) C:\Windows\system32\RtlCPAPI64.dll 2021-12-21 19:19 - 2015-07-03 21:24 - 000341160 _____ (Synopsys, Inc.) C:\Windows\SysWOW64\SRCOM.dll 2021-12-21 19:19 - 2015-07-03 21:24 - 000341160 _____ (Synopsys, Inc.) C:\Windows\system32\SRCOM.dll 2021-12-21 19:19 - 2015-07-03 21:24 - 000321720 _____ (Dolby Laboratories, Inc.) C:\Windows\system32\RP3DHT64.dll 2021-12-21 19:19 - 2015-07-03 21:24 - 000321720 _____ (Dolby Laboratories, Inc.) C:\Windows\system32\RP3DAA64.dll 2021-12-21 19:19 - 2015-07-03 21:24 - 000231920 _____ (Synopsys, Inc.) C:\Windows\system32\SFNHK64.dll 2021-12-21 19:19 - 2015-07-03 21:24 - 000214840 _____ (Dolby Laboratories, Inc.) C:\Windows\system32\RTEED64A.dll 2021-12-21 19:19 - 2015-07-03 21:24 - 000195184 _____ (Realtek Semiconductor Corp.) C:\Windows\system32\RtkCfg64.dll 2021-12-21 19:19 - 2015-07-03 21:24 - 000190552 _____ (Sonic Focus, Inc.) C:\Windows\system32\SFProc64.dll 2021-12-21 19:19 - 2015-07-03 21:24 - 000118600 _____ (Andrea Electronics Corporation) C:\Windows\system32\AERTAR64.dll 2021-12-21 19:19 - 2015-07-03 21:24 - 000110992 _____ (Dolby Laboratories, Inc.) C:\Windows\system32\RTEEL64A.dll 2021-12-21 19:19 - 2015-07-03 21:24 - 000096064 _____ (Sonic Focus, Inc.) C:\Windows\system32\SFComm64.dll 2021-12-21 19:19 - 2015-07-03 21:24 - 000093504 _____ (Sonic Focus, Inc.) C:\Windows\system32\SFSAPO64.dll 2021-12-21 19:19 - 2015-07-03 21:24 - 000092480 _____ (Sonic Focus, Inc.) C:\Windows\system32\SFHAPO64.dll 2021-12-21 19:19 - 2015-07-03 21:24 - 000092480 _____ (Sonic Focus, Inc.) C:\Windows\system32\SFDAPO64.dll 2021-12-21 19:19 - 2015-07-03 21:24 - 000090920 _____ (Synopsys, Inc.) C:\Windows\system32\SFCOM64.dll 2021-12-21 19:19 - 2015-07-03 21:24 - 000088352 _____ (Dolby Laboratories, Inc.) C:\Windows\system32\RTEEG64A.dll 2021-12-21 19:19 - 2015-07-03 21:24 - 000088328 _____ (Synopsys, Inc.) C:\Windows\system32\SFAPO64.dll 2021-12-21 19:19 - 2015-07-03 21:24 - 000083632 _____ (Virage Logic Corporation / Sonic Focus) C:\Windows\SysWOW64\SFCOM.dll 2021-12-21 19:19 - 2015-07-03 21:21 - 072121872 _____ (Realtek Semiconductor Corp.) C:\Windows\system32\RCoRes64.dat 2021-12-21 19:19 - 2015-07-03 21:21 - 004515584 _____ (Realtek Semiconductor Corp.) C:\Windows\system32\Drivers\RTKVHD64.sys 2021-12-21 19:19 - 2015-07-03 21:21 - 002926848 _____ (Realtek Semiconductor Corp.) C:\Windows\system32\RtPgEx64.dll 2021-12-21 19:19 - 2015-07-03 21:21 - 002711296 _____ (Realtek Semiconductor Corp.) C:\Windows\system32\RTSnMg64.cpl 2021-12-21 19:19 - 2015-07-03 21:21 - 001757440 _____ (Realtek Semiconductor Corp.) C:\Windows\system32\RCoInstII64.dll 2021-12-21 19:19 - 2015-07-03 21:21 - 000122328 _____ (Real Sound Lab SIA) C:\Windows\system32\CONEQMSAPOGUILibrary.dll 2021-12-21 19:19 - 2015-07-03 21:21 - 000023704 _____ (Realtek Semiconductor Corp.) C:\Windows\system32\RtkCoLDR64.dll 2021-12-21 19:19 - 2015-07-02 11:43 - 002897741 _____ C:\Windows\system32\Drivers\RTAIODAT.DAT 2021-12-21 19:17 - 2021-12-21 19:17 - 000002134 _____ C:\Users\Public\Desktop\3D Vision Photo Viewer.lnk 2021-12-21 19:17 - 2021-12-21 19:17 - 000000000 ____D C:\ProgramData\Microsoft\Windows\Start Menu\Programs\NVIDIA Corporation 2021-12-21 19:15 - 2015-07-23 02:44 - 000572048 _____ (NVIDIA Corporation) C:\Windows\SysWOW64\nvStreaming.exe 2021-12-17 18:29 - 2021-12-17 18:29 - 000009331 _____ C:\Users\User-33TL\Downloads\MacroLibrary (1).rar 2021-12-15 21:03 - 2021-12-15 21:03 - 000000000 ____D C:\Windows\SystemTemp 2021-12-15 12:32 - 2021-12-15 12:32 - 000272384 _____ C:\Windows\system32\TpmTool.exe 2021-12-15 12:32 - 2021-12-15 12:32 - 000223744 _____ C:\Windows\SysWOW64\TpmTool.exe 2021-12-15 12:32 - 2021-12-15 12:32 - 000162816 _____ C:\Windows\system32\DataStoreCacheDumpTool.exe 2021-12-15 12:32 - 2021-12-15 12:32 - 000011979 _____ C:\Windows\system32\DrtmAuthTxt.wim ==================== One month (modified) ================== (If an entry is included in the fixlist, the file/folder will be moved.) 2022-01-13 00:44 - 2019-12-07 11:14 - 000000000 ____D C:\ProgramData\regid.1991-06.com.microsoft 2022-01-13 00:33 - 2021-05-05 08:40 - 000000000 ____D C:\Program Files (x86)\Google 2022-01-13 00:00 - 2020-11-19 09:54 - 000841126 _____ C:\Windows\system32\PerfStringBackup.INI 2022-01-13 00:00 - 2019-12-07 11:13 - 000000000 ____D C:\Windows\INF 2022-01-12 23:53 - 2021-12-02 18:44 - 000000000 ____D C:\ProgramData\NVIDIA 2022-01-12 23:53 - 2021-05-05 17:41 - 000008192 ___SH C:\DumpStack.log.tmp 2022-01-12 23:53 - 2021-05-05 07:51 - 000000180 _____ C:\Windows\system32\{A6D608F0-0BDE-491A-97AE-5C4B05D86E01}.bat 2022-01-12 23:53 - 2020-11-19 09:43 - 000000006 ____H C:\Windows\Tasks\SA.DAT 2022-01-12 23:52 - 2019-12-07 11:03 - 000524288 _____ C:\Windows\system32\config\BBI 2022-01-12 23:25 - 2021-05-05 10:35 - 000000000 ____D C:\Users\User-33TL\AppData\Roaming\Awesomium 2022-01-12 22:58 - 2020-11-19 09:43 - 000000000 ____D C:\Windows\system32\SleepStudy 2022-01-12 20:56 - 2021-05-05 09:17 - 000000000 ____D C:\Users\User-33TL\AppData\LocalLow\Mozilla 2022-01-12 20:56 - 2021-05-05 09:17 - 000000000 ____D C:\ProgramData\Mozilla 2022-01-12 09:49 - 2019-12-07 11:14 - 000000000 ___HD C:\Program Files\WindowsApps 2022-01-12 09:49 - 2019-12-07 11:14 - 000000000 ____D C:\Windows\AppReadiness 2022-01-11 08:39 - 2021-05-05 08:41 - 000002245 _____ C:\ProgramData\Microsoft\Windows\Start Menu\Programs\Google Chrome.lnk 2022-01-11 08:39 - 2021-05-05 08:41 - 000002204 _____ C:\Users\Public\Desktop\Google Chrome.lnk 2022-01-08 19:03 - 2020-11-19 09:46 - 000002438 _____ C:\ProgramData\Microsoft\Windows\Start Menu\Programs\Microsoft Edge.lnk 2022-01-08 19:03 - 2020-11-19 09:46 - 000002276 _____ C:\Users\Public\Desktop\Microsoft Edge.lnk 2022-01-06 22:39 - 2021-05-05 08:58 - 000004562 _____ C:\Windows\system32\Tasks\Adobe Acrobat Update Task 2021-12-24 12:31 - 2021-05-05 07:56 - 000000000 ____D C:\Program Files\Microsoft Update Health Tools 2021-12-21 19:27 - 2019-12-07 11:03 - 000000000 ____D C:\Windows\CbsTemp 2021-12-21 19:19 - 2021-05-05 07:50 - 000000000 ____D C:\Windows\SysWOW64\RTCOM 2021-12-21 19:15 - 2021-12-02 18:44 - 000000000 ____D C:\ProgramData\NVIDIA Corporation 2021-12-21 19:14 - 2019-12-07 11:14 - 000000000 ____D C:\Windows\system32\Sysprep 2021-12-21 00:41 - 2021-05-05 09:11 - 000000000 ____D C:\Users\User-33TL\AppData\Roaming\discord 2021-12-21 00:26 - 2021-05-05 09:10 - 000000000 ____D C:\Users\User-33TL\AppData\Local\Discord 2021-12-16 21:11 - 2020-11-19 09:43 - 000000000 ____D C:\Windows\system32\Drivers\wd 2021-12-15 21:04 - 2020-11-19 09:43 - 000257824 _____ C:\Windows\system32\FNTCACHE.DAT 2021-12-15 21:03 - 2019-12-07 11:54 - 000000000 ____D C:\Program Files\Windows Defender Advanced Threat Protection 2021-12-15 21:03 - 2019-12-07 11:14 - 000000000 ___RD C:\Windows\ImmersiveControlPanel 2021-12-15 21:03 - 2019-12-07 11:14 - 000000000 ____D C:\Windows\SystemResources 2021-12-15 21:03 - 2019-12-07 11:14 - 000000000 ____D C:\Windows\system32\setup 2021-12-15 21:03 - 2019-12-07 11:14 - 000000000 ____D C:\Windows\system32\oobe 2021-12-15 21:03 - 2019-12-07 11:14 - 000000000 ____D C:\Windows\system32\lv-LV 2021-12-15 21:03 - 2019-12-07 11:14 - 000000000 ____D C:\Windows\system32\lt-LT 2021-12-15 21:03 - 2019-12-07 11:14 - 000000000 ____D C:\Windows\system32\et-EE 2021-12-15 21:03 - 2019-12-07 11:14 - 000000000 ____D C:\Windows\system32\es-MX 2021-12-15 21:03 - 2019-12-07 11:14 - 000000000 ____D C:\Windows\Provisioning 2021-12-15 21:03 - 2019-12-07 11:14 - 000000000 ____D C:\Windows\PolicyDefinitions 2021-12-15 21:03 - 2019-12-07 11:14 - 000000000 ____D C:\Windows\bcastdvr 2021-12-15 12:26 - 2021-05-05 07:54 - 000000000 ____D C:\Windows\system32\MRT 2021-12-15 12:25 - 2021-05-05 07:54 - 137938848 ____C (Microsoft Corporation) C:\Windows\system32\MRT.exe ==================== SigCheck ============================ (There is no automatic fix for files that do not pass verification.) ==================== End of FRST.txt ======================== Addition : Additional scan result of Farbar Recovery Scan Tool (x64) Version: 10-01-2022 01 Ran by User-33TL (13-01-2022 00:59:15) Running from C:\Users\User-33TL\Downloads Microsoft Windows 10 Pro Version 21H2 19044.1415 (X64) (2021-05-05 15:43:14) Boot Mode: Normal ========================================================== ==================== Accounts: ============================= (If an entry is included in the fixlist, it will be removed.) Administrator (S-1-5-21-4171439222-1843728066-1652194855-500 - Administrator - Disabled) DefaultAccount (S-1-5-21-4171439222-1843728066-1652194855-503 - Limited - Disabled) Guest (S-1-5-21-4171439222-1843728066-1652194855-501 - Limited - Disabled) User-33TL (S-1-5-21-4171439222-1843728066-1652194855-1001 - Administrator - Enabled) => C:\Users\User-33TL WDAGUtilityAccount (S-1-5-21-4171439222-1843728066-1652194855-504 - Limited - Disabled) ==================== Security Center ======================== (If an entry is included in the fixlist, it will be removed.) AV: Windows Defender (Enabled - Up to date) {D68DDC3A-831F-4fae-9E44-DA132C1ACF46} ==================== Installed Programs ====================== (Only the adware programs with "Hidden" flag could be added to the fixlist to unhide them. The adware programs should be uninstalled manually.) 4game (HKLM-x32\...\4game2.0) (Version: 1.0.0.264-f - Innova Co. SARL) Adobe Acrobat Reader DC (HKLM-x32\...\{AC76BA86-7AD7-1033-7B44-AC0F074E4100}) (Version: 21.007.20099 - Adobe Systems Incorporated) AnyDesk (HKLM-x32\...\AnyDesk) (Version: ad 6.2.6 - philandro Software GmbH) Discord (HKU\S-1-5-21-4171439222-1843728066-1652194855-1001\...\Discord) (Version: 1.0.9001 - Discord Inc.) Google Chrome (HKLM-x32\...\Google Chrome) (Version: 97.0.4692.71 - Google LLC) Intel(R) Management Engine Components (HKLM\...\{1CEAC85D-2590-4760-800F-8DE5E91F3700}) (Version: 11.5.0.1020 - Intel Corporation) Intel(R) Processor Graphics (HKLM-x32\...\{F0E3AD40-2BBD-4360-9C76-B9AC9A5886EA}) (Version: 20.19.15.4835 - Intel Corporation) Lineage 2 EU (HKLM-x32\...\4game2.0_l2-eu_live) (Version: L2EU-P-210714-220105-1 - Innova Co. SARL) Maxx Audio Installer (x64) (HKLM\...\{307032B2-6AF2-46D7-B933-62438DEB2B9A}) (Version: 2.6.6448.1 - Waves Audio Ltd.) Hidden Microsoft Edge (HKLM-x32\...\Microsoft Edge) (Version: 97.0.1072.55 - Microsoft Corporation) Microsoft OneDrive (HKU\S-1-5-21-4171439222-1843728066-1652194855-1001\...\OneDriveSetup.exe) (Version: 21.230.1107.0004 - Microsoft Corporation) Microsoft Update Health Tools (HKLM\...\{E876418F-BE59-4D8C-B9A5-74B056B676FA}) (Version: 2.93.0.0 - Microsoft Corporation) Microsoft Visual C++ 2015 Redistributable (x64) - 14.0.23918 (HKLM-x32\...\{dab68466-3a7d-41a8-a5cf-415e3ff8ef71}) (Version: 14.0.23918.0 - Microsoft Corporation) Microsoft Visual C++ 2015 Redistributable (x86) - 14.0.23918 (HKLM-x32\...\{2e085fd2-a3e4-4b39-8e10-6b8d35f55244}) (Version: 14.0.23918.0 - Microsoft Corporation) Mozilla Firefox 88.0 (x64 bg) (HKLM\...\Mozilla Firefox 88.0 (x64 bg)) (Version: 88.0 - Mozilla) Mozilla Maintenance Service (HKLM\...\MozillaMaintenanceService) (Version: 88.0 - Mozilla) NVIDIA 3D Vision Driver 353.62 (HKLM\...\{B2FE1952-0186-46C3-BAEC-A80AA35AC5B8}_Display.3DVision) (Version: 353.62 - NVIDIA Corporation) NVIDIA Graphics Driver 353.62 (HKLM\...\{B2FE1952-0186-46C3-BAEC-A80AA35AC5B8}_Display.Driver) (Version: 353.62 - NVIDIA Corporation) NVIDIA nView 146.33 (HKLM\...\{B2FE1952-0186-46C3-BAEC-A80AA35AC5B8}_Display.NView) (Version: 146.33 - NVIDIA Corporation) NVIDIA WMI 2.22.0 (HKLM\...\{B2FE1952-0186-46C3-BAEC-A80AA35AC5B8}_Display.NVWMI) (Version: 2.22.0 - NVIDIA Corporation) PotPlayer-64 bit (HKLM\...\PotPlayer64) (Version: 210428 - Kakao Corp.) Pythagoras (HKLM-x32\...\{8993BE81-5C44-45CA-9DBE-3C9D19979152}) (Version: - ) Realtek Audio COM Components (HKLM-x32\...\{2355B503-9B11-4449-861D-1C1748B26320}) (Version: 1.0.2 - Realtek Semiconductor Corp.) Realtek High Definition Audio Driver (HKLM-x32\...\{F132AF7F-7BCA-4EDE-8A7C-958108FE7DBC}) (Version: 6.0.1.7548 - Realtek Semiconductor Corp.) Sentinel Runtime (HKLM-x32\...\{0C1622B1-67B2-47E4-B971-845A538C66D1}) (Version: 8.23.59329.60000 - Thales) VLC media player (HKLM\...\VLC media player) (Version: 3.0.12 - VideoLAN) Winamp (HKLM-x32\...\Winamp) (Version: 5.8 - Winamp SA) Windows PC Health Check (HKLM\...\{B1E7D0FD-7CFE-4E0C-A5DA-0F676499DB91}) (Version: 3.2.2110.14001 - Microsoft Corporation) WinRAR 6.01 (64-bit) (HKLM\...\WinRAR archiver) (Version: 6.01.0 - win.rar GmbH) X7 Oscar Lite (HKLM-x32\...\X7OscarLite) (Version: 20.11.0001 - A4Tech) Packages: ========= Microsoft Solitaire Collection -> C:\Program Files\WindowsApps\Microsoft.MicrosoftSolitaireCollection_4.12.1050.0_x64__8wekyb3d8bbwe [2022-01-12] (Microsoft Studios) [MS Ad] Spotify Music -> C:\Program Files\WindowsApps\SpotifyAB.SpotifyMusic_1.176.447.0_x86__zpdnekdrzrea0 [2022-01-09] (Spotify AB) [Startup Task] ==================== Custom CLSID (Whitelisted): ============== (If an entry is included in the fixlist, it will be removed from the registry. The file will not be moved unless listed separately.) ContextMenuHandlers1: [WinRAR] -> {B41DB860-64E4-11D2-9906-E49FADC173CA} => C:\Program Files\WinRAR\rarext.dll [2021-04-07] (win.rar GmbH -> Alexander Roshal) ContextMenuHandlers1-x32: [WinRAR32] -> {B41DB860-8EE4-11D2-9906-E49FADC173CA} => C:\Program Files\WinRAR\rarext32.dll [2021-04-07] (win.rar GmbH -> Alexander Roshal) ContextMenuHandlers5: [00nView] -> {1E9B04FB-F9E5-4718-997B-B8DA88302A48} => C:\Program Files\NVIDIA Corporation\nview\nvshell.dll [2015-07-29] (NVIDIA Corporation -> ) ContextMenuHandlers5: [igfxcui] -> {3AB1675A-CCFF-11D2-8B20-00A0C93CB1F4} => -> No File ContextMenuHandlers5: [igfxDTCM] -> {9B5F5829-A529-4B12-814A-E81BCB8D93FC} => C:\Windows\system32\igfxDTCM.dll [2017-11-17] (Microsoft Windows Hardware Compatibility Publisher -> Intel Corporation) ContextMenuHandlers5: [NvCplDesktopContext] -> {3D1975AF-48C6-4f8e-A182-BE0E08FA86A9} => C:\Windows\system32\nvshext.dll [2015-07-23] (NVIDIA Corporation -> NVIDIA Corporation) ContextMenuHandlers6: [WinRAR] -> {B41DB860-64E4-11D2-9906-E49FADC173CA} => C:\Program Files\WinRAR\rarext.dll [2021-04-07] (win.rar GmbH -> Alexander Roshal) ContextMenuHandlers6-x32: [WinRAR32] -> {B41DB860-8EE4-11D2-9906-E49FADC173CA} => C:\Program Files\WinRAR\rarext32.dll [2021-04-07] (win.rar GmbH -> Alexander Roshal) ==================== Codecs (Whitelisted) ==================== ==================== Shortcuts & WMI ======================== (The entries could be listed to be restored or removed.) Shortcut: C:\Users\User-33TL\Desktop\Frozen Throne - Пряк път.lnk -> D:\Warcraft IIIii\Frozen Throne.exe (Blizzard Entertainment) <==== Cyrillic ==================== Loaded Modules (Whitelisted) ============= 2021-11-15 17:25 - 2021-11-15 17:16 - 000967168 _____ () [File not signed] [File is in use] C:\Program Files (x86)\Innova\4game2.0\bin\CefSharp.BrowserSubprocess.Core.dll 2021-11-15 17:25 - 2021-11-15 17:24 - 001445888 _____ () [File not signed] [File is in use] C:\Program Files (x86)\Innova\4game2.0\bin\CefSharp.Core.Runtime.dll 2021-11-15 17:25 - 2021-11-15 17:19 - 000014848 _____ () [File not signed] [File is in use] C:\Program Files (x86)\Innova\4game2.0\bin\Innova.Launcher.Shared.Localization.dll 2021-11-15 17:25 - 2021-11-15 17:23 - 000010752 _____ () [File not signed] [File is in use] C:\Program Files (x86)\Innova\4game2.0\bin\Innova.Launcher.Shared.Logging.dll 2021-11-15 17:25 - 2021-11-15 17:24 - 000014848 _____ () [File not signed] [File is in use] C:\Program Files (x86)\Innova\4game2.0\bin\Innova.Launcher.Shared.Tracking.dll 2021-11-15 17:25 - 2021-11-15 17:23 - 000013312 _____ () [File not signed] [File is in use] C:\Program Files (x86)\Innova\4game2.0\bin\Innova.Launcher.Tracking.dll 2021-11-15 17:25 - 2021-11-15 17:12 - 017782784 _____ () [File not signed] [File is in use] C:\Program Files (x86)\Innova\4game2.0\bin\Innova.Launcher.Updater.Core.dll 2021-11-15 17:25 - 2021-11-15 17:09 - 120004608 _____ () [File not signed] C:\Program Files (x86)\Innova\4game2.0\bin\libcef.dll 2021-11-15 17:25 - 2021-11-15 17:23 - 000328704 _____ () [File not signed] C:\Program Files (x86)\Innova\4game2.0\bin\libegl.dll 2021-11-15 17:25 - 2021-11-15 17:14 - 005571072 _____ () [File not signed] C:\Program Files (x86)\Innova\4game2.0\bin\libglesv2.dll 2021-11-17 19:56 - 2017-04-19 11:27 - 003852800 ____N () [File not signed] C:\Program Files (x86)\X7OscarLite\X7OscarLite\Data\RES\Forms\Internet_Advertisement\Internet_Advertisement_DLL.dll 2021-11-15 17:25 - 2021-11-15 17:19 - 000269312 _____ (App vNext) [File not signed] [File is in use] C:\Program Files (x86)\Innova\4game2.0\bin\Polly.dll 2021-05-05 09:55 - 2021-11-15 17:16 - 000082944 _____ (Bernhard Millauer,Uwe Mayer, Konrad Mattheis) [File not signed] [File is in use] C:\Program Files (x86)\Innova\4game2.0\bin\WPFLocalizeExtension.dll 2021-11-15 17:25 - 2021-11-15 17:19 - 000093184 _____ (hardcodet.net) [File not signed] [File is in use] C:\Program Files (x86)\Innova\4game2.0\bin\Hardcodet.Wpf.TaskbarNotification.dll 2021-11-15 17:25 - 2021-11-15 17:15 - 000198144 _____ (ICSharpCode) [File not signed] [File is in use] C:\Program Files (x86)\Innova\4game2.0\bin\ICSharpCode.SharpZipLib.dll 2021-11-15 17:25 - 2021-11-15 17:16 - 000167424 _____ (Innova Co. SARL) [File not signed] [File is in use] C:\Program Files (x86)\Innova\4game2.0\bin\Innova.Launcher.Core.dll 2021-11-15 17:25 - 2021-11-15 17:24 - 000592896 _____ (Innova Co. SARL) [File not signed] [File is in use] C:\Program Files (x86)\Innova\4game2.0\bin\Innova.Launcher.dll 2021-11-15 17:25 - 2021-11-15 17:24 - 000114176 _____ (Innova Co. SARL) [File not signed] [File is in use] C:\Program Files (x86)\Innova\4game2.0\bin\Innova.Launcher.Shared.dll 2021-11-15 17:25 - 2021-11-15 17:24 - 000187904 _____ (Innova Co. SARL) [File not signed] [File is in use] C:\Program Files (x86)\Innova\4game2.0\bin\Innova.Launcher.UI.dll 2021-11-15 17:25 - 2021-11-15 17:24 - 000287744 _____ (Jimmy Bogard) [File not signed] [File is in use] C:\Program Files (x86)\Innova\4game2.0\bin\AutoMapper.dll 2021-11-15 17:25 - 2021-11-15 17:24 - 000361984 _____ (Maurício David) [File not signed] [File is in use] C:\Program Files (x86)\Innova\4game2.0\bin\LiteDB.dll 2021-11-15 17:25 - 2021-11-15 17:24 - 000010240 _____ (Microsoft.Practices.ServiceLocation) [File not signed] [File is in use] C:\Program Files (x86)\Innova\4game2.0\bin\CommonServiceLocator.dll 2021-11-15 17:25 - 2021-11-15 17:23 - 000815104 _____ (NLog) [File not signed] [File is in use] C:\Program Files (x86)\Innova\4game2.0\bin\NLog.dll 2021-12-21 19:15 - 2015-07-23 02:44 - 001171872 _____ (NVIDIA Corporation PE Sign v2014 -> NVIDIA Corporation) [File not signed] C:\Program Files (x86)\NVIDIA Corporation\3D Vision\nvSCPAPI.dll 2021-12-21 19:15 - 2015-07-23 02:44 - 001367232 _____ (NVIDIA Corporation PE Sign v2014 -> NVIDIA Corporation) [File not signed] C:\Program Files (x86)\NVIDIA Corporation\3D Vision\nvSCPAPI64.dll 2021-11-15 17:25 - 2021-11-15 17:23 - 000678400 _____ (Roland Pheasant) [File not signed] [File is in use] C:\Program Files (x86)\Innova\4game2.0\bin\DynamicData.dll 2021-11-15 17:25 - 2021-11-15 17:24 - 000030208 _____ (The CefSharp Authors) [File not signed] [File is in use] C:\Program Files (x86)\Innova\4game2.0\bin\CefSharp.Core.dll 2021-11-15 17:25 - 2021-11-15 17:16 - 001032192 _____ (The CefSharp Authors) [File not signed] [File is in use] C:\Program Files (x86)\Innova\4game2.0\bin\CefSharp.dll 2021-11-15 17:25 - 2021-11-15 17:24 - 000032768 _____ (The CefSharp Authors) [File not signed] [File is in use] C:\Program Files (x86)\Innova\4game2.0\bin\CefSharp.WinForms.dll 2021-11-15 17:25 - 2021-11-15 17:24 - 000879616 _____ (The Chromium Authors) [File not signed] C:\Program Files (x86)\Innova\4game2.0\bin\chrome_elf.dll 2021-05-05 09:55 - 2021-11-15 17:24 - 000043008 _____ (Thomas Levesque) [File not signed] [File is in use] C:\Program Files (x86)\Innova\4game2.0\bin\WpfAnimatedGif.dll 2021-05-05 09:55 - 2021-11-15 17:24 - 000064512 _____ (Unity Open Source Project) [File not signed] [File is in use] C:\Program Files (x86)\Innova\4game2.0\bin\Unity.Abstractions.dll 2021-05-05 09:55 - 2021-11-15 17:24 - 000148480 _____ (Unity Open Source Project) [File not signed] [File is in use] C:\Program Files (x86)\Innova\4game2.0\bin\Unity.Container.dll 2021-05-05 09:55 - 2021-11-15 17:24 - 000037376 _____ (Uwe Mayer,Konrad Mattheis,Bernhard Millauer) [File not signed] [File is in use] C:\Program Files (x86)\Innova\4game2.0\bin\XAMLMarkupExtensions.dll ==================== Alternate Data Streams (Whitelisted) ======== ==================== Safe Mode (Whitelisted) ================== ==================== Association (Whitelisted) ================= ==================== Internet Explorer (Whitelisted) ========== ==================== Hosts content: ========================= (If needed Hosts: directive could be included in the fixlist to reset Hosts.) 2019-12-07 11:14 - 2019-12-07 11:12 - 000000824 _____ C:\Windows\system32\drivers\etc\hosts ==================== Other Areas =========================== (Currently there is no automatic fix for this section.) HKLM\System\CurrentControlSet\Control\Session Manager\Environment\\Path -> C:\Program Files (x86)\Intel\iCLS Client\;C:\Program Files\Intel\iCLS Client\;%SystemRoot%\system32;%SystemRoot%;%SystemRoot%\System32\Wbem;%SYSTEMROOT%\System32\WindowsPowerShell\v1.0\;%SYSTEMROOT%\System32\OpenSSH\;C:\Program Files (x86)\Intel\Intel(R) Management Engine Components\DAL;C:\Program Files\Intel\Intel(R) Management Engine Components\DAL;C:\Program Files (x86)\Intel\Intel(R) Management Engine Components\IPT;C:\Program Files\Intel\Intel(R) Management Engine Components\IPT HKU\S-1-5-21-4171439222-1843728066-1652194855-1001\Control Panel\Desktop\\Wallpaper -> C:\Windows\Web\Wallpaper\Theme2\img12.jpg DNS Servers: 45.144.64.151 - 185.204.2.172 HKLM\SOFTWARE\Microsoft\Windows\CurrentVersion\Policies\System => (ConsentPromptBehaviorAdmin: 0) (ConsentPromptBehaviorUser: 3) (EnableLUA: 1) HKLM\SOFTWARE\Microsoft\Windows\CurrentVersion\Explorer => (SmartScreenEnabled: ) Windows Firewall is disabled. ==================== MSCONFIG/TASK MANAGER disabled items == (If an entry is included in the fixlist, it will be removed.) HKLM\...\StartupApproved\Run: => "SecurityHealth" HKU\S-1-5-21-4171439222-1843728066-1652194855-1001\...\StartupApproved\Run: => "OneDrive" ==================== FirewallRules (Whitelisted) ================ (If an entry is included in the fixlist, it will be removed from the registry. The file will not be moved unless listed separately.) FirewallRules: [{90070B7E-AF8B-4431-A027-CCF5935BB67A}] => (Allow) C:\Program Files (x86)\Winamp\winamp.exe (Winamp SA -> Winamp SA) FirewallRules: [{0042CCE5-9C68-4E54-99FE-FE61DDB37B5E}] => (Allow) C:\Program Files (x86)\Winamp\winamp.exe (Winamp SA -> Winamp SA) FirewallRules: [{4C9146B5-85F9-45ED-9F8A-CCB75AD2249C}] => (Allow) C:\Program Files\Mozilla Firefox\firefox.exe (Mozilla Corporation -> Mozilla Corporation) FirewallRules: [{ABA7E619-C59C-4B8C-9923-D2D8118F540B}] => (Allow) C:\Program Files\Mozilla Firefox\firefox.exe (Mozilla Corporation -> Mozilla Corporation) FirewallRules: [{3648BB4C-4CAA-4EAC-BAAF-C7C04AF4A1AD}] => (Allow) C:\Program Files (x86)\Common Files\Aladdin Shared\HASP\hasplms.exe (Thales DIS CPL USA, Inc. -> Thales Group) FirewallRules: [{15E88E9C-A7A9-4439-875C-A429950FE0C4}] => (Allow) C:\Program Files\WindowsApps\Microsoft.SkypeApp_15.79.95.0_x86__kzf8qxf38zg5c\Skype\Skype.exe (Skype Software Sarl -> Skype Technologies S.A.) FirewallRules: [{57D3B70B-1546-4A31-A3D6-1B4E8586092F}] => (Allow) C:\Program Files\WindowsApps\Microsoft.SkypeApp_15.79.95.0_x86__kzf8qxf38zg5c\Skype\Skype.exe (Skype Software Sarl -> Skype Technologies S.A.) FirewallRules: [{7050BC2B-37E0-4448-A7C1-E57CF3BD9D18}] => (Allow) C:\Program Files\WindowsApps\Microsoft.SkypeApp_15.79.95.0_x86__kzf8qxf38zg5c\Skype\Skype.exe (Skype Software Sarl -> Skype Technologies S.A.) FirewallRules: [{E2A67435-2CA5-4647-9A38-B837A7F1314B}] => (Allow) C:\Program Files\WindowsApps\Microsoft.SkypeApp_15.79.95.0_x86__kzf8qxf38zg5c\Skype\Skype.exe (Skype Software Sarl -> Skype Technologies S.A.) FirewallRules: [{DDD5A556-E08B-4A7D-9532-34A7A8272133}] => (Allow) C:\Program Files\WindowsApps\SpotifyAB.SpotifyMusic_1.176.447.0_x86__zpdnekdrzrea0\Spotify.exe (Spotify AB -> Spotify Ltd) FirewallRules: [{DA332307-F020-4D8C-9B70-2AA02A213B15}] => (Allow) C:\Program Files\WindowsApps\SpotifyAB.SpotifyMusic_1.176.447.0_x86__zpdnekdrzrea0\Spotify.exe (Spotify AB -> Spotify Ltd) FirewallRules: [{01B88CD3-513B-4514-979D-D6A2BC66B37B}] => (Allow) C:\Program Files\WindowsApps\SpotifyAB.SpotifyMusic_1.176.447.0_x86__zpdnekdrzrea0\Spotify.exe (Spotify AB -> Spotify Ltd) FirewallRules: [{C0F7BE71-31B7-4F99-9D7E-19CC591CC814}] => (Allow) C:\Program Files\WindowsApps\SpotifyAB.SpotifyMusic_1.176.447.0_x86__zpdnekdrzrea0\Spotify.exe (Spotify AB -> Spotify Ltd) FirewallRules: [{7723F50A-B9FA-422F-A8B5-C5CE113314B7}] => (Allow) C:\Program Files\WindowsApps\SpotifyAB.SpotifyMusic_1.176.447.0_x86__zpdnekdrzrea0\Spotify.exe (Spotify AB -> Spotify Ltd) FirewallRules: [{725BA095-2E94-4F46-917A-029F430841C7}] => (Allow) C:\Program Files\WindowsApps\SpotifyAB.SpotifyMusic_1.176.447.0_x86__zpdnekdrzrea0\Spotify.exe (Spotify AB -> Spotify Ltd) FirewallRules: [{5B8DC1B9-78B2-4B7A-8462-C3DEE98DBBD2}] => (Allow) C:\Program Files\WindowsApps\SpotifyAB.SpotifyMusic_1.176.447.0_x86__zpdnekdrzrea0\Spotify.exe (Spotify AB -> Spotify Ltd) FirewallRules: [{2C77E269-B5E5-438F-B214-F3A984DE9681}] => (Allow) C:\Program Files\WindowsApps\SpotifyAB.SpotifyMusic_1.176.447.0_x86__zpdnekdrzrea0\Spotify.exe (Spotify AB -> Spotify Ltd) FirewallRules: [{84BE2362-4E06-4312-B7B4-B69CF13C1BAC}] => (Allow) C:\Program Files\Google\Chrome\Application\chrome.exe (Google LLC -> Google LLC) FirewallRules: [{C6C894BA-6612-46A9-980A-FBBAE0BB2389}] => (Allow) C:\Program Files (x86)\AnyDesk\AnyDesk.exe (philandro Software GmbH -> philandro Software GmbH) FirewallRules: [{278218F5-1935-4961-853D-4BB8074E9BB9}] => (Allow) C:\Program Files (x86)\AnyDesk\AnyDesk.exe (philandro Software GmbH -> philandro Software GmbH) FirewallRules: [{CBE54583-64F0-4A95-BE8D-DDF929D2CC78}] => (Allow) C:\Program Files (x86)\AnyDesk\AnyDesk.exe (philandro Software GmbH -> philandro Software GmbH) FirewallRules: [{84D899DE-DCDF-4FC5-B727-3272309EC7FF}] => (Allow) C:\Program Files (x86)\AnyDesk\AnyDesk.exe (philandro Software GmbH -> philandro Software GmbH) FirewallRules: [{3A69F623-CE87-4600-BBC5-B20E95ECBE29}] => (Allow) C:\Program Files (x86)\AnyDesk\AnyDesk.exe (philandro Software GmbH -> philandro Software GmbH) FirewallRules: [{84A47DE7-93E5-4AEA-B5D6-5EF580454332}] => (Allow) C:\Program Files (x86)\AnyDesk\AnyDesk.exe (philandro Software GmbH -> philandro Software GmbH) ==================== Restore Points ========================= 21-12-2021 19:26:53 Windows Modules Installer 29-12-2021 19:34:15 Scheduled Checkpoint 09-01-2022 21:45:45 Scheduled Checkpoint ==================== Faulty Device Manager Devices ============ Name: Microsoft PS/2 Mouse Description: Microsoft PS/2 Mouse Class Guid: {4d36e96f-e325-11ce-bfc1-08002be10318} Manufacturer: Microsoft Service: i8042prt Problem: : This device is not present, is not working properly, or does not have all its drivers installed. (Code 24) Resolution: The device is installed incorrectly. The problem could be a hardware failure, or a new driver might be needed. Devices stay in this state if they have been prepared for removal. After you remove the device, this error disappears.Remove the device, and this error should be resolved. Name: Standard PS/2 Keyboard Description: Standard PS/2 Keyboard Class Guid: {4d36e96b-e325-11ce-bfc1-08002be10318} Manufacturer: (Standard keyboards) Service: i8042prt Problem: : This device is not present, is not working properly, or does not have all its drivers installed. (Code 24) Resolution: The device is installed incorrectly. The problem could be a hardware failure, or a new driver might be needed. Devices stay in this state if they have been prepared for removal. After you remove the device, this error disappears.Remove the device, and this error should be resolved. ==================== Event log errors: ======================== Application errors: ================== Error: (01/12/2022 11:45:26 AM) (Source: VSS) (EventID: 8193) (User: ) Description: Volume Shadow Copy Service error: Unexpected error calling routine CoCreateInstance. hr = 0x8007045b, A system shutdown is in progress. . Error: (01/12/2022 11:45:26 AM) (Source: VSS) (EventID: 13) (User: ) Description: Volume Shadow Copy Service information: The COM Server with CLSID {4e14fba2-2e22-11d1-9964-00c04fbbb345} and name CEventSystem cannot be started. [0x8007045b, A system shutdown is in progress. ] Error: (12/21/2021 07:17:10 PM) (Source: Software Protection Platform Service) (EventID: 8198) (User: ) Description: License Activation (slui.exe) failed with the following error code: hr=0x803F7001 Command-line arguments: RuleId=3482d82e-ca2c-4e1f-8864-da0267b484b2;Action=AutoActivate;AppId=55c92734-d682-4d71-983e-d6ec3f16059f;SkuId=4de7cb65-cdf1-4de9-8ae8-e3cce27b9f2c;NotificationInterval=1440;Trigger=TimerEvent Error: (11/03/2021 06:33:49 PM) (Source: MsiInstaller) (EventID: 11500) (User: DESKTOP-J4MB6U6) Description: Product: Sentinel Runtime -- Error 1500. Another installation is in progress. You must complete that installation before continuing this one. Error: (06/04/2021 09:32:08 PM) (Source: VSS) (EventID: 13) (User: ) Description: Volume Shadow Copy Service information: The COM Server with CLSID {4e14fba2-2e22-11d1-9964-00c04fbbb345} and name CEventSystem cannot be started. [0x8007045b, A system shutdown is in progress. ] Error: (06/04/2021 09:27:02 PM) (Source: Dell-System Update) (EventID: 3720) (User: ) Description: Update Failure User: User-33TL Package: DELLMUP.exe 1.0.0.20 Description: DELL MUP Package version:6.0.1.6086 Realtek High Definition Auido - Previous version: 6.0.1.6086, New version: 6.0.1.6086 Log file: C:\Dell\UpdatePackage\log\DELLMUP.log Exit code = 1603 (Error) Error: (06/02/2021 04:55:52 PM) (Source: Firefox Default Browser Agent) (EventID: 12007) (User: ) Description: Event-ID 12007 Error: (06/02/2021 04:55:52 PM) (Source: Firefox Default Browser Agent) (EventID: 0) (User: ) Description: Event-ID 0 System errors: ============= Error: (01/12/2022 11:57:10 PM) (Source: Service Control Manager) (EventID: 7000) (User: ) Description: Услуга eapihdrv не може да бъде стартирана поради следната грешка: This driver has been blocked from loading Error: (01/12/2022 11:57:10 PM) (Source: Application Popup) (EventID: 1060) (User: ) Description: \??\C:\Users\USER-3~1\AppData\Local\Temp\ehdrv.sys Error: (01/12/2022 11:57:09 PM) (Source: Application Popup) (EventID: 1060) (User: ) Description: \??\C:\Users\USER-3~1\AppData\Local\Temp\ehdrv.sys Error: (01/12/2022 11:57:09 PM) (Source: Service Control Manager) (EventID: 7000) (User: ) Description: Услуга eapihdrv не може да бъде стартирана поради следната грешка: This driver has been blocked from loading Error: (01/12/2022 11:57:09 PM) (Source: Service Control Manager) (EventID: 7000) (User: ) Description: Услуга eapihdrv не може да бъде стартирана поради следната грешка: This driver has been blocked from loading Error: (01/12/2022 11:57:09 PM) (Source: Application Popup) (EventID: 1060) (User: ) Description: \??\C:\Users\USER-3~1\AppData\Local\Temp\ehdrv.sys Error: (01/12/2022 11:57:09 PM) (Source: Service Control Manager) (EventID: 7000) (User: ) Description: Услуга eapihdrv не може да бъде стартирана поради следната грешка: This driver has been blocked from loading Error: (01/12/2022 11:57:09 PM) (Source: Application Popup) (EventID: 1060) (User: ) Description: \??\C:\Users\USER-3~1\AppData\Local\Temp\ehdrv.sys Windows Defender: ================ Date: 2022-01-12 21:44:38 Description: Microsoft Defender Antivirus scan has been stopped before completion. Scan Type: Antimalware Scan Parameters: Quick Scan Date: 2022-01-12 09:48:42 Description: Microsoft Defender Antivirus scan has been stopped before completion. Scan Type: Antimalware Scan Parameters: Quick Scan Date: 2022-01-10 23:39:29 Description: Microsoft Defender Antivirus scan has been stopped before completion. Scan Type: Antimalware Scan Parameters: Quick Scan Date: 2022-01-07 19:02:43 Description: Microsoft Defender Antivirus scan has been stopped before completion. Scan Type: Antimalware Scan Parameters: Quick Scan Date: 2022-01-06 18:43:46 Description: Microsoft Defender Antivirus scan has been stopped before completion. Scan Type: Antimalware Scan Parameters: Quick Scan ==================== Memory info =========================== BIOS: Hewlett-Packard L51 v01.42 11/17/2014 Motherboard: Hewlett-Packard 1905 Processor: Intel(R) Core(TM) i7-4790 CPU @ 3.60GHz Percentage of memory in use: 48% Total physical RAM: 16136.86 MB Available physical RAM: 8266.98 MB Total Virtual: 18568.86 MB Available Virtual: 10653.93 MB ==================== Drives ================================ Drive 😄 () (Fixed) (Total:124.8 GB) (Free:75.87 GB) NTFS Drive d: () (Fixed) (Total:98.23 GB) (Free:68.72 GB) NTFS \\?\Volume{5dcd099d-0000-0000-0000-100000000000}\ (System Reserved) (Fixed) (Total:0.05 GB) (Free:0.02 GB) NTFS \\?\Volume{5dcd099d-0000-0000-0000-30c537000000}\ () (Fixed) (Total:0.49 GB) (Free:0.08 GB) NTFS ==================== MBR & Partition Table ==================== ========================================================== Disk: 0 (MBR Code: Windows 7/8/10) (Size: 223.6 GB) (Disk ID: 5DCD099D) Partition 1: (Active) - (Size=50 MB) - (Type=07 NTFS) Partition 2: (Not Active) - (Size=124.8 GB) - (Type=07 NTFS) Partition 3: (Not Active) - (Size=98.2 GB) - (Type=0F Extended) Partition 4: (Not Active) - (Size=499 MB) - (Type=27) ==================== End of Addition.txt =======================


Разглеждащи това в момента 0
- Няма регистрирани потребители разглеждащи тази страница.